
Blending AI, Blockchain & Data to solve real-world problems Building homa app to help you run your personal wealth as a system
Lagos, Nigeria
Joined October 2010
- Tweets10.4K
- Following2.7K
- Followers851
- Likes2K


Pinned Tweet
"The amount you are loved — not your wealth or accomplishments — is the ultimate measure of success in life."
@WarrenBuffett
Hi .@utexocom, we are integrating the WDK RGB Lightning stack into an our app for agentic commerce on Bitcoin.
In our pinned implementation, ordinary RGB Lightning payments require at least 3,000,000 msat (3,000 sats) alongside the RGB asset. Our understanding is that this supports enforceable RGB recovery if the channel closes unilaterally.
Could you confirm whether that BTC permanently transfers to the recipient, or whether a supported recovery mechanism exists?
This creates a challenge for small merchant purchases: the buyer intends to pay the asset price without an additional BTC transfer.
Is there a supported approach for:
- Atomically returning the BTC carrier after successful RGB settlement?
- Having an LSP or merchant sponsor the carrier liquidity?
- Using receiver-funded collateral while preserving unilateral-close security?
We wondered whether a receiver-provided UTXO could help, but understand that Lightning commitment outputs may require a different mechanism.
Is the 3,000-sat floor configurable safely, or would carrier-neutral settlement require protocol changes?
We want to preserve Bitcoin enforceability and RGB ownership guarantees.
everything works as expected but that 3000 sats on every RGB transfers is a real blocker to our use case.
hope to hear your take
good sounds

CHINEKE ft. @BustaRhymes OUT NOW.
directed by me
THE BRIDGE. OUT NOW. 🥹 full vid on YT
To share a song called “Chineke” w a giant like Busta Rhymes is monuMINTal in every sense. I carry deep reverence for the doors he’s opened & the culture he’s moved.


Hey @utexocom - we hit a reproducible Android native-addon loading issue while testing "@utexo/[email protected]" for an embedded RGB Lightning wallet.
The release APK builds and launches, and contains:
"lib/x86_64/libbare-channel.5.3.0.so"
The WDK worklet manifest correctly resolves:
"linked:libbare-channel.5.3.0.so"
But the Bare worklet aborts before WDK/wallet initialization with:
"ADDON_NOT_FOUND: Cannot find addon '.' imported from .../bare-channel/binding.js"
We also reproduced the same class of addon-resolution failure with Bare Kit 0.14.5 ("bare-type").
Environment:
• Android API 36 x86_64
• "wdk-rgb-lightning" 0.1.0-beta.15
• "rgb-lightning-node-bare" 0.1.0-beta.15
• WDK RN Core 1.0.0-beta.21
• Bare Kit 0.15.5
Happy to share the minimal reproduction, APK ABI listing, worklet manifest, and focused logs if useful.

very educative

Bitcoin Hardware and Soverignty Club: Schnorr Signatures Explained: Fiat-Shamir & Nonce Reuse | The Cryptographic Trick Behind Bitcoin Signatures | #Bitcoineducation xitter.cf/i/broadcasts/1PKqrNkDg…
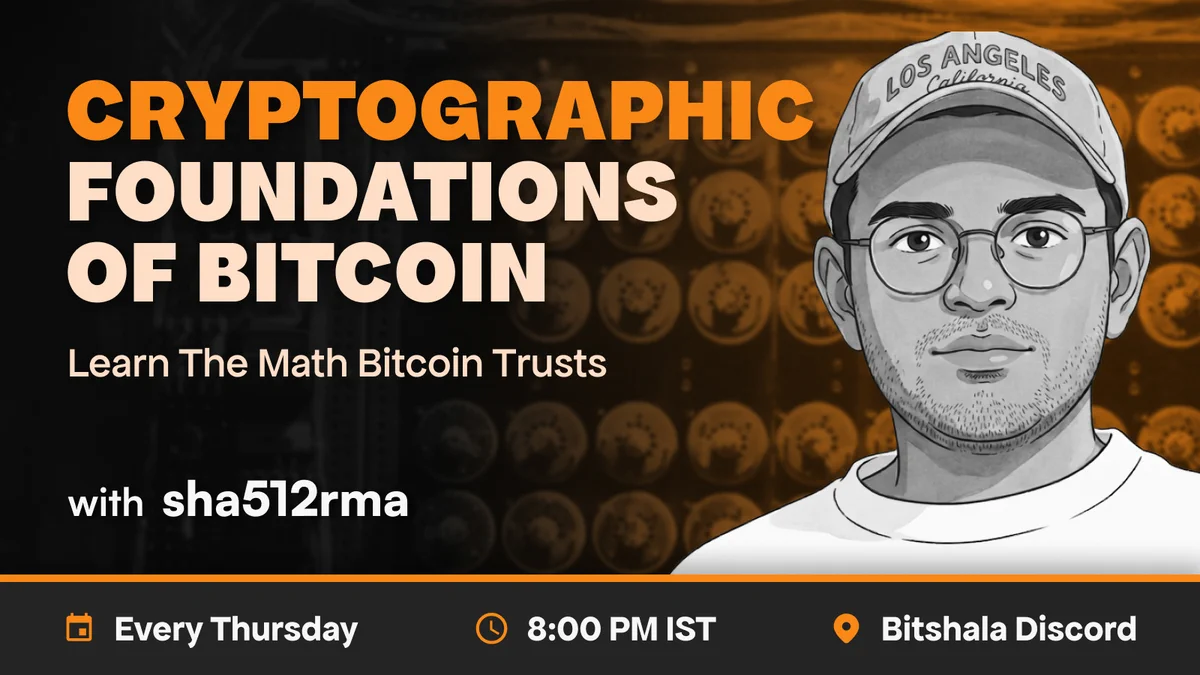
Yesterday during our Bitshala cryptography session, I realized I had confused ECC/ECDLP, the cryptographic framework built around elliptic curves and the hard discrete-log problem, with ECDSA, the digital-signature algorithm built on top of that framework.
The confusion came from the notation around k. In the ECC/ECDLP context, the secret scalar in an expression like k can represent the private key. But in ECDSA, the long-term private key is usually written as d, while k is a temporary per-signature nonce used when generating a signature.
That distinction matters a lot. If the temporary ECDSA k-value is exposed, reused, or poorly generated, the long-term private key d can potentially be recovered. So both the private key and the per-signature nonce must be handled with extreme care.
The security of the wallet we are building is too important to treat these details casually. We have users waiting on us, and we need to make sure what we ship is not only functional, but cryptographically sound.
#bitmask #awakening


JS has 1 string. Rust has 2.
String = owned, heap, growable
&str = borrowed, view, fixed
Params = &str (zero-cost)
Ownership = String
That's it. That's the mental model. 🦀
A perfect token can still represent a terrible investment.
Every RWA token has 3 layers:
🟠 Asset — real-world value
🔵 Legal — your actual rights
🟣 Token — on-chain record
Break any one = failure.
Blockchain proves you own the token.
Law determines what that means.
Audit all three.
Asset Tokenisation is often explained like this:
Asset → Blockchain → Token
That skips the most important layer.
The better model is:
Asset → Legal Rights → Token
The token is not the asset.
It represents a claim, right, or economic interest tied to it.
That legal bridge is what makes RWA tokenisation meaningful.
#RWA #Tokenisation #DigitalAssets #Fintech
Your card says “Approved” in seconds.
But that doesn’t mean the merchant has received the money.
A card payment still moves through:
Authorization → Clearing → Settlement → Merchant Funding
Banks don’t settle every transaction individually. Payments are cleared, obligations are calculated, and institutions settle their net positions.
So next time you see “Approved”, remember:
The payment is approved.
The money is still moving.
#Fintech #Payments #Banking
The fear is real, but is just math capable of doing many things, but it can be contained, one it is constraint, it runs on a computer plus it's networks, so we can tame it using cryptography with sufficient day/night entropy, ai can only call or do what it is supposed to do and gated accordingly with using math as well

Math is capable of many things and he is right, but AI should be gated with cryptography with sufficient day/night entropy.
AI should be allowed to advanced human civilization but gated accordingly
This quoted post is unavailable.
i am actually help some insight; for Bitcoin wallet developers, how do you ensure sync is faster, like every import using the seed does not need to start afresh, is it ideal to saved and pickup on next wallet import. new wallet can be tolerated but reimporting the wallet should not take more than 2 seconds using cached memory.
what to hear your take
just use kit to understand concept you are confused about best case scenario let it generate the code while you inspect

The creator of the C++ programming language, Bjarne Stroustrup, says AI-generated code is not successful and calls the idea of using natural language as a programming language idiotic.
He says humans will still write code and use abstraction.
According to him, AI generates bloated code with more bugs and security holes, making it hard to validate.
He also says the senior developers needed to validate it are starting to retire because they don’t want to deal with validating something that changes every time you change your prompt.
He goes on to say that AI is not good at writing safety-critical or performance-critical code: “Now, let’s say that 70 or 80% of the world’s code doesn’t fit that pattern, but it’s that 10, 20% of the code that I’m interested in.”
