

Security Researcher & Dark Net Pest, no longer active on X: https://xitter.cf/t.co/GeZ7D3YQUb
7.0 pH water
Joined September 2023
- Tweets35
- Following38
- Followers339
- Likes104



I'm moving to Bluesky because this platform is total trash: bsky.app/profile/htmalgae.bs…
If you haven't seen github.com/Casualtek/Ransomc… yet, go check it out.

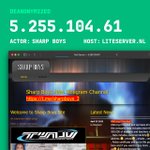
#SharpBoys leaked their #Cloudflare-protected origin IP today. Side note – They should win a web design award. #ransomware #infosec #originleak

"Hulk" really hurt #Donutleaks' feelings. This #ransomware gang is back at it again with another dramatic "appeal" on their blog 🍿

htmalgae retweeted

Someone on the Lorenz ransomware crew is having a very bad day after being called out for misconfiguring an Apache server leading to leaked contact data everywhere....
The Reg's @ConnorLBJones spoke to @htmalgae, who spotted the leak reg.cx/4a3B
"Sony Hackers" #RansomedVC can't get it together recently. 🧵They decided to switch their site to WordPress today after setting up a new VPS with @FrantechCA's BuyVM (PONYNET).


#Donutleaks #ransomware having a little bit of drama right now – The irony is palpable.

🫗#Metaencryptor's claimed 15 years experience isn't enough to hide their hidden service IP: 31.14.41[.]137. Another happy @serverroomnet customer!


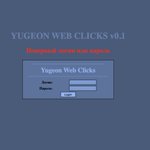
The flatfile database is accessible at threeamkelxicjsaf2czjyz2lc4q3ngqkxhhlexyfcp2o6raw4rphyad[.]onion/cl/inc/clicks.dat, and yes, it's XSS vuln galore.

#Snatch ransomware group's webserver access logs exposed ✅ krebsonsecurity.com/2023/09/…