
Security Researcher, System Programmer and Part-Time Garbage Collector
Austin, TX
Joined May 2009
- Tweets3.6K
- Following544
- Followers1.3K
- Likes466



Mohamed Saher retweeted
Austin hackers, let's gather for a night of lectures, libations, and BBQ on Wednesday June 5th. Thanks to our corporate sponsors tagged in the photo for fueling the evening. Limited capacity, register at: eventbrite.com/e/austin-hack… Looking forward to catching up with everyone.

Mohamed Saher retweeted
New blog entry: An Abstract Interpretation-Based Deobfuscation Plugin for Ghidra msreverseengineering.com/blo…
Mohamed Saher retweeted
Translate x86_64 and ARM binaries to LLVM IR github.com/Microsoft/llvm-mc…

Mohamed Saher retweeted
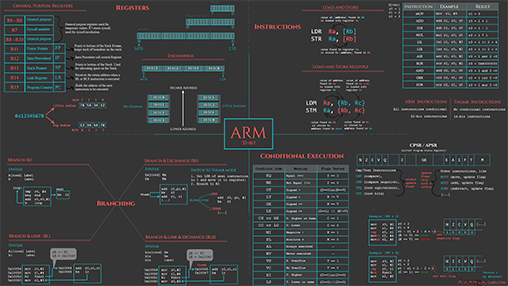
As I was laying in bed with a cold yesterday, I felt like I should use that time to create a cute little cheatsheet on ARM assembly basics for you guys. Enjoy! 🖤
azeria-labs.com/assembly-bas…
Mohamed Saher retweeted

My Metasploitable 3 CTF Start to Finish walk-through of all the challenges including CTF setup/prep, and alternative solutions: docs.google.com/document/d/1… (Now downloadable/printable/copy allowed)

Mohamed Saher retweeted

The world could use a full C/C++ example of MSFT's Antimalware Scan Interface (AMSI), so here's one that I used in my lab: goo.gl/72FjGr


Mohamed Saher retweeted

OMG, look what I got :-) Simply add a registry entry value (UAC free) on windows 10 1803, then we can make our vbscript or jscript files bypass AMSI PERMANENTLY! Isn't it so easy? or is it an Easter egg Microsoft left to us? :-( @tiraniddo @bohops @subTee @Oddvarmoe @domchell


Mohamed Saher retweeted

[DEMO] Recovering a PE with damaged headers with #PEsieve: youtube.com/watch?v=dFJcGYUF… (example: #PrincessLocker) - I am currently testing this feature, if you want to help in tests, pls check the "Latest builds": github.com/hasherezade/pe-si…

Mohamed Saher retweeted
Learn Verilog for #fpga by taking interactive exams in your browser wp.me/pk3lN-1mWS
Mohamed Saher retweeted
some possible career goals jvns.ca/blog/2018/09/30/some…
Mohamed Saher retweeted

Just released a new #mimikatz version to support Windows 10 1803 to bypass the Credential Guard authentication chain
Reminder: your passwords/keys are not in the secure world... only its storage **after** authentication!
@reni_ni this version is for you 😉
github.com/gentilkiwi/mimika…

Mohamed Saher retweeted

Linux kernel userfaultfd+setxattr heap spray writeup @bevxcon cyseclabs.com/blog/linux-ker…

Mohamed Saher retweeted

This report burns a lot of cool tricks, this and CoreTrust will probably make user-only sbox escape and sig bypass significantly harder! github.com/bazad/blanket

Mohamed Saher retweeted
Abusing the COM Registry Structure (Part 2): Hijacking & Loading Techniques bohops.com/2018/08/18/abusin…

Mohamed Saher retweeted
Windows 10 19H1 introduces system call entry/exit callbacks, the ability to consume real-time ETW events from kernel-mode (with an inline callback and not the usual shenanigans you do in user-mode) and an equivalent kprobe-like feature called trace points. alex-ionescu.com/?p=358

Mohamed Saher retweeted

ZeroNights 2018 CFP is open! (November 20-21, Saint-Petersburg, Russia) Please send your submissions 01x.cfp.zeronights.ru/zn2018…

Mohamed Saher retweeted

Finding and exploiting RCE (CVE-2018-0387) in Cisco Spark (WebEx Teams) messanger: asintsov.blogspot.com/2018/0…


Mohamed Saher retweeted
Fred from @tetrane just gave me an exciting demo of their product REVEN (e.g. blog.tetrane.com/2016/11/rev…). It seems extremely useful for dynamic analysis (particularly vulnerability analysis). I look forward to playing with it more in the future and I hope they succeed!