

Kashmiri in 🇸🇬 … Application/API Security Architect… Travel, Food, F1 and Aviation interests me… When life throws me a virus, I throw it back harder…
Singapore
Joined July 2017
- Tweets11.4K
- Following198
- Followers263
- Likes9.2K



Pinned Tweet
Not just a mosque, but a legacy of faith, patience, and promise. Masjid Al-Aqsa. Alhamdulillah…


Fouad Farooq retweeted

The Palestinian ambassador speaks about genocide of Palestinians and reminds people of the history, the reality of terror, and the global support for genocide.
Neki kar, media pe daal…

#Watch : SSP Traffic City Sgr Bisma Qazi leads a massive drive at Rajbagh Srinagar against traffic rules violations. She also counselled minors and urged their parents to keep watch on their wards so that precious lives are saved.
Reports: Abid Bashir
Camera and Edit: Musiab Fayaz
@SSPTFCSGR @Traffic_hqrs


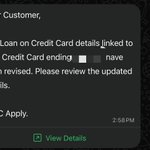
Hey @HDFC_Bank , if I have not taken a loan yet on the credit card, why do you draft the SMS in a way to scare me that I have already taken one. You can do better. Though you are not the only bank to do so in India…


Fouad Farooq retweeted

After making the entire country dance around for KYCs and SIRs their security keys are 4 and 56. Never has such dizzyingly high incompetence married zero accountability on such a large scale. Motherland for a reason ⚡

Fouad Farooq retweeted

Mozilla updated their blog on the eMudhra CA compromise, super efficient way of communicating the whole incident



Impossible standards? Seriously?

Now people should celebrate. An Indian company exits SSL/TLS business. Your witch-hunt and demand for impossible standards has worked.
Readers added context they thought people might want to know
Generating private keys with more than 3 digits for a world-trusted root certificate authority are not impossible standards. Badly generated keys may endanger - and have - the whole internet by breaking the most important encryption protocol.
theregister.com/security/2026/…
cloudflare.com/learning/ssl/w…
Fouad Farooq retweeted

How eMudhra comes up with its private keys -


Fouad Farooq retweeted

There's nothing to "fear monger". Everyone big in the industry has revoked the 8 intermediate certificates already.
Mozilla has permanently removed emSign Root CA G3 from its software. Google will remove it permanently too in the next few days.
Reputation damage is done. The world has mostly "fixed" this mess eMudhra has created and has permanently stopped using one of the very few Indian Certificate Authorities trusted globally.


Fouad Farooq retweeted

October has been an absolute nightmare for software
> Railway - customer secrets exposure
> LiteLLM - malicious PyPI + Docker releases
> Zeabur - infrastructure breached
> OpenCode - AI API keys exposed
> OVHcloud CLI - official binaries backdoored
> Rank Math PRO - malware in official plugin
> TeamUpdraft - customer data compromised
> ConnectWise - cloud backup identities compromised
> Tensorlake - npm package infected
> SubQuery - backdoored npm package
> GhostAction - GitHub repos with malicious workflows
> PHP - critical RCE vulnerabilities
> Node.js - security vulnerabilities patched
> eMudhra - certificate authority keys compromised
> Tailscale - eMudhra incident
At this point, the biggest security risk might not be the code we write, but the code we trust...
Fouad Farooq retweeted

Are you aware of the critical RCE vulnerabilities CVE-2026-109618 and CVE-2026-109619 that are affecting PHP core products?
Our customers are already safeguarded.

Akamai Releases Protections for Critical Remote Code Execution Vulnerabilities in PHP Core
Full Write-Up:
ow.ly/PNPj50ZZIoZ

Fouad Farooq retweeted

🚨 UPDATE: India has launched a special investigation into eMudhra after 8 intermediate CA private keys were found trivially recoverable.
CERT-In and Red Hat have issued fresh security alerts as the fallout extends beyond Chrome, Firefox, and Go.
Read - thehackernews.com/2026/10/ei…

Fouad Farooq retweeted

The important thing with incidents like @eMudhra is to proceed openly and by engaging with the communit… ah crap


Global TLS Intermediate CA incident: We’ve updated our incident page with how it happened, who is affected (one US customer ecosystem), what’s not affected, and what we’re putting in place. We will publish the root cause once our investigation is complete.
👉emudhra.com/en/post/certific…
Readers added context they thought people might want to know
eMudhra minimizes the scope by claiming only "one US customer ecosystem" is affected. In reality, 8 of its CA certificates had catastrophically weak private keys (one being simply the number 4), allowing anyone to forge trusted HTTPS certificates for any website on the internet.blog.google/security/prote…