




Nice numbers. What’s the setup? How many Sparks, which engine and weights (original or a quant), how many streams for the 380, and how long a prompt for the 17.5K prefill, cold or cached? We’re at 289 tok/s at 6 streams and 6.3K cold prefill on 4 Sparks, original weights.
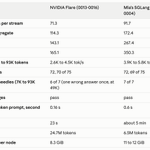
Mean of 8 task types (code, json, prose, math...). 1 stream: code 96 vs 122, prose 52 vs 71, math 83 vs 112 tok/s, Flare vs Mia SGLang. Temp 1, thinking off.

I would not jump to conclusions yet, but hopefully my data is solid and it gives a general baseline.
DeepSeek-V4.1-Flash-1017 (552B MoE, native MXFP4 experts / FP8), TP4 over 4 DGX Sparks. NVIDIA’s Flare vs MiaAI-Lab’s SGLang lane, same weights.
Yes. Same 4 Sparks, 1017 native weights, temp 1, thinking off. KV 24.7M vs 6.5M tokens, start 23 s vs ~5 min. But decode 71 vs 92 tok/s at 1 stream, 114 vs 172 at 4, 165 vs 350 at 16, prefill 2.6-4.5K vs 3.9-5.8K. qeval a draw (72/70 vs 72/69).

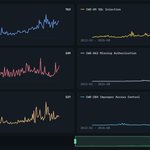
August 2026: 12,275 CVEs published in one month.
That's almost double the 12-month average of 6,256, and the average is climbing too.
If your triage process was sized for 2023 volumes, it's already underwater.
The fastest-growing bug class since 2023 is missing authorization: code that works fine but never checks who is asking.
613 of those CVEs in August alone.
That's also when AI coding tools went mainstream.
Coincidence is doing a lot of work here.
exploit-intel.com/stats


We've been doing this for a while, watching the process is like watching hours of potential frustration pass by as a timelapse. exploit-intel.com/blog/

100% with you on that. Wassenaar popped up first in my head, as that was my churn with 0day back in the day. The argument is not about full disclosure, but some sense of responsibility and self preservation when dealing with what others sometimes call a "weapon".
Agree with the sentiment, but no - you can't 'do whatever you please' with a 0-day just because the exploit is your IP. e.g. - Wassenaar puts strict export controls on intrusion software. Violate it and you can go to jail.
This may help - we actually find that a large portion of existing vulns have an incomplete patch, or more similar vulnerabilities in nearby code...
exploit-intel.com/blog/posts…

Autonomously helping with Vulnerability Research - exploit-intel.com/blog/posts…