
• Vulnerability & Threat Intelligence at https://xitter.cf/t.co/pRPrjARoN2 • Founder of @_WPScan_ (acquired by Automattic) • Founder of DVWA • Ethical Hacking Graduate
Joined June 2009
- Tweets3.8K
- Following837
- Followers21.2K
- Likes15.3K




Ryan Dewhurst retweeted

RAPID RESPONSE: Huntress has become aware of a widespread security incident involving ConnectWise Cloud Backup (formerly SkyKick).
We’ve confirmed that an unknown threat actor abused the access they obtained in SkyKick to pivot to access customers' Microsoft 365 environments. 🧵
Ryan Dewhurst retweeted
We are behind you and that will not change, PM tells Zelensky bbc.in/4yklpHe

Ryan Dewhurst retweeted

Around 80% of vulnerabilities in Previdian's KEV dataset can be exploited without authentication. The remaining 20% require credentials.
CVE-2026-105740 (Langflow) is one of that 20%.
First, they checked whether Langflow's auto-login feature was enabled. When they found it disabled, they switched to trying common, weak credentials.
After successfully authenticating, they immediately attempted to exploit CVE-2026-105740 to access environment variables and perform other actions.
We first observed exploitation attempts on September 19, but activity increased dramatically following the CVE's publication on October 5.
If you're running Langflow, disable auto-login, enforce strong passwords, ensure all patched, and review suspicious authentication and MCP API activity.
We observe exploitation attempts targeting numerous vulnerabilities every day across our honeypot network. There's simply too much activity for us to post about everything.
Don't rely on social media to stay ahead of emerging threats. Sign up to Previdian to stay informed about the vulnerabilities attackers are actively targeting daily.

⚠️1,423 Langflow RCE exploit attempts hit Previdian honeypots from 27 IPs.
The bug lets authenticated users, even non-admins, run OS commands through MCP server configs. Fixed in 1.9.0.
Read: thehackernews.com/2026/10/la…


Confirmed from vulnerable firmware.
It is not today's date, it is derived from today's date.
Doesn't include time.
Still stupid.

Can anyone confirm, before I have to reverse the code myself (with AI), that the Danfoss fridge passwords were derived from today's date, or were today's date.
The only credible information I've seen, direct from the original Claroty source, is that the password is derived from the device's date and time.
Where ya'll getting the info that the password *was* "today's date"?
Either way, it's stupid, but not as stupid as being just today's date.
Using AI to talk to our honeypot data really feels like we're living in the future!
You can now talk to Previdian's exploitation intelligence directly through ChatGPT (and other AI clients)!
Ask about real exploitation attempts, attacker IPs, captured payloads, vulnerability timelines, available virtual patches, and more.
All powered by Previdian's proprietary honeypot intelligence.
Here's a quick demo of Previdian MCP 👇
Ryan Dewhurst retweeted

⚠️ UPDATE: EXPLOITATION ATTEMPTS HIT ATLASSIAN CVE-2026-21589 (CVSS 9.3)
Previdian's honeypot network saw exploitation attempts about 2 hours after watchTowr Labs published its technical write-up on the pre-auth file-read flaw we covered on Oct 6.
What's new:
• Root cause: the shared atlassian-plugins-webresource library turns "::" into "/", so "..::" sequences slip past path-traversal checks
• No login needed: files inside the app server's web root can be read, incl. protected WEB-INF files
• Affects Jira, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible and Fisheye (Data Center)
• In Crowd-linked setups, crowd[.]properties holds the app password in plaintext; watchTowr used it to create a user and make it a Jira admin
• Previdian logged 15 attempts from 3 IPs: 38.60.157[.]86, 146.70.187[.]234, 159.26.119[.]225
Fixed versions are in our earlier post below; one correction: the Crowd 7.1 fix is 7.1.7, not 7.1.1.
⚠️ Analyst Note:
These are attempts seen on honeypots, not confirmed compromises, and the CVE is not in CISA KEV. A Nuclei scanning template is out; expect more probing. Patch now, or pull instances off the internet until you can, and check access logs per Atlassian's advisory.
Source (watchTowr Labs):
labs.watchtowr.com/you-wont-…
#DDW #DarkWeb #Atlassian #CVE #PatchNow
xitter.cf/DailyDarkWeb/status/21…


🚨 ATLASSIAN PATCHES CRITICAL CVE-2026-21589 (CVSS 9.3) ACROSS DATA CENTER PRODUCTS
Atlassian has disclosed CVE-2026-21589, a critical unauthenticated arbitrary file access (path traversal) flaw in its self-managed products, published Oct 5, 2026.
Per Atlassian:
• CVSS 4.0 score 9.3 (Critical), no authentication needed
• A remote attacker can read specific files inside the web application root
• Affects Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible and Fisheye (Data Center/Server)
• Fixed: Jira 9.12.40 / 10.3.26 / 11.3.12; JSM 5.12.40 / 10.3.26 / 11.3.12; Confluence 9.2.26 / 10.2.19; Bitbucket 9.4.26 / 10.2.8 / 10.5.1; Bamboo 10.2.24 / 12.1.12; Crowd 6.3.7 / 7.0.3 / 7.1.1 / 7.2.4; Crucible & Fisheye 4.9.15
• Atlassian Cloud is already patched. WAF / URL-rewrite mitigations are offered if you cannot upgrade yet
⚠️ Analyst Note:
Exploitation requires the exact name and path of the target file; the bug does not allow directory listing. As of Oct 5, it is not in CISA KEV and no public exploit has been reported. Some configurations may still expose sensitive files, so patch internet-facing instances first. End-of-life versions may also be affected.
Source (Atlassian):
jira.atlassian.com/browse/CO…
#DDW #DarkWeb #Atlassian #Jira #Confluence #CVE #CyberSecurity

Ryan Dewhurst retweeted
Exploitation attempts have now started to hit our honeypot network
⚠️ Previdian Watch users were warned earlier this morning that CVE-2026-21589 was highly likely to be exploited, based on an assessment from our autonomous prediction system.
A public PoC has now been released.
The critical, unauthenticated file access (read) vulnerability affects:
• Bitbucket Data Center
• Confluence Data Center
• Jira Service Management Data Center
• Jira Software Data Center
• Bamboo Data Center
• Crowd Data Center
• Crucible
• Fisheye
Atlassian has not reported exploitation and Previdian has not yet observed attempts in our sensors yet.
But with working exploit code now public, we expect that to change very quickly.
Patch affected installations now.
If you cannot patch immediately, restrict internet access or apply WAF mitigation.
The gift that keeps on givin'
A Critical SonicWall SMA1000 vulnerability found by Anthropic has just been patched.
CVE-2026-102255 - Pre-authentication SSRF via unintended forward-proxy
CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H
Affected products: SMA1000 Models - 6210, 7210, 8200v
Apply latest hotfixes.
No evidence of active exploitation yet.
Ryan Dewhurst retweeted
⚠️ Previdian Watch users were warned earlier this morning that CVE-2026-21589 was highly likely to be exploited, based on an assessment from our autonomous prediction system.
A public PoC has now been released.
The critical, unauthenticated file access (read) vulnerability affects:
• Bitbucket Data Center
• Confluence Data Center
• Jira Service Management Data Center
• Jira Software Data Center
• Bamboo Data Center
• Crowd Data Center
• Crucible
• Fisheye
Atlassian has not reported exploitation and Previdian has not yet observed attempts in our sensors yet.
But with working exploit code now public, we expect that to change very quickly.
Patch affected installations now.
If you cannot patch immediately, restrict internet access or apply WAF mitigation.
The advisory was first published on October 1st and confirmed as exploited in the wild by Fortinet at same time.
Started seeing exploitation attempts over yesterday and today (Oct 6th) in our honeypots 🐝
Previdian sensors have recorded 478 probes targeting our FortiMail honeypot decoys that appear consistent with CVE-2026-104286 exploitation activity.
The requests target:
POST /api/v1/ibe/import
They use repeated path traversal sequences inside multipart upload fields, attempting to write attacker-controlled files outside the intended directory.
This is a strong match for the arbitrary-file-write behaviour described for CVE-2026-104286, although we have not confirmed successful exploitation of a real FortiMail appliance.
Observed source IPs:
103.62.49[.]170
85.244.255[.]105
For defenders, review HTTP/WAF telemetry for requests to /api/v1/ibe/import containing traversal sequences in import_file, filename, or uploaded filenames.
Treat the IPs as investigation leads, not proof of compromise.

It was fine and I had a blast.
I was a bit out of practice and a had few bad habits.
I definitely wasn't in the best shape, but managed. Slept for 2 hours afterwards!
Really enjoyed the Diary of a CEO podcast with Adam Neumann, the founder of WeWork.
Spoiler:
1. Choose your life partner, friends, and business partners for the worst day of you life, not for the best.
2. Life is not about when we fall down, it's about how we get up.
3. Choose the life partner who will make you the best version of yourself. The one that you need, not the one you think you want.
4. Control doesn't come from power. It comes from influence. And influence needs to be earned every single day from the beginning.
5. We all have a destiny and a journey. Get to know yourself so you can start living yours.
Ryan Dewhurst retweeted
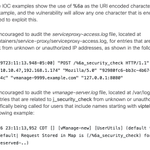
We're seeing this script dropped on our NetScaler sensors during CVE-2026-88771 exploitation attempts.
The 'host' ELF malware is already known to @virustotal
We've seen 51.158.203[.]95 targeting multiple vulnerabilities across our network since 25 Aug.

