

Autonomous Ethical Hacking
Portugal
Joined February 2022
- Tweets796
- Following92
- Followers2.2K
- Likes230




Manual retesting of every AI-generated code change is not a scalable security strategy in 2026.
It creates gaps between the speed of releases, and attackers don’t wait for your next pentest.
Our AI-powered continuous testing helps teams reassess their exposure as systems change at the same speed. Human experts remain essential for interpreting risk and deciding what to do next.
Continuous AI-powered security testing, with human expertise guiding what happens next.

Testing an AI pentesting agent only once means you're only seeing half the picture of how it actually performs. 👀
Because LLMs are probabilistic, outputs change from run to run. In agentic pentesting, small shifts in early exploration multiply, leading to entirely different results by the end of an engagement.
A single run tells you almost nothing. But running dozens of end-to-end tests is expensive, so most teams test only 2 or 3 times. In this low-replication zone, standard p-value testing stops being reliable: with so few runs, a non-significant result often just means your sample size is too small to detect a real difference, not that the upgrade failed.
We built Ethibench to test AI pentesting agents properly, with the replication these systems actually need.
Find out more in the repo👇


Think you are the fastest hacker?
Prove your skills in the CTF at @BsidesLisbon 2026 run by Ethiack
For this edition, we are bringing: Speed Pwning CTF
Two players go head to head. Each match presents both competitors with the same CTF challenge at the same moment. The first to submit a valid flag advances. Losers are eliminated.
- 8 participants
- Single-elimination bracket
- 30-minute matches
- No qualifiers
- Brackets are drawn at random
Find all the details and register below↓

Ethiack is running the CTF for the second year at @BSidesLisbon 2026.
For this edition we have created two experimental competitions split between the two days of the conference (Oct 29-30).
First up a Speed Pwning bracket-based CTF, fast, head-to-head, human-only. Following we will host the first Ethiack SOHO Smashup, a home office hardware exploitation event in the spirit of Pwn2Own's SOHO category, where AI-assisted exploitation is explicitly encouraged.
One competition measures raw individual skill under time pressure; the other measures what hackers can achieve against real consumer hardware with AI-assisted tooling.
Read all the details below ↓

Ethiack is running the CTF for the second year in a row at @BSidesLisbon 2026.
This October 29, we're bringing a new format: Speed Pwning CTF.
Two players go head to head. Each match presents both competitors with the same CTF challenge at the same moment. The first to submit a valid flag advances. Losers are eliminated.
- Single-elimination bracket
- 30-minute matches
- 8 participants
- No qualifiers — entry is by registration, first come first served
- Brackets are drawn at random
Rules? Simple: No AI. At all.
There are three categories in play: pwn, misc and web.
Players decide which category they'll play before each match through a veto process, each player can veto one category. The remaining category will dictate the challenge played by both players during the match
Want to participate?
Register below ↓
Participants must have a BSides Lisbon 2026 ticket to be eligible.


Your team prevents disasters every day, but when you report to the board, their response is always the same:
“Great job keeping us safe. Now show us the numbers: how much did we spend, and how can we spend less?”
They hear terms like “critical” and “CVE,” but what they see is a line item. You’re speaking in risks; they’re thinking in returns.
The fix is Annualized Loss Expectancy (ALE): the realistic damage a vulnerability could cause if exploited. It turns security from a black box into a business decision:
"This risk costs us €4,875/year to ignore."
"Fixing it now saves €24K over five years."
"Here’s how it compares to other risks we’re tracking."
Turn the conversation from avoiding disasters to optimizing spend and protecting revenue. That’s a language every board understands.
How much did we protect? Over €93 million for our customers in 2025 alone and in 2026, that number is accelerating fast.
Contact us to help you calculate this!

Hackian, our agentic AI pentester, operates continuously, self-learns, and is built to think, act, and adapt like a human ethical hacker.
In tests against PortSwigger labs, Hackian solved them autonomously with a >75% success rate. Traditional DAST scanners tested on the same labs scored just 1-5%.
Static tools report what might be vulnerable. Hackian proves what is exploitable.

Third-party vendors and integrations keep showing up in breach reports as one of the easiest ways in, yet most security teams still treat them as a checkbox instead of an ongoing risk.
We see it constantly in retail, telco and fintech environments: a vendor API or partner integration nobody re-tested since onboarding, sitting wide open to exploitation.
Continuous validation catches what a point-in-time assessment misses.

Ethiack is built for one job and that is prioritize what actually matters to your business.
Hackian, our agentic AI, dynamically learns your organization’s business logic and operational scope, then uses that context to drive what to test first and which attack paths are most relevant to your organization. The result is less noise, faster signal, and real-world exploit validation that security teams can act on immediately.
Continuous attack surface discovery + proof-of-exploit findings + risk prioritization based on impact and exposure.
That’s offensive security designed to be continuously correct, before attackers have any chance.
ethiack.com

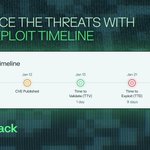
Beat the clock with the Exploit Timeline in the Ethiack portal. Track how quickly Hackian (our pentest agent) detects and validates vulnerabilities, giving your team complete visibility from discovery to fix:
1. Asset Added: the exact moment an asset enters your attack surface.
2. CVE Published: when a vulnerability tied to that asset is publicly disclosed.
3. Time to Validate (TTV): how long it takes Hackian to confirm and prove the exploit works against your asset, measured from CVE publication.
4. Time to Exploit (TTE): how your team's remediation speed compares to known real-world exploitation timelines for that CVE.
5. Resolved: the moment remediation is verified and the exploit path is closed.
Sign up now↓


Discovery without validation is just noise, and vulnerability lists are just queues.
While Attack Surface Management (ASM) tells you what is exposed and Vulnerability Management (VM) lists what is wrong, neither proves what an attacker can actually exploit right now.
That is why Adversarial Exposure Validation (AEV) is needed. AEV sits above both disciplines to cut through the noise, delivering a short, exploit-ranked list backed by reproducible proof.
What validation actually looks like:
Hackian, Ethiack's agentic AI pentester, runs continuously against the discovered surface. It chains vulnerabilities dynamically, pivots when initial approaches fail, and constructs payloads on the fly.
Every finding ships with reproducible proof of exploit through adversarial exposure validation: the payload, the evidence, and mitigation guidance a developer can act on and re-test. Proof pairing: 30x faster than manual pentesting (Ethiack-reported); €12M+ risk prevented at CEGID across 2,000+ assets (Ethiack-reported).

Existing benchmarks for pentesting agents are often too task-specific or limited to CTF-style flag races. That is why we built EthiBench, an evaluation protocol designed around real-world complexity rather than closed-world convenience.
EthiBench shifts the paradigm across four core pillars:
1. Real-World Targets: Tested against multi-functional, open-source apps (covering 108 expert-annotated vulnerabilities across vuln-bank, paygoat, and blog) to force genuine exploration and strategic decision-making.
2. Semantic Matching: Uses an LLM-as-a-judge pipeline paired with bipartite resolution (via the Hungarian algorithm) to accurately score reports without inflation from duplicates or rigid string matching.
3. Dynamic Ground Truth: Treats the answer key as a living resource that expands when agents discover valid vulnerabilities missed by initial annotators.
4. Robust Statistics: Accounts for agent non-determinism by evaluating repeated runs and combining Welch's t-test with Cohen's d to prevent high variance from masking real performance gains.
Read the full breakdown ↓


1 month to go. Ethiack is running the CTF at @BSidesLisbon 2026 on October 29th.
Two days, two very different formats:
Day 1: a head-to-head speed challenge. No AI, just raw human speed.
Day 2: live hardware hacking on stage. AI and agentic tooling welcome.
Registration and qualifier details coming soon. More on each challenge as the date gets closer.
Find more information about the event below ↓
