

Beyond testing tools, solutions that deliver expertise. 🌐 Chip & binary security testing https://xitter.cf/t.co/1dUvkjLR8L https://xitter.cf/t.co/BCMLXCF49H
Joined July 2015
- Tweets1.1K
- Following336
- Followers1.8K
- Likes379




Part 2 of our Android kernel exploit chain (CVE-2023-20938): the stale read returns garbage until you control what reclaims the freed slot.
Land the right object there and it hands back a live kernel pointer instead. That’s your KASLR bypass.
eshard.com/blog/kernel-uaf-2…
In case you missed it: we started publishing a full Android kernel exploit chain built on CVE-2023-20938.
Part 2 is coming soon.
eshard.com/blog/kernel-uaf-1…

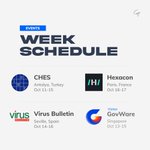
Live from Paris at @hexacon_fr 🔵 We’re here with the team until tomorrow, come say hi!
If you want something to dig into, our Android kernel UaF series is live, and you can explore the trace at ttd.eshard.com


We’re publishing a full Android kernel exploit chain built on CVE-2023-20938, a use-after-free in Binder, on a Pixel 6 running Android 12.
🔗 eshard.com/blog/kernel-uaf-1…
𝚘𝚏𝚏𝚜𝚎𝚝𝚜_𝚜𝚒𝚣𝚎 = 15.
That’s all it takes for Android’s Binder driver to free an object it’s still using.
Part 1 of our CVE-2023-20938 exploit chain: the trigger. Every stage recorded with time-travel debugging, hosted trace included.
🔗 eshard.com/blog/kernel-uaf-1…
Recording a malware sample used to be a long list of manual steps.
Now one sentence to an LLM connected to Epoch covers it all, from a clean isolated VM to a verified, indexed trace.
eshard.com/blog/record-malwa…


What can an adversary actually extract from a captured autonomous system?
Keys, firmware, protocols, algorithms, AI models and more can all become part of the attack surface.
eshard.com/blog/what-can-an-…

Live from CHES in Turkey. 🔵 Come by our booth to discuss PQC implementation security, and meet us at the poster section for the latest research on HQC.


Last chance to join our October PQC training. 🚨
2 days, online, hands-on: recover keys via power analysis and fault injection, forge Dilithium signatures with one bit-flip.
Register: eventbrite.fr/e/pqc-physical…
🔥 50% off for students: "STUDENT"

We tested Botan 3.7.1’s ECC from source code to EM attacks on an iMX 8.
Constant-time on paper wasn’t constant-time on silicon: a timing leak and a table lookup leak both worked on real hardware.
Accepted at HS3 @ ESORICS 2026.
eshard.com/blog/botan-physic…


Lite VM Studio builds a quiet Windows VM from one prompt: emulation CPU drops from 86% to 1.3% of a host core on Windows 10, about 66x less noise.
🔗 See how we did it: eshard.com/blog/lite-vm-stud…
Lite VM Studio builds a quiet Windows VM from one prompt: emulation CPU drops from 86% to 1.3% of a host core on Windows 10, about 66x less noise.
🔗 See how we did it: eshard.com/blog/lite-vm-stud…
We’re at UAV SHOW Bordeaux this week! 🚁
Stop by our booth to talk about physical capture and protecting what matters inside autonomous systems.
We’ve also just published our new white paper "A practical security guide for autonomous systems".
📄 Download: eshard.com/industry-space-an…

We're here at @nextappdevcon in Berlin 💙 Find us at our booth, and at lightning talk this Friday at 11h20 local time.


In the next chapter of our series on implementation security for autonomous systems, we raise awareness of one point: Physical capture. A risk that traditional security programs don't fully address.
eshard.com/blog/designing-au…

Record first. Ask questions afterwards.
We used Epoch to record an Android app's full-system execution, then asked an AI agent to test it against OWASP MASVS. The trace stays as evidence.
eshard.com/blog/ai-mobile-ap…

📍 NextApp DevCon, Berlin: introducing our new time travel debugger for AI investigations.
💬 Talk: "Reconstructing Telegram: Time Travel Debugging Meets AI on Android"
📍 UAV Show, Bordeaux: diving into the world of drones, with a first blog post: eshard.com/blog/autonomous-s…
