

Dev • Aspiring Minimalist • Blogger | @abu_naturals
Addis Ababa, Ethiopia
Joined November 2021
- Tweets1.3K
- Following379
- Followers858
- Likes2.8K





elshaday retweeted

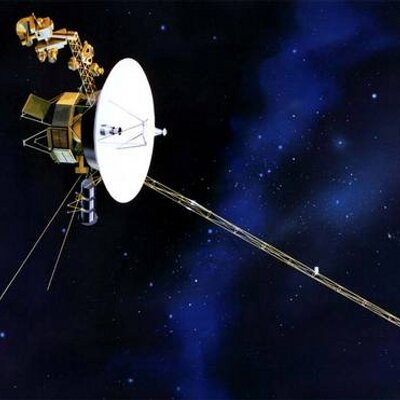
Just 34 minutes before its cameras were turned off in 1990, Voyager 1 captured this iconic view of Earth – a pale blue dot in the vastness of space.
Today, Voyager 1 is one light-day away from Earth. A little piece of our planet journeying through interstellar space. 🌎💙

ALT Earth is seen in the vastness of space as a single, bright blue dot in the middle of a fuzzy, white sun ray. Other rays of light are scattered across the image. Credit: NASA


elshaday retweeted

Tomorrow, Voyager 1 will reach one light day from Earth , on Wednesday November 18th, 2026 at 1:16pm EAT..
elshaday retweeted
The SpaceX engineers who caught the rocket don't write LinkedIn thought pieces about leadership.
elshaday retweeted

Congratulations @SpaceX!
For the first time in human history, a spaceship has been caught by a launch tower.
What an extraordinary engineering achievement. 🎥 by @KEnagonio

elshaday retweeted

Fable 5.2 wrote its own specifications, selected the components, routed the four-layer circuit boards, designed enclosures for 3D printing, and programmed the software.
Each board was ready for manufacture in under a day. All three devices work without any modifications.

How is a simple validation not done

🆕 New CVE
Contact Form 7: remote code execution via unauthenticated form file upload (CVE-2026-114432)
Unauthenticated visitors can upload arbitrary files that may run as code on common Apache setups.
Patch → 6.2.4
cve.now/CVE-2026-114432?utm_…

1
268
Learning project: a codebase Q&A agent that runs fully locally
currently: Celery's 43.5k lines split into ~3,150 AST-aware chunks, local embeddings, vector search, then an LLM answers citing file and line
next: fine tuning
github.com/Elshaday97/Loom


elshaday retweeted

‼️WARNING - OpenSSH issues emergency fix for a critical SSH authentication bypass on Alpine Linux.
A password longer than 256 bytes can unlock key-only accounts on affected servers, without knowing the actual credentials.
Here's how it works ↓ thehackernews.com/2026/11/op…


elshaday retweeted

The bug is like a joke.
On Alpine Linux, type 257 to 1024 characters of anything and you get root. 💀

‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password.
The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours.
It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY".
Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.


elshaday retweeted

Kubernetes is beautiful.
Every Concept Has a Story, you just don't know it yet.
In k8s, you run your app as a pod. It runs your container. Then it crashes, and nobody restarts it. It is just gone.
So you use a Deployment. One pod dies and another comes back. You want 3 running, it keeps 3 running.
Every pod gets a new IP when it restarts. Another service needs to talk to your app but the IPs keep changing. You cannot hardcode them at scale.
So you use a Service. One stable IP that always finds your pods using labels, not IPs. Pods die and come back. The Service does not care.
But now you have 10 services and 10 load balancers. Your cloud bill does not care that 6 of them handle almost no traffic.
So you use Ingress. One load balancer, all services behind it, smart routing. But Ingress is just rules and nobody executes them.
So you add an Ingress Controller. Nginx, Traefik, AWS Load Balancer Controller. Now the rules actually work.
Your app needs config so you hardcode it inside the container. Wrong database in staging. Wrong API key in production. You rebuild the image every time config changes.
So you use a ConfigMap. Config lives outside the container and gets injected at runtime. Same image runs in dev, staging and production with different configs.
But your database password is now sitting in a ConfigMap unencrypted. Anyone with basic kubectl access can read it. That is not a mistake. That is a security incident.
So you use a Secret. Sensitive data stored separately with its own access controls. Your image never sees it.
Some days 100 users, some days 10,000. You manually scale to 8 pods during the spike and watch them sit idle all night. You cannot babysit your cluster forever.
So you use HPA. CPU crosses 70 percent and pods are added automatically. Traffic drops and they scale back down. You are not woken up at 2am anymore.
But now your nodes are full and new pods sit in Pending state. HPA did its job. Your cluster had nowhere to put the pods.
So you use Karpenter. Pods stuck in Pending and a new node appears automatically. Load drops and the node is removed. You only pay for what you actually use.
One pod starts consuming 4GB of memory and nobody told Kubernetes it was not supposed to. It starves every other pod on that node and a cascade begins. One rogue pod with no limits takes down everything around it.
So you use Resource Requests and Limits. Requests tell Kubernetes the minimum your pod needs to be scheduled. Limits make sure no pod can steal from everything around it. Your cluster runs predictably.


elshaday retweeted

today, we introduce a little mischief to the world.
for four years, we’ve been brewing real brain cells on electrodes to understand how they compute. now, we’ve turned those discoveries into a video model anyone can use.
from 0.5¢ a second, mischief 1 is at least 5x faster than its base and the cheapest image-to-video model on @fal and @OpenRouter. soon to be on @awscloud marketplace.
it’s not a delusion anymore. biocompute is real, commercial and this is just the beginning.
happy halloween.