





Pinned Tweet
I just achieved one of my 2025 goals by gaining my first private invite on Bugcrowd ✌️✌️✌️
I Built a Hackbot for Less Than $250 youtu.be/z5wQNqQ-e6M?si=s41c… via @YouTube
Eib retweeted

A different approach to Bug Bounty Hunting:
Instead of using your time and tokens searching for attack vectors and then looking for their impact, start with the impacts that the BB accepts.
1. Start from the impact
Identify the valid impacts accepted by the BB and focus your thinking there.
2. Guide your AI from the impact
Point your AI system toward a specific goal instead of asking it to find arbitrary attack vectors. For example: find a vulnerability that leads to unauthorized fund loss.
3. Filter for valid findings
Use the goal to guide the AI and focus its reasoning only on findings that can actually produce an accepted impact.
4. Go deep
Once you have a potential finding, go deep. Start from the end and work backward toward the root cause.
It’s like reverse engineering the vulnerability. Instead of:
Attack vector → Impact
Try:
Impact → Attack path → Root cause
Start from the end, not from the beginning.
Eib retweeted

Web apps protect their cookies from XSS with `HttpOnly`.
But ESI markup runs server-side, so an attacker can read those cookies anyway.
The lesson? Obscure tech = completely new attack surface. Read those docs.
Full talk: youtu.be/Df42-CfJF8k

Eib retweeted

⚠️ CVE-2026-94545 (CVSS 9.5) ⚠️
Your Next.js OG image endpoint can hand an attacker a shell. 😱
If you use next/og on the Node runtime with sharp installed (what Next recommends for prod), one unauthenticated POST to that route runs commands on your server. Here's why: Satori builds the image as an SVG and drops your text in without escaping it, so an attacker breaks out of the tag and injects their own markup. It reaches the native image libs (sharp, libvips, librsvg, libxml2) and corrupts memory there, and since Node ships non-PIE, a hardcoded ROP chain lands execve every time.
This is the default prod setup, not some weird edge case. 🚨
Not affected: edge runtime or no sharp — that path uses the wasm renderer.
Patched in Next.js 16.3.6 / Satori 0.33.5. On 16.2.0–16.3.5? Update now.
🔥 PoC + setup: github.com/EQSTLab/CVE-2026-…
#Nextjs #RCE #CVE #PoC #Exploit #CyberSecurity #nextog #CVE_2026_94545
Eib retweeted

🚀 New Update: ?mode=txt on subdomains.jsmon.sh
One API call - Fetch all subdomains. Even if a domain has 500K subdomains, full output in seconds.
curl -s -H 'Api-Key: YOUR_KEY' 'subdomains.jsmon.sh/api/doma…'
Available on Pro and Max plans.

Eib retweeted

The height of strategic wisdom is to avoid all conflicts and entanglements from which there are no realistic exits.
Eib retweeted
It is your own bad strategies, not the unfair opponent, that are to blame for your failures.
You are responsible for the good and bad in your life.
Eib retweeted
Do not fight them. Instead think of them the way you think of children, or pets, not important enough to affect your mental balance.
Eib retweeted
In the realm of power, everything must be judged by its cost, and everything has a price.
Eib retweeted
Accept your limitations and work with what you have, rather than fantasize about godlike powers you can never attain. Maintain a realistic attitude.
Eib retweeted
Since your success depends on the people you work with and for, make their character the primary object of your attention.
You will spare yourself the misery of discovering their character when it is too late.
Eib retweeted

Don't just read posts about hacking AI. Be part of it!
Yes, we actually have practice labs (Hubs) for hacking an actual AI. 🤖
Start hacking today, they’re free! 👇
hhub.io/eSLRYyLUEV
Eib retweeted

When fuzzing is no longer treated as merely bruteforcing, you start to unlock meaningful results 🤠
From discovering hidden assets to turning unusual behavior into exploitable vulnerabilities! 😎
In our latest article, we've teamed up with Orwa Atyat (@GodFatherOrwa) to dive deeper into mastering web fuzzing for reconnaissance and vulnerability exploitation.
Read the article now! 👇
intigriti.com/researchers/bl…

Eib retweeted
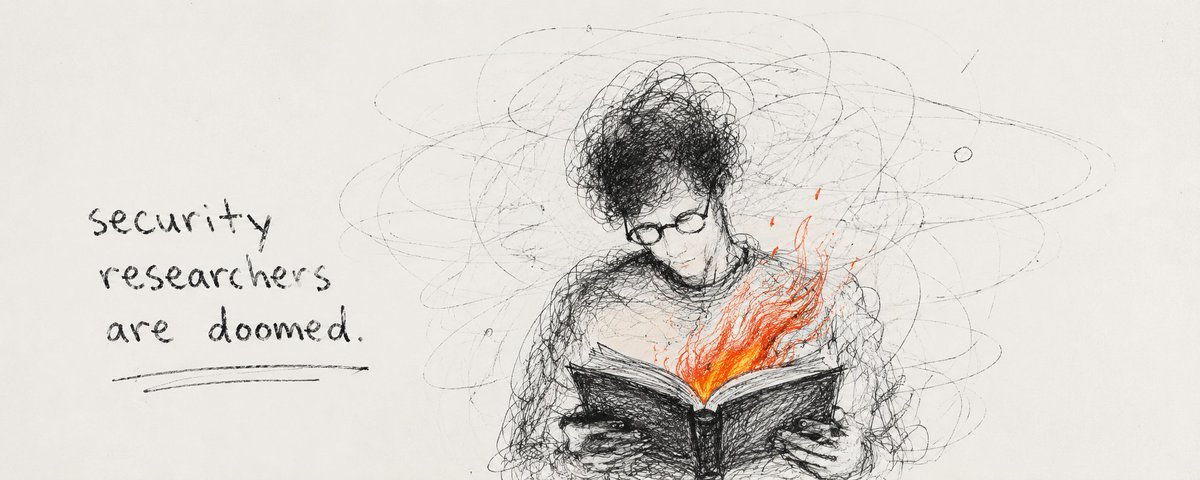
“Security researchers are doomed because of AI.”
I kept hearing versions of this, so I went back through 500 years of people saying the same thing every time a machine learned a human skill.
Some were idiots.
Some were right.
Here’s where I landed.
Eib retweeted
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
You will find a Critical vulnerability.
Eib retweeted

i got $50K+ in bounties hacking ai
100% accuracy, 0 duplicates
will be spilling all my secrets this friday at Bug Bounty Village, DEF CON , so everyone can do it 😎
can’t make it? lmk if i need to send you the recording once it’s out 🔴


Eib retweeted

The whitepaper is live! Read "Can AI Do Novel Security Research? Meet the HTTP Terminator" here ->
portswigger.net/research/htt…
