

America's Most Secure Cellphone Service (https://xitter.cf/t.co/KgeWAAAUe9)
San Francisco, California
Joined January 2012
- Tweets3.8K
- Following6
- Followers9.3K
- Likes2.7K
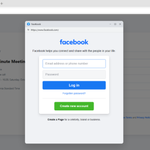


‼️ Hackers are using FAKE Meta job interviews to steal Facebook and Google accounts, even when 2FA is enabled.
Malwarebytes uncovered a phishing campaign using fake Calendly pages to book 30-minute recruiter calls.
Victims choose a slot, enter personal details and complete a fake CAPTCHA.
Then comes the trap: fake Facebook and Google logins that steal passwords and 2FA codes in real time.
Your phone's security codes can become the attacker's way in.
🧵


Your phone is part of this attack.
Scammers can request SMS/WhatsApp OTPs, authenticator codes and Google sign-in approvals.
If your Google account falls, attackers may also access email, recovery options and password resets for other services.
High-value accounts face serious exposure.
Protect yourself:
- Verify recruiters independently
- Use passkeys or hardware security keys
- Never share OTPs or approve unexpected prompts
- Secure your mobile number against SIM swaps and unauthorized port-outs
- Review recovery settings and active sessions
Your phone number deserves protection too. This is what we do @efani!
⚠️ Your crypto security plan needs an answer to: “Unlock your phone. Now.”
An attacker who threatens you directly may never need to crack a password. That is the danger behind a “wrench attack” - using physical coercion to force someone to surrender access to their assets.
Your phone can reveal wallet apps, exchange accounts, private conversations and clues about what you own. For high-value targets, that exposure deserves serious attention.
In this clip, Efani’s Mark Kreitzman and Deniable founder Josh Thomas discuss the “decoy wallet” analogy: revealing a limited environment while keeping more sensitive information separate.
Josh explains how that thinking informs Deniable’s approach to phone privacy. It cannot guarantee safety during an attack, but it raises a question every crypto holder should consider:
How much would someone discover if they forced you to open your phone?
At @efani, we see phone-number protection, account security and device privacy as connected parts of protecting your digital life.
Watch the clip. Full interview and Deniable details in the next post. 👇
Watch Josh Thomas and Mark Kreitzman discuss crypto security, coerced unlocking and Deniable’s approach to phone privacy.
Full interview:
youtu.be/WQ8vnYbrXrU
Learn about Deniable:
deniable.io/
🚨 A 5-day-old domain was already copying Microsoft Teams’ login screen and interface.
Researcher Steven Lim flagged teams-cloud[.]live on October 18, warning organizations to block it.
For employees joining meetings on their phones, a familiar Teams screen can make an unexpected login request look legitimate. Entering work credentials there could put confidential conversations, company files and client information at risk if attackers gain access.
Bookmark this thread for the warning signs and protective steps.

A company name in the address proves nothing.
The reported amgen[.]teams-cloud[.]live subdomain still sits under teams-cloud[.]live.
That does NOT establish an Amgen breach. The report also provides no confirmed victim count or evidence of captured passwords.
On mobile, open Teams directly and verify unexpected login or update requests with IT.
Enterprises: block the reported domain, investigate visits and enforce phishing-resistant MFA using passkeys or FIDO2 security keys.
A copied login page should never be enough.
#Cybersecurity #Microsoft #Efani
Your next attacker may already know enough about you to sound convincing.
Your name. Your number. Your address. Details that make “Hi, I’m the account owner” a much more believable story.
On DailyCyber with @BrandonKrieger, our GM Mark Kreitzman discusses how breaches, data brokers, public directories, and AI crawlers are changing personal privacy - and what that means for SIM swap threats.
The danger is what happens when scattered details become a convincing impersonation attempt.
For crypto holders, executives, and founders, protecting your phone number means looking closely at how your carrier verifies identity. Knowing facts about you should never be enough to take control of your service.
Watch the clip. Full interview in the next post. 👇
Watch Efani GM Mark Kreitzman’s full conversation with @BrandonKrieger on DailyCyber about SIM swapping, personal data exposure, and mobile security.
Your personal information may circulate beyond your control. Protecting your mobile identity still matters.
youtube.com/watch?v=oMJIultg…
🚨 90 seconds. One convincing phone call. Someone else controlling your mobile account.
On DailyCyber with @BrandonKrieger, our GM Mark Kreitzman recounts a white-hat demonstration where a hacker used a believable story - and a crying baby playing in the background - to get a reporter’s mobile account details changed.
The deeper warning: a SIM swap can begin before anyone asks to transfer your number.
An email change. A password reset. Smaller changes that make the next request look legitimate.
For crypto holders, founders, and executives, those account changes deserve attention. Your mobile account is part of your security perimeter.
Watch Mark explain the sequence. Full interview in the next post. 👇
Watch the full DailyCyber conversation between @BrandonKrieger and Efani GM Mark Kreitzman on SIM swapping, social engineering, and protecting your mobile identity.
youtube.com/watch?v=oMJIultg…
⚠️ Someone forces you to unlock your phone. How much of your life does that one PIN expose?
Your messages, financial apps, private photos and business conversations could all become accessible without anyone needing to hack the device.
In this clip, Josh Thomas, Founder and CEO of Deniable, joins Efani’s Mark Kreitzman to explain the problem of coerced unlocking - and how separate encrypted environments are designed to give users more control over what an unlocked phone reveals.
For crypto holders, executives and anyone carrying sensitive information, this raises a critical question: have you planned for someone targeting you directly?
At @efani, we believe mobile security must account for both remote account takeover and physical access to your device. Protecting your number and protecting the information on your phone address different parts of that risk.
Watch the clip, then find the full interview and Deniable website in the next post. 👇
What separates Deniable’s approach from @GrapheneOS’s duress PIN? Josh explains the distinction and the thinking behind plausible deniability.
Watch the full conversation: youtu.be/WQ8vnYbrXrU
Explore Deniable: deniable.io/
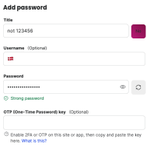
🚨 It's 2026. We have password generators, password managers, Face ID, and passkeys.
Yet someone reportedly used "123456" to help expose 8.8 MILLION records in Denmark. 🤡
According to reports, THREE accounts at an IT contractor used this password. One was an ADMIN account.
8.8 million records. Protected by the password equivalent of leaving your front door wide open.
You can't make this stuff up. 👇

Your smartphone makes this even scarier.
It holds your email, banking apps, crypto wallets, and often the phone number used to recover your accounts.
If someone compromises your email or hijacks your phone number, they may be able to reset passwords and target other accounts.
For executives and high-net-worth individuals, the financial stakes can be enormous.
And yes, a strong password alone won't stop a SIM swap.
It's 2026... PLEASE retire "123456." 🙏
🔐 Use a password manager to generate unique passwords.
🔐 Enable passkeys and phishing-resistant MFA where available.
🔐 Secure your primary email and recovery accounts.
🔐 Protect your mobile number against unauthorized SIM swaps and port-outs.
🔐 Remove unused accounts and recovery methods.
Your phone holds too much of your financial life to protect it with six consecutive numbers.