

@feedly CEO. Passionate about research, machine learning, design, and cybersecurity
Atherton, CA
Joined October 2007
- Tweets13.3K
- Following1.1K
- Followers3.7K
- Likes7.6K





Edwin K retweeted

We're excited to share that after achieving #SOC2Type1, Feedly has completed its SOC 2 Type 2 examination, verified by @Aligncompliance.
For #CTI teams operating under compliance mandates, this gives your InfoSec team a documented answer on how #Feedly protects your data.
feedly.com/new-features/post…
@AICPA

Edwin K retweeted
Triaging an #IoC list means deciding which indicators are malicious enough to act on, and that usually means looking each one up in #VirusTotal separately and reconciling it by hand.
Feedly now pulls @virustotal #detectiondata directly into IoC Insights Cards: confirm if malicious in seconds, judge zero-detection domains from WHOIS, certs, and hosting, and trace your investigation into VirusTotal in one click.
Learn more: feedly.com/new-features/post…
Edwin K retweeted
12 new #AIprompts for #CTI work, free to use in any #LLM and grounded in what actually works for #threatintel.
Earlier this year our CTI Prompt Library covered the fundamentals. Volume 2 builds on it with prompt chaining, so a report can move through to a finished output in one pass.
feedly.com/ti-essentials/pos…

ALT CTI Prompt library Vol. 2 announcement. 12 prompts. 4 ready made chains. Built with the CTI community.

ALT Prompt example: Detection opportunity generator prompt that turns your data into a structures Sentinel detection engineering report.

ALT Chained prompt example: AI threat activity to detection opportunities.

ALT Meet our contributors Built with the CTI community Real prompts they rely on in their own work.
Edwin K retweeted

We recently wrote a guide for operationalizing ASN data for threat detection with @feedly TI Essentials.
Check out how, when, and why to track ASNs alongside IOCs here: feedly.com/ti-essentials/pos…
What's inside
- How to score ASNs with free tools
- Alerting vs. blocking
- Clustering to connect infrastructure
- Dive into Tycoon2FA

Edwin K retweeted
CTI teams need to process dozens of threat intel reports every week.
That’s why our #CTI Advisor Josh Darby MacLellan mapped out how to automate 5 workflows that cover #IOC enrichment all the way to stakeholder briefing.
Estimated time saved per report: 145–290 min
Full guide with actual prompts 👇
feedly.com/ti-essentials/pos…

AI won't make human capital less valuable it makes it more valuable. You can offload a task. You can never offload your learning.
The firms that win won't be the ones picking the best model, but the ones building a loop where people and AI compound on top of it.
Build a frontier ecosystem, not just a frontier model.
That's the whole game.

Edwin K retweeted
#MITRE ATT&CK is one of the most widely used frameworks in #cybersecurity, and its real power goes beyond technique mapping.
In our next #CTI Session, Amy and Lex from The @MITREattack Corporation walk through how to turn #TTPmapping into behavior-first detections that run in production.
feedly.com/cti-sessions/turn…

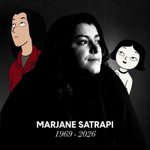
Today I learned that Marjane Satrapi, the creator of Persepolis, has passed away at 56.
linkedin.com/posts/edwink_to…




Edwin K retweeted
#CTI practitioners are great at tracking adversaries but the best ones are also great at telling the story of why it matters.
Join us June 17 at 9AM PT!
We’ll break down the metrics that matter most at each stage of program maturity, and how to build a #businesscase that earns confidence from your #CISO and leadership team.
feedly.com/cti-sessions/prov…

Edwin K retweeted
Feedly #Threat Intelligence + #OpenCTI = a #CTI knowledge graph that's always ready!
We're excited to share our new integration with OpenCTI by @FiligranHQ and a sneak peek of how Feedly Threat Intelligence automatically delivers structured, contextual #OSINT directly into your OpenCTI knowledge graph so your analysts can jump straight to pivoting and investigating.
feedly.com/new-features/post…

Edwin K retweeted
Most #CTI teams want to be more proactive. Here's what that looks like in practice.
When #ScatteredSpider hit UK retail, Ian Parsons and his small team at @Quilter already had the full Dragon Force profile and an executive-ready report done the same afternoon.
Here's the challenge they faced and the workflow that changed everything 👇
feedly.com/customers/posts/f…
#ThreatIntelligence #CyberThreatIntelligence

Edwin K retweeted
If big companies can't make a net return on their LLM token costs, that doesn't mean it's impossible to. In fact this is exactly what you'd expect to happen with a new technology. Incumbents can't use it well, and are replaced by upstarts who can.
Edwin K retweeted
BFSI CTI teams juggle triage, incident response support, fraud coordination, and exec briefing, often at the same time.
That’s why we put together 10 prompt templates to help with #BFSI #CTI workflows: feedly.com/ti-essentials/pos…
#cybersecurity #threatintelligence

Edwin K retweeted
A #vulnerability rated MEDIUM sat unpatched for 3 months. Then #CISA added it to #KEV as actively exploited, CVSS 9.8.
That 3-month gap can be deadly. #CTI can help close it.
Mari Galloway, CEO A&M Strategies + CEO & Co-Founder of @WomenCyberjutsu walks through the exact playbook BrickHaus's #CTI team used to prioritize their vulnerability backlog.
feedly.com/ti-essentials/pos…

Edwin K retweeted
One Pharma security team is currently:
→ Pulling hundreds of #IOCs from 7,500+ sources without the manual work
→ Starting their day with a #TTP briefing waiting in MS Teams every morning at 7:30am
→ Monitoring #ScatteredSpider live and turning new TTPs into #detectionrules
Read the case study for the full breakdown 👇
feedly.com/customers/posts/p…


Edwin K retweeted
In case you missed it…
We have a #TI Essentials article covering what good #cybercrime investigation actually looks like.
We sat down with Will Thomas (@teamcymru) and Garrett Carstens (@Intel471Inc) and did a deep dive from verifying #threatactor claims before you react, to #crypto tracing, to why you shouldn't try to engage criminals on the fly.
feedly.com/ti-essentials/pos…

Edwin K retweeted

GBrain is your company brain

how I’m building an agent company inside my agency.
the structure looks like this:
Agency gBrain
→ Orchestrator Hermes Agent
→ Department verticals
→ Specialist agents
→ Scoped sub-agents
gBrain is the company brain.
It gets ingested with the data and experience we already have:
> transcripts
> chats
> previous campaigns
> client learnings
> strategy docs
> internal workflows
> examples of what good looks like
That brain is maintained by a human champion plus an orchestrator Hermes Agent.
Under the orchestrator, we have different department verticals inside the agency.
Each vertical has its own specialist agents.
Some of those specialist agents have even narrower scoped agents underneath them.
I’ve found that narrow scope improves output quality and reduces drift.
> a general “marketing agent” is too vague.
> a lifecycle email agent with access to the right campaigns, voice rules, approval gates, and examples can get very good.
> a technical SEO agent with its own tools, checklists, and source standards can get very good.
> a content research agent with narrow inputs and a clear definition of done can get very good.
The narrower the job, the easier it is to improve the agent.
I use different harnesses for this.
Mostly Hermes Agent, but also CLI harnesses like Codex and Claude Code depending on the job.
I’m still looking for a good bare-bones harness for model routers to run on.
To keep track, I maintain an org chart inside the company gBrain.
The org chart shows:
> top-level orchestrator
> department verticals
> specialist agents
> scoped sub-agents
> which brain each agent reads from
> which tools each agent is allowed to use
> where human approval is required
For clients, I do downstream pods.
Think of them as new agent companies that are isolated from the agency brain, but can still communicate with our agency agents when needed.
A client pod has its own:
> client gBrain
> client orchestrator
> client specialist agents
> client-specific workflows
> client-specific approvals
> client-specific memory
This is important.
You do not want client context bleeding across accounts.
You do not want one agent with every client’s data, every tool, and every permission.
Scope is what keeps the system useful.
The powerful part is that once you build one vertical agent well, you can fork it.
Not copy-paste blindly.
You still need to customize the context, examples, approvals, voice, tools, and workflows.
But you are not starting from zero.
You might have 75% of the agent already done.
That changes the agency model.
You no longer need a full traditional department for every function before you can deliver a well-rounded marketing service.
One or two strong marketing engineers can run an output surface that used to require a much larger team.
But this only works if the agents are actually good.
It takes iteration, taste, source material, QA, workflow design, and real marketing experience.
Bad agents do not become good because you connected more tools.
Vague agents just create vague output faster.
TLDR:
> turn the agency’s knowledge into a brain
> turn repeated work into scoped agents
> turn each client into an isolated pod
> let skilled operators run the system
