

Deep tech infrastructure builder | Developing MerdekaL1 — Malaysia’s post-quantum Layer-1 for institutional digital finance. 🇲🇾
Kuala Lumpur City
Joined September 2025
- Tweets238
- Following48
- Followers52
- Likes561



Pinned Tweet
Our website now support TLS 1.3 with hybrid X25519 + MLKEM768 key exchange.
For supported browser sessions, that means combining X25519 (widely used on the web today), with ML-KEM-768 (a post-quantum method designed for future threats). It helps protect session data from harvest-now, decrypt-later risk.
Certificate authentication remain ECDSA while post-quantum certificate standards mature. Hybrid key exchange can keep eligible sessions confidential, but it’s not the finish line for post‑quantum migration.
The broader requirement is crypto-agility: being able to swap cryptography without rebuilding the entire system.

We won as Token-X Champion! 🏆
Proud to build MerdekaL1 for institutional tokenisation, with post-quantum security for verifying and exchanging data across the network.
Thank you, @sidecmy, for giving Malaysian builders a platform to grow.
mediaselangor.com/en/2026/10…


𝗧𝗼𝗸𝗲𝗻𝗶𝘀𝗲𝗱 𝘀𝘂𝗸𝘂𝗸 𝘄𝗶𝗹𝗹 𝗯𝗿𝗶𝗻𝗴 𝗯𝗹𝗼𝗰𝗸𝗰𝗵𝗮𝗶𝗻 𝗰𝗹𝗼𝘀𝗲𝗿 𝘁𝗼 𝘁𝗵𝗲 𝗿𝗮𝗸𝘆𝗮𝘁 𝘁𝗵𝗿𝗼𝘂𝗴𝗵 𝗮 𝗽𝗿𝗮𝗰𝘁𝗶𝗰𝗮𝗹 𝗳𝗶𝗻𝗮𝗻𝗰𝗶𝗮𝗹 𝘂𝘀𝗲 𝗰𝗮𝘀𝗲.
Under Budget 2027, the proposed tokenised retail savings sukuk initiative would let Malaysians invest in government sukuk and choose which national priorities their funds support — education, healthcare, or social protection.
As a home-grown digital asset infrastructure builder, we welcome this direction. It connects investment participation with outcomes people recognise in their daily lives, while helping more Malaysians understand blockchain’s wider potential in finance.
A low entry barrier should be a central design goal for financial inclusion. Participation needs to be accessible, understandable, and straightforward for the rakyat — supported by infrastructure that institutions can trust.
💡 Our view: this is the right first step to building blockchain financial literacy among Malaysians.

Tokenised sukuk’s potential can be realised on MerdekaL1, our purpose-built blockchain infrastructure that we're developing to support initiatives like this.
For MerdekaL1's development, read here: xitter.cf/e23_io/status/21073640…

Within the next few years, AI may drive breakthroughs that weaken or break some of the cryptography securing today’s financial systems. That possibility makes post-quantum cryptography (PQC) harder to dismiss.
Payment networks and financial infrastructure should begin migrating away from current primitives and become crypto-agile, so they can switch algorithms quickly if a widely used scheme is compromised. The rails that move value between institutions need durable proofs of authenticity and integrity that remain verifiable over time, even if conventional signatures become unreliable.
The goal is straightforward: ensure funds and instructions remain safe, traceable, and tamper-evident from one endpoint to another—without relying on any single cryptographic assumption to hold forever.
A little context for anyone following this without a cryptography background:
Your Bitcoin private key authorises spending. Your public key lets the network verify that authorisation without revealing the private key.
The security rests on how difficult it is to work backwards from the public key to the private key.
Drake’s concern is that AI could help discover a mathematical shortcut. He is raising a scenario, not demonstrating that Bitcoin’s cryptography has been broken.
Some Bitcoin address types hide the public key behind a hash until funds are spent. That explains his focus on exposed public keys. Fresh addresses offer limited protection in this scenario; they are not a complete solution.
e23's takeaway: institutions need to understand both how their assets are protected today and how they would change that protection safely. That ability to adapt is what crypto-agility means.

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
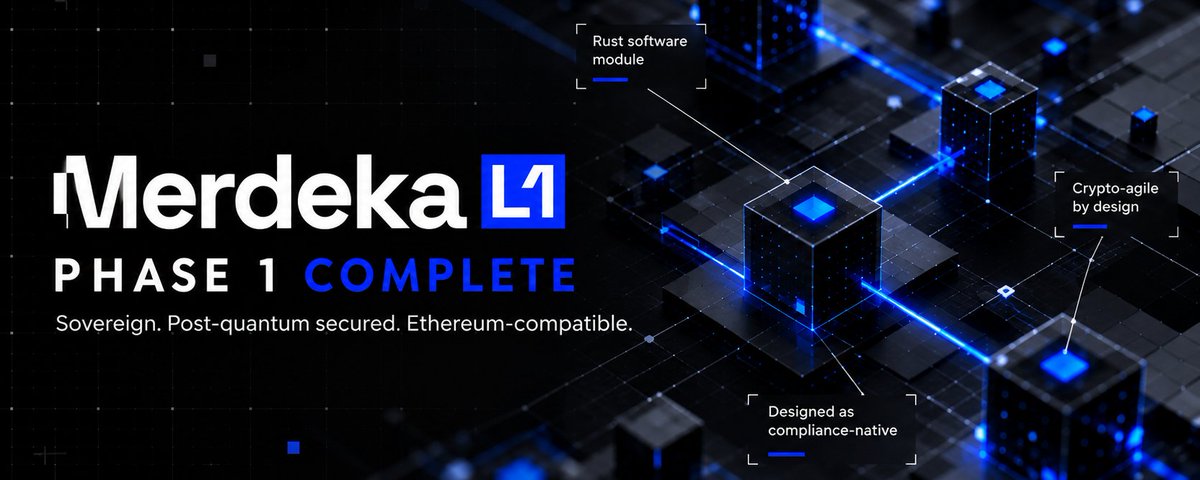
Phase 1 of MerdekaL1 is complete 🇲🇾
11/11 planned modules, built and tested.
The core network is up. Post-quantum security is built into the foundation with Ethereum compatibility.
See how MerdekaL1 is taking shape ⬇️
For #CybersecurityAwarenessMonth, don’t stop at “don’t click the wrong link.” Unique passwords, 2FA, and patching still matter.
The data that will hurt you was encrypted years ago, under keys you can’t easily rotate, in systems nobody fully inventoried. An attacker can steal that ciphertext now and decrypt it later, once quantum computers can break today’s algorithms. Waiting doesn’t buy safety. It just leaves more secrets exposed.
If a secret has to stay secret for a decade, the migration plan has to exist now: what you encrypt, with what, for how long, and how you swap algorithms without rewriting the product.
Awareness starts the work. Crypto-agile design sustains it.

Post-quantum readiness should be built into your infrastructure and procurement decisions.
For CISOs, CTOs and C-suite leaders:
• Map cryptographic dependencies
• Test performance and interoperability
• Require vendor upgrade plans
Build a foundation that can grow with what you choose today.

e23 will be at @LunoGlobal's Institutional Digital Asset Conference, LIDAC26, tomorrow.
Come by our booth and say hello. Our CEO, @wuiyangee, and the e23 team will be there!
lidac.io/

1/3 Quantum computing and quantum security are no longer on the same business timeline.
@wef and @Accenture's 2025 report places quantum computing at medium maturity, but rates the risk of inaction on quantum security as high.
For financial institutions, the security work begins before the machine arrives. 🧵

Full WEF report weforum.org/publications/qua…

2/3 Start with a cryptographic inventory.
Map where cryptography protects data, payments, approvals and external connections. Identify the systems that cannot pause. Then, test the ability to change security controls before wider rollout.
PQC becomes manageable when the dependencies are visible.

3/3 @BancoSabadell's WEF case study shows how network-level crypto-agility can reduce disruption.
For tokenised markets, the same discipline must cover custody, identity, settlement and recovery.
For Malaysia, we're developing MerdekaL1 for that challenge. Beta planned for 2027.

1/2 National liquidity will increasingly move across bank accounts, payment rails and blockchain networks. As these systems connect, cryptography must evolve without interrupting settlement.
Banks can be directed to migrate, however public blockchains need network agreement. 🧵
2/2 A delayed blockchain upgrade can disrupt settlement.
Banks, payment providers, custodians, issuers and operators need to test the settlement path together.
MerdekaL1, a consortium-governed, post-quantum, crypto-agile Layer-1. Beta 2027.
Read Edmund Yong in @starbizmy.

Banks are racing to prepare for quantum threats, but blockchains risk falling dangerously behind as fragmented governance makes a coordinated security upgrade far harder.
thestar.com.my/business/busi…

Tokenised markets run on robust infrastructure: a dependable chain, market rails and institutional applications, all anchored by a base layer that can evolve as cryptographic standards change.
Introducing 𝗠𝗲𝗿𝗱𝗲𝗸𝗮𝗟𝟭, a post-quantum, crypto-agile foundation.
More at AiSEM@Selangor in October.


3/4 QVault's key feature is that PQC runs inside the hardware. The Trusted Platform Module (TPM) generates and uses the private keys internally, so they never leave the device.
💡 This matters because the cryptographic keys are unexposed to threats, creating a stronger line of defense from bad actors.

