

Domain Registration, Brand Protection, High Availability DNS. Management and security of your domain names, DNS & IT perimeter. Brought to you by @easyDNS
Toronto, Ontario
Joined February 2017
- Tweets72
- Following60
- Followers42
- Likes3



Pinned Tweet
Attention all Web3, blockchain, DeFi, Dapp, DEX and exchange projects:
Your domain names make you particularly vulnerable to Web2 risks that can teleport attackers right inside your perimeter.
Our white paper shows you how to defend yourself.
whitepapers.domainsure.zone/…

The Trezor client data breach has morphed into a snail mail attack, with affected clients receiving letters advising them to "migrate their wallets" - DO NOT SCAN THAT QR CODE, obiously.
Our write-up on it here:
domainsure.com/crypto/trezor…

Fake "Update Your W-8BEN" phishing email for @Wealthsimple making the rounds.
Keep an eye.
(Duly added to our threat-feeds).

Heads up @HyperliquidX and @bing - somebody is buying keyword search results for "hyperliquid login"
(All fakes have been added to the DS Threat feeds)


More info on the Domainsure threat feeds are here:
domainsure.com/threat-feeds/

The latest @Ledger spear-phish looks fairly convincing to the untrained eye - sent via what looks like a compromised @royalcanin email server and URL redirected via @SendGrid
the domain is dash-ledger .com and regged via NiceNic - DNS with @Cloudflare


The ultimate lander domain in this instance is
extend-ens . org - which was just registered on Aug 24.
We've already added this to the Domainsure Crypto Defender Thread feed (available here):
domainsure.com/threat-feeds/
Be careful out there, folks.


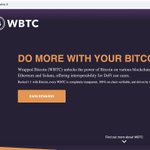
Somebody snagged the domain wbtc{.}fi and is running a wallet drainer off of it
They're driving traffic by dusting ETH addresses with the message "Visit wbtc{.}fi to earn rewards."
(Don't).
Metamask and Coinbase have already flagged the address, and it's been added to Domainsure thread-feeds.
domainsure.com/threat-feeds

Our honeypots have picked up Yet Another Malicious Domain targeting @Ledger users.
There is no new firmware fix.
There is no quantum vulnerability update.
There are only wallet drainers
This domain has been added to the Domainsure theat-feeds...
domainsure.com/threat-feeds/

Domainsure retweeted

More DNS FUD debunked by yours truly...

No, DNS can't be used to hack your AI chatBot - despite the impression you may have gotten from the @WIRED and @arstechnica articles implying that.
In our latest post, we take you through what those posts really mean (link in thread) 👇

No, DNS can't be used to hack your AI chatBot - despite the impression you may have gotten from the @WIRED and @arstechnica articles implying that.
In our latest post, we take you through what those posts really mean (link in thread) 👇

Domainsure retweeted
Because of all the quantum fud being amplified by retarded slop accounts on this site, phishers are now sending fake "Quantum Computing Vulnerability" notices with "upgrade" buttons that no doubt take to you wallet drainers.
We've already added this one to the @Domainsure threat-feeds.
