

Cybersecurity & ML
Zurich, Switzerland
Joined August 2025
- Tweets170
- Following99
- Followers52
- Likes192




Pinned Tweet
Why run "claude" when you can run "sclaude"?
Announcing SideKernel: an AI agent sandbox for macOS with a focus on usability.
When AI coding agents first arrived, many of us faced a dilemma that felt impossible.
We could give them free rein over our data and systems, putting both at risk, but letting them do great things unattended....
or we could use them cautiously and watch others, who accepted more risk by temperament (you can call it bravery, you can call it ignorance, and probably both would be right), move faster.
Either way, many of us were caught between a rock and a hard place.
For months I waited for a solution to come, either from the open-source community or directly from the frontier labs: some sandbox that offered reasonable security while also being easy to use.
Well, many sandboxes were indeed released, but almost all of them targeted production use cases, i.e. programmable agents built on SDKs.
From hosted services like E2B to open-source projects like microsandbox, that part of the industry matured and gained popularity quickly.
The more I tried using those sandboxes, however, the more I realized they tend to get in the way of the AI coding agents (e.g. Claude Code, Codex) most of us run daily in our terminals.
They were good solutions, but not for my problem.
As a result, I—and frankly, most of us—kept running those coding agents directly on our machines, or on clunky VMs, or on separate VPSs or spare Mac Minis… You get the gist.
For months I waited for a solution to come, either from the open-source community or directly from the frontier labs: some sandbox (a term that is overused today, but that's a discussion for another time) that offered reasonable security while also being easy to use
So when my MSc practicum at School of Cybersecurity and Privacy at Georgia Tech came around, I decided to built the sandbox I wanted.
SideKernel runs your coding agent inside a lightweight VM on macOS, with a real virtualization boundary between the agent and your machine, while feeling almost as quick as running it directly.
It's open source under Apache 2.0.
Try it out, compare it break it, and tell me what you find (a ⭐ on GitHub helps too).
Thanks to Prof. Mustaque Ahamad for inspiring me to work in systems security through his course and supervising the capstone.
But also to the amazing TA and colleague, @eMADAK for the legendary guidance, and supervision along the way and during the capstone.
At last, I'm grateful to @kalio_late for pushing me and motivating me to release it, and to my colleague Stuart and to @epmatt_ for the many awesome talks around security, systems and infra as well as the awesome builder community of the @thejfloor
Try it out and let me know what you think: github.com/minoansecurity/si…


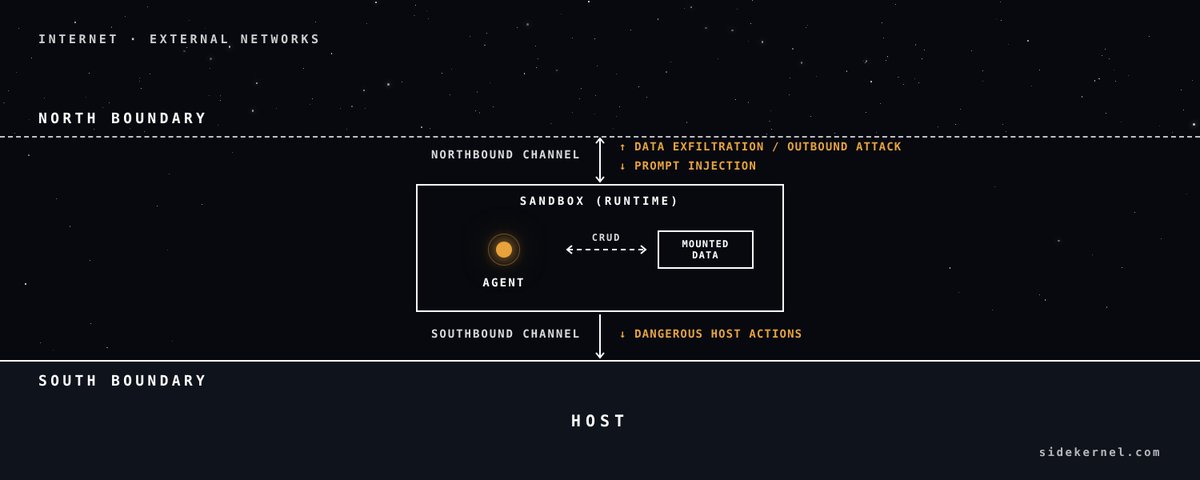
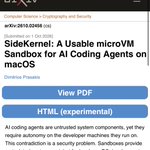
SideKernel is now available as a preprint on arXiv! 🚀
Today, an academic journey I started over 10 years ago finally comes full circle. I’ve worked immensely hard over those years, spending most of them balancing my studies with full-time work.
I’m incredibly grateful to @GeorgiaTech for the quality of education and opportunity it provided to me.
Now that the MS is over, I finally have the time to focus on the things I truly enjoy beyond coursework, including open-source software and vulnerability research.
Excited for what comes next ⏳

Refreshing to read! Bravo @vercel
