




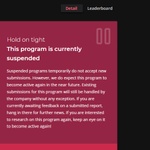

Approved for CVP. Mythos showed up for a few hours, then disappeared. Account still says CVP, but every cyber prompt gets blocked again. Ticket’s been open for days with no reply. @AnthropicAI @claudeai can someone actually check the grant?
Devyn retweeted

Building a hack-bot orchestrator in my free time called "Wild Hunt". Running it hard for 2 weeks while iterating and fixing bugs. Can run on 5-6 programs in parallel - aiming to scale to 20.
Few RCEs and ATOs. Duplication still high but will keep scaling: 🧵

Devyn retweeted

Switching from Claude Max to OpenAI Pro has been one of the best decisions I've made lately. No getting flagged for ~cyber~ despite being CVP-approved. The ChatGPT Work app is miles ahead of Claude.
OpenAI is absolutely cooking. 👏
First CVE.
CVE-2026-85610
OpenPanel before 2.3.0
CWE-94 in chart formula evaluation
Auth’d project reader could get RCE in the API process and break org isolation. Fixed in 2.3.0.
Doesn’t hit like it would have before every model could spit out a finding. Still cool. First time seeing my handle on a CVE record.
github.com/Openpanel-dev/ope…
cve.org/CVERecord?id=CVE-202…

this was very unclassy for the founder of a b̶i̶l̶l̶i̶o̶n̶-̶d̶o̶l̶l̶a̶r̶ startup to say to someone who just gave free, accurate feedback on your site’s font loading.
After conversion finishes:
curl -b cookies.txt http://127.0.0.1:8083/stats
Renders the SSTI → command execution.
Fix in 0.6.27: strict source/destination format allowlists that reject the traversal before conversion starts.
Upgrade recommended.
Upload the EPUB as the non-admin user, note the book ID, grab CSRF from the edit page, then: (Adjust traversal depth to hit the writable cps/templates dir.)

PoC (≤0.6.26):
Build a flat EPUB containing attacker-controlled stats.html with SSTI:

ALT full poc: https://pastebin.com/raw/7TbWiPP1
Root cause: /admin/book/convert/ accepted unrestricted book_format_to.
Calibre-Web appended it to the book path and passed it to ebook-convert. A traversal that resolved to an existing directory triggered Calibre’s OEB output mode, writing attacker-controlled EPUB files (including a malicious template) into that directory.

Just stumbled on this…👀
Three live ClamAV 1.5.x memory corruption bugs (double free, ZIP desync that reaches RCE, STATS pointer leak). Full labs, PoCs, and patches already public.
“The vulnerabilities were discovered entirely through AI. Author takes no credit — all glory to the Clankers.”
github.com/Zer0SumGam3/clama…
#InfoSec #ZeroDay #ClamAV #AI

