

Hack your supply chain before real attackers do.
Joined September 2026
- Tweets13
- Following11
- Followers406
- Likes15

Depi retweeted
We released a blog post @depi_ about Mean Time To Detect vs Meant Time To React, especially applied to Software Supply Chain
Beautifully written by @vm00z 🔥
depi.security/blog/20261002-…

Depi retweeted
We're building Depi Red Team.
Zero to a validated exploit in 3m 56s. Depi does the recon and validation, the red teamer builds the exploit locally on top.
We also used Bug Bounty as a sandbox for our research and got XX,XXX$ bounties with it ;D
Our team went from hours or days to minutes on the hardest exploits.
I need help from Red Teamers and get some feedback. DM me what's missing or let's jump into a call ;D

Depi retweeted
Proud to partner with Aikido Security to power Depi's malware detection 🤝
Attack dependencies before threat actors do. Detect malware with Aikido's feed. React with context from our dependency graph.
Three layers, one platform.
Hack the planet 🔥

Aikido Intel now powers @depi_'s malware detection.
Depi maps every package, pipeline and maintainer between you and a supply chain compromise. Aikido Intel's feed now powers the malware detection behind it.
💜🤝💙
Learn more about Aikido Intel: intel.aikido.dev/

Depi retweeted

Aikido Intel now powers @depi_'s malware detection.
Depi maps every package, pipeline and maintainer between you and a supply chain compromise. Aikido Intel's feed now powers the malware detection behind it.
💜🤝💙
Learn more about Aikido Intel: intel.aikido.dev/
Depi retweeted
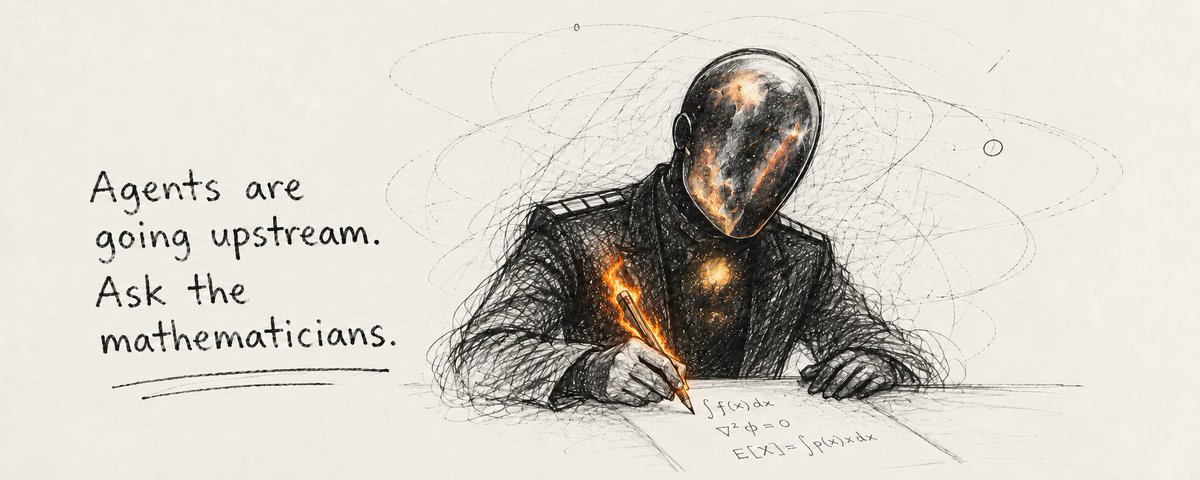
Your security team went home.
The agent looking for a way into your stack didn’t.
Agents are going upstream. Ask the mathematicians.
Depi retweeted

I have an inside source, you're gonna wanna watch this hacker closely - crazy stuff going on.


Depi retweeted

You should definitely follow her work & research at @depi_
I have it on good authority that there will be multiple bangers (including a new technique!)


