





Flux Proxy SDK being dropped as part of ongoing compromise global[.]proxystream[.]st


Surreal to see some of the @synthient research mentioned by @AnthropicAI :) Super cool
anthropic.com/research/self-…

One of my friends found this pretty bug that allows you to impersonate Grok bot. Reported but never heard back.
nightd.dev/blog/impersonatin…

The IPWeb operators have purged everything from GitHub post-publication. Guess they aren’t a fan of #opensource 😔


> be chinese financially motivated threat actor
> create big ass fuck off botnet
> botnet transforms machines into proxies
> sell proxies on IPweb
> make big money
> millions of dollars
> accidentally push source code of botnet to GitHub
> accidentally push source code of botnet to GitHub
> @synthient finds it
> hello mr synthient can i have the goop code?
> "sure?"
> gives
> download it
thank you mysterious group of chinese people for accidentally uploading your botnet code to github. i have goop code now


Chinese-speaking proxy services are often grouped together as belonging to IPIDEA or Kookeey. In reality, the ecosystem is incredibly diverse and includes a number of custom botnets. This report focuses on one of those providers: IPWeb.

In our latest research, we reveal the inner workings of APSolo, one of the largest Chinese proxy botnets. The botnet continues to fuel DDoS attacks, fraud, and other cybercrime. Using multiple source-code and infrastructure pivots, we linked it to the Chinese proxy provider IPWeb.
Provider: IPWeb
Malware Family: Proxyware.APSolo
Size: 800K - 1.2 million daily active IPs
Full Story: synthient.com/blog/ipweb-pee…


Ben retweeted

Two Australian TeamPCP members were arrested today.
Here's the arrest footage:
Arrest of 23 year old in Mandurah.
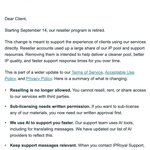
IPRoyal planning to terminate their reseller program starting September 14th. This likely comes following the NetNut disruption. Will be interesting to see if this includes their own reseller brands such as Marsproxies.

Orbit is highly active with a large portion of attacks targeting #discord along with small websites. Interestingly there is another C2
coxm[.]duckdns[.]org responsible for delegating attacks.


#Sysorbit is an Android DDoS botnet disguised as "Google Play Service." It is derived from the Mirai family but has been thoroughly adapted for the Android environment.
apk hash: 6b926acb42e6519747d72ddb0bfecb8f4e346d28
cnc: tblcxmo.duckdns[.org udpatetbl.duckdns[.org


Ben retweeted

Winners of the Claude, Twitter Premium and Synthient accounts!
Claude:
@jackskelt
@man_gtx
@normanbyte3
@gr3ys3c
Twitter Premium:
@d1ngbat_
@Jus7rai
@sooftware_
@0xRavenspar
@aim120c8
@_mayrasantiago
Synthient Account:
@foilmanhacks
@inf0stache

New giveaway alert
Our friends at @synthient wanted to giveaway some goodies for you nerds
2x Synthient Researcher Accounts - $40k
4x Claude Pro 1 Year Subscriptions - $400
6x Twitter Premium 1 Year Subscriptions - $600
If you want to enter this giveaway please do the following
Like the post, Comment what you want and why, and follow both @synthient and @vxgiveaways
Goodluck to all, picking winners next week