

Believer in @gonka_Ai
Succinct City
Joined November 2021
- Tweets3.4K
- Following1.4K
- Followers592
- Likes4.4K




Razdor retweeted

Huge congrats to Succinct’s Rahul Dalal, one of the cryptographers behind FlashProve, @AnthropicAI’s provable inference system built on zkSNARKs.
Why: Today, AI runs on a “just trust me” model. Users can’t verify that a response came from the model they chose, or that an attacker didn’t tamper with it along the way. As AI takes on higher-stakes work, that create tension for users, labs, and regulators alike.
What: Researchers from Anthropic, EPFL, MIT, and @SuccinctLabs built FlashProve, a system that lets a model provider commit to a specific model and then prove each response was produced by it, without revealing the weights. Under the hood, it uses zkSNARKs, the same cryptographic technology Succinct uses to secure $13.5B in deposits on Ethereum L2s.
So What: FlashProve proved Llama 4 Maverick, a 400B-parameter LLM, at 110 tokens/sec on a single H100 GPU, with ~19 MB proofs. That puts proving at roughly 70 to 95x the cost of running the model. The previous standard for the same model was ~0.02 tokens/sec.
What’s Next: FlashProve is still a research prototype, but it’s a step change toward the question we asked with Flock earlier this year: how close can proving get to computing? The closer it gets, the less reason there is to release any output without a proof attached.
Congrats again to Rahul and the FlashProve team, and great to see @Starknet, @Mantle_Official (proven by Succinct), and several zkML projects cited.


Razdor retweeted

Happy 6th Birthday, @NEARProtocol 🎂🔥
Our home chain turns 6. We're proud to ship on it every single day 💛


✦ 6 years on mainnet
✦ 10 shards
✦ 600ms blocks
✦ $34B+ Intents volume
✦ 3B+ Confidential Intents volume
✦ 150M+ Confidential TVL
✦ 10k+ NEAR Legion members
✦ 100% uptime
Grateful to the worldwide ecosystem of validators, devs, dApp teams, researchers, users, community members, legionnaires, and more who have helped shape NEAR into the groundbreaking protocol it is today. Side by side, we continue pioneering the onchain AI economy, connecting ecosystems, and are giving users back their sovereignty.


Razdor retweeted
how to get?
1) join my ref link near.com/login?ref=vhi2xcsn
2) deposit money. 100-200-300 $
3) trade perps
4) do swaps
5) onboard Referrals using your ref link. 2-3-4 friends is ok
6) ask friends do swaps
7) put some limit orders (yes intents can do limit orders)
begin ASAP. Fast start - more points


Razdor retweeted
🔥 We promised your activity would be rewarded - and here it is!
Thanks to our work and partnership with @NEARProtocol , our users are getting solid rewards in the NEAR@3.33 drop 🤘
⏳ Only one thing left: $NEAR has to hold above $3.33 for 72 hours
🪙 Once it does, your rewards will be added automatically to your confidential balance on near.com (near.com/). No extra apps, no extra steps ❤️
🏆 To give you an idea: user #99 in the snapshot is set to receive around $2,800 💵
👀 And the most important part - this is not the end. The next drop will be announced very soon: NEAR@6.66. Don't miss it
You can check your position at near.com/near-x

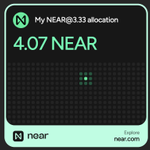
My NEAR@3.33 allocation is in: 4.07 NEAR 💚
The next phase of NEAR@X is coming.
Join me on near.com with my referral link:
near.com/login?ref=lof5ylsp

1
36


Razdor retweeted

A guy just turned standard home Wi-Fi into a radar that sees through walls.
Over 62,000 stars on GitHub for a system that tracks humans without using a single camera lens.
It doesn’t just know you’re there.
Watch what happens when a person lies down on a bed in another room.
The AI instantly maps their exact posture, tracks their breathing, and calculates their heartbeat in real-time.
No optical surveillance, no privacy leaks - it just analyzes how your body disrupts ordinary radio waves.
The whole thing runs on a tiny $5 microchip.
Traditional security requires a direct line of sight and invades your personal space.
Now, your Wi-Fi router is a camera that sees through solid brick.
Readers added context they thought people might want to know
RuView needs extra ESP32 nodes (~$9) with custom firmware; standard home routers alone cannot. Docker defaults to simulated data. Research concept is real; audits/users report short of advertised exact through-wall pose, breathing and heartbeat.
github.com/ruvnet/RuView
korben.info/en/wifi-densep…
arxiv.org/abs/2301.00250


Razdor retweeted
Migrating Ethereum to post-quantum security is a herculean task. That's why we released VEIL, a new compiler.
Succinct's SP1 — the protocol Google used for generating ZK proofs — relies on a Groth16 wrapper. VEIL swaps the elliptic-curve dependency for a PQS hash-based one.

Today a crazy quantum story just got wilder.
On March 31, the Google Quantum AI team published a landmark result on Shor's algorithm for elliptic curve cryptography. Technically, the paper was a bombshell: a dramatic 10x improvement over the state-of-the-art. As a stunt and wakeup call to the blockchain space, those optimisations were illustrated on secp256k1, the elliptic curve underlying Bitcoin and Ethereum signatures.
But perhaps the most striking part of the paper was sociological, not technical. Instead of following standard academic process, the optimisations were kept secret, hidden behind a zero-knowledge (ZK) proof. Google's accompanying blog post mentions they "engaged with the U.S. government". The ZK proof demonstrates the existence of algorithmic improvements without leaking details. Academic censorship with ZK, a historic first!
As a co-author of the Google paper I witnessed some of the context surrounding this censorship. To be honest, multiple aspects of that context don't sit well with me. As much as I believe the general public ought to know more, I am limited in my ability to whistleblow. Though let me be clear about one thing: the Google team's professionalism has been absolutely exemplary, and they deserve nothing but praise.
Censorship has a way of backfiring. The Streisand effect, where an attempt to bury something only draws more attention to it, is exactly what's unfolding today. First, Google's key optimisation has been rediscovered by the French. And in a thrilling turn of events, a collaborative Shor-at-home challenge just launched. The initiative, available at ecdsa[.]fail, breached a new Shor world record in a matter of hours.
Let's start with the rediscovery. Just two months after Google's paper, French quantum expert André Schrottenloher cracks the main secret optimisation. His paper, titled "Optimized Point Addition Circuits for Elliptic Curve Discrete Logarithms", landed on the arXiv today. Big congrats to André, who beat several other nerdsnipped experts to it. In a blog post also published today, Craig Gidney, the world expert on Shor optimisations, revealed that he'd been sitting on this very optimisation for a whole year under censorship pressure.
Interestingly, André missed a handful of minor optimisations, both from Google's original publication and from improvements found since. It's plausible there's still plenty of juice left to squeeze out of Shor, and this is exactly what the ecdsa[.]fail challenge is about. The verifier program developed for the ZK proof does double duty, automatically filtering for valid submissions. Dozens of compounding small and micro improvements are rolling in. As of the time of writing there's an 8.4% improvement to Google's circuit, as measured by the product of logical qubit count and Toffoli gate count. Nice!
The nerdsnipping ran deeper than anyone expected. Over the last few weeks it became clear it extended well beyond André and other quantum experts. Behind the scenes, a small army of amateurs quietly got to work. Inspired by Karpathy-style autoresearch, they turned AI on Shor. Ironically, the verifier program for the ZK proof makes an ideal reward function for AIs. The barrier to entry for this modern style of research is refreshingly low, with several non-experts, even a teenager, finding nice optimisations. Get in touch if you'd like to join a Telegram group with fellow autoresearchers :)
Part 2: neutral atoms and qday
The story doesn't end with Google. On the same day Google went public, a stealthy startup called Oratomic published its own Shor paper in a coordinated release. It made a splash, ultimately becoming the most upvoted paper on scirate[.]com, a website ranking arXiv papers.
Oratomic's claim was wild. By building on Google's logical optimisations and applying custom physical optimisations for neutral atoms, they claimed just 10K physical qubits were sufficient to run Shor's algorithm on secp256k1. That number is mind-bogglingly low.
Knowing essentially nothing about neutral atoms when Oratomic's paper landed, I was intrigued and decided to learn more about the tech. I fell straight down the rabbit hole and spent a couple hundred hours on the topic. I got a little obsessed and watched every YouTube video I could find and spoke to a bunch of experts.
My conclusion? The tech is real, very real. Even Google recently decided to start a neutral atom lab, a notable pivot from their sole focus on superconducting qubits. If you care about qday, i.e. the day a quantum computer will break the first piece of cryptography in production, neutral atoms demand your attention. I shared some of my learnings on Shor and neutral atoms in a 30min talk at the ZKProof cryptography conference. You can find it on YouTube by searching "zkproof neutral atom".
Here's an interesting observation about this duo of breakthrough papers: neither Google nor Oratomic say a word about what their results mean for qday. No timelines. Zero. Nada. That is especially baffling given that the whole point of whitehat quantum cryptanalysis is to inform qday estimations and help the general public make good decisions.
So let me attempt to partially fill the silence, similarly to what Scott Aaronson did in his April 29 post. Given everything I know, including scary non-public information, I now put the odds of qday by 2032 at 50%. 10% by 2030.
Anecdotally, the US government has its own date: 2035. Originating at the NSA and later adopted by NIST, it's when branches of the US government will be disallowed from using quantum-vulnerable cryptography. In plain language: with hindsight, that date is a joke and should be discounted entirely. I don't see how NIST avoids being forced to pull it forward by years.
Part 3: post-quantum cryptography
There are good reasons to sound the alarm today, but please do not panic. Rushing carelessly towards immature post-quantum cryptography is a recipe for disaster. IMO a good target date for migration is 2029, roughly 3.5 years out. 2029 happens to be the date selected by Google, Cloudflare, and the Ethereum Foundation.
These days most of my time goes to safely migrating Ethereum towards post-quantum cryptography as part of the broader lean Ethereum effort. There's a lot to do. We need to rip out and replace BLS signatures at the consensus layer, KZG commitments at the data layer, and ECDSA signatures at the execution layer.
The plan to get there is compelling, and is based on hash-based cryptography. Within the Ethereum Foundation we've developed a Swiss army knife called leanVM (github[.]com/leanEthereum/leanVM) powered by the magic of hash-based SNARKs. Thanks to truly exceptional work by Emile, Thomas, and others, its performance is derisked. Regarding security, leanVM is a jewel, a minimal zkVM crafted for end-to-end formal verification and maximum security.
Want to help? There are two $1M initiatives. First, the Proximity Prize (proximityprize[.]org). Solve a long-standing mathematical conjecture in coding theory, improve hash-based SNARKs, and go home a millionaire. Second, the Poseidon Initiative (poseidon-initiative[.]info), offers $1M for breaking Poseidon, the SNARK-friendly hash function.
Razdor retweeted
near.com/login?ref=vhi2xcsn
1) deposit to confidential balance
2) do swaps
3) n@x
thanks later
Razdor retweeted
Succinct is bringing zero-knowledge proofs to @base. The upcoming Azul upgrade will use SP1 to prove every transaction on the network.
Succinct will soon secure over $10 billion across major rollups, making SP1 the most widely deployed zkVM in production.


Razdor retweeted

We are officially past the point where decentralized AI inference is only a philosophical argument
Over the last 24 hours, Gonka processed hundreds of thousands of inferences and billions of AI tokens across the network. Across a decentralized network of real hardware built by dozens of participants - companies and individuals
This is still early and rough around the edge, people are still hitting limits, but when they do, it’s another milestone for the network. But this is exactly how new infrastructure starts. Perfection is not important, usability is. It is already real, being used, and improving faster each week
The demand for inference is already coming from millions of developers, agents, builders, and users around the world. The question is whether this demand will keep flowing into a few centralized providers or whether it will drift towards an open, verifiable, decentralized alternative
If you want decentralized AI to exist, use it. Try the inference, build with it, help other people connect, launch a swarm of agents, and try to bump into the limit to push it further. Every request, every test, every fix, every GPU, every new user makes the network stronger
Bitcoin started this way. This is how open infrastructure wins

Razdor retweeted
📢 To SP1 Users: We will be removing support for v5 on the Prover Network on Tuesday, May 19th, 2026.
If you have not already, please upgrade to v6 with this helpful migration guide:
docs.succinct.xyz/docs/sp1/g…
SP1 Hypercube (v6) delivers up to 4x faster proof generation. V6.2.0 is the latest build with the most recent security and performance upgrades.
github.com/succinctlabs/sp1/…
If you have any questions, DM us or open a GitHub.
Razdor retweeted

Phase 3
Controlled Reopen live 12th May in between 5-10PM UTC
Expected:
• User access is restored
• Liquidations are paused for 24 hours — use this window to add collateral or repay debt before the liquidation bot resumes
• Margin trading positions must be closed within 24 hours — no new positions can be opened
• After 24 hours, all open margin positions will be force closed
Note:
Normal liquidation thresholds won't apply during this period, but forced liquidation can still occur if your real collateral falls below your real debt.
Razdor retweeted

It's been a year and a half since we first announced OP Succinct: our flagship product to secure blockchains with ZK technology.
Today, we're proud to be working with @base, one of the largest L2s, to secure billions in assets on their chain.

Base is partnering with Succinct to bring zero-knowledge proofs to Base Azul.
SP1 will prove $7.4 billion in deposits as @Base joins a growing list of major L2s adding validity proofs to their roadmap with Succinct.