

35K+ YouTube subs | Software Engineer who ships AI apps | Scaling AI first development Agency | DM for AI SaaS development
Joined September 2020
- Tweets1.4K
- Following224
- Followers855
- Likes1.4K



CodeBucks⚡ retweeted
You’re paying for CODEX and still not using the full limit.
I fixed that with a dot:
1. I made a dot and connected it to 2–3 codex cloud environments
2. I point it at specific gitHub repos. It sends the right tasks to codex in the cloud, then tells me when it’s done or needs my approval.
3. If usage is still left, I ask it to list every task we should finish before the reset. It already knows my work, so the suggestions are actually good. I just pick from the list and send them.
4. It also runs scheduled jobs for me: backlink ideas, SEO fixes, small scripts. Those run on its own VM and report back every day.
5. Same dot handles local codex desktop app too. I tell it the task, it hands it to the right project
The dot is what turns leftover usage into finished work plus I don't open the sidebar anymore nor I have to craft full prompts.

CodeBucks⚡ retweeted
refactored one mono repo to standalone app using gpt-6-astra high as a main agent and gpt-6.1-sol-max as sub-agents and guess what only took 7-8% of my weekly usage limit.
It's all on codex cloud, took only 2 hours🙌🏻

CodeBucks⚡ retweeted
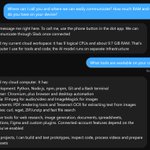
This is INSANE!
dots basically gets its own cloud computer with:
• 9 logical CPU cores
• ~9.7 GiB RAM
• python, node.js, npm, pnpm, git + bash
• chromium + browser/desktop automation
• ffmpeg + Imagemagick
• pdf tools, ocr, curl, wget, zip/unzip
• web research, image generation, docs, spreadsheets, presentations, figma + plugins
and the actual AI model runs on separate infrastructure.
we're basically giving AI agents their own computers now.🤯
if you're on openAI subscription then deploy your side-projects in dots care instead of spending on VM😂

ALT A screenshot of conversation with chatgpt dots
CodeBucks⚡ retweeted
deploying Next.js to cloudflare just got a lot easier.
before migrating, just run:
npx vinext check
It scans your project and tells you exactly what’s supported, next.js imports, config, libraries, App router features, and more.
Mine came back 100% compatible 👀
vinext is making cloudflare a much more interesting option for next.js apps. It's pretty easy to use, just read the blog post you'll know.


Vinext 1.0 graduates from an AI experiment to a production-ready framework, letting developers run Next.js apps on Vite. This release brings advanced cache warming, broader compatibility, and an automated testing pipeline. cfl.re/4dcK6hk #BirthdayWeek

CodeBucks⚡ retweeted
Opus 5.5 designing website directly on Figma using figwright MCP server/plugin!
running on medium reasoning and all images are generated with the help of gpt-5.6-sol which controlled by Opus through openAI's official claude code plugin.
website concept: ecom landing page for single product
This is one shot without adding any skills or guidance except for basic instructions and role based prompting.
CodeBucks⚡ retweeted
Anyone looking for new portfolio they can checkout my last video tutorial, I have open sourced the final code.
You can check the repo from here:
github.com/codebucks27/Nextj…
don't forget to star⭐ the repo 😉


Your portfolio gets ~10 seconds to make an impression.
And most developer portfolios look the same, so I recorded a full tutorial building one that doesn't:
🔸day/night hero with live video backgrounds
🔸real-time visitor weather widget
🔸Smooth scroll animations
🔸an editorial design system (no shadows, no bold, one accent)
It's developed using next.js, tailwind CSS, and framer motion.
Full live portfolio and tutorial links are in the first comment 👇
(It's quite long so I can't upload it here on X)
CodeBucks⚡ retweeted
we're hiring frontend engineers and design engineers at @dodopayments.
we're looking for people who care about the details - how a product works, how it feels, and everything between design and code.
frontend engineer → build fast, reliable product experiences used by businesses around the world.
design engineer → sit closer to the intersection of design and frontend. prototype, obsess over interactions, and turn ideas into polished product.
we care less about your resume and more about what you've built. side projects, open source, experiments, products you shipped because you wanted them to exist.
onsite in bengaluru.
know someone great? send this their way. apply link in the first reply.

CodeBucks⚡ retweeted
That's why you use stricter rules in Agents.md file.
and human review should be involved on each iteration.
here are few instructions I put in my claude.md and agents.md files:
## core principles
- **KISS & YAGNI.** Write the smallest amount of code that solves the problem correctly. No speculative abstractions, config options, or features nobody asked for.
- **Boring beats clever.** Prefer the obvious solution. code is read far more often than it is written, optimize for the next reader.
- **Existing code is context, not gospel.** Read the surrounding code first and stay consistent with its conventions when they're sound. But never copy a pattern just because it's already in the repo it may be flawed or legacy. Use the best pattern for the job, and briefly note when you deviate from what's there.
- **Follow official best practices** of every framework and library in use, use them the way their documentation intends, not through workarounds.
- **Simplicity is a feature.** If a change makes the code harder to understand, it needs a strong justification.
CodeBucks⚡ retweeted

Amazing video for learning Tailwind CSS v4, Framer Motion, React 19, and shadcn/ui 🔥 @code_bucks
youtube.com/watch?v=1qJEZVr6…
CodeBucks⚡ retweeted
Codex just freed 100 GB of junk on my C: drive.
few days ago my C: drive hit 16.8 GB free and windows started panicking.
instead of deleting random stuff like i usually do, i gave Codex read-only access and asked it to figure out where my storage actually went.
got almost 100 GB back without breaking anything. here's what it found👇🏻🧵
CodeBucks⚡ retweeted
I don't really buy the "rogue AI escaped its sandbox" framing.
yes, LLMs agents have demonstrated the ability to find and exploit sandbox vulnerabilities. that’s a fact.
but portraying this as an AI spontaneously deciding to "escape" with no help or enabling conditions, seems misleading.
these incidents happened in adversarial security evaluations, often with weakened safeguards, vulnerable infrastructure, or misconfigured sandboxes.
the capability is real but the “rogue AI” headline doesn't sound quite right.
CodeBucks⚡ retweeted
my obsession with making products look good is keeping me from shipping a bunch of them.
CodeBucks⚡ retweeted
Your heaviest user is now your most expensive one.
AI companies surveyed by ICONIQ expect gross margins near 52% this year. The saas playbook most founders are still copying was written on 80%.
that gap is not an accounting detail. It changes who you actually want using your product.
in classic saas one more heavy user cost close to nothing, so the person living inside your app all day was your best account.
put a model call in the middle of that same workflow and it inverts. on flat per-seat pricing, the user you work hardest to keep gets more expensive every month you keep them.
almost every AI feature I see shipped is priced before anyone measures what one run of it costs. usage grows, and six months later there is a meeting about optimising the prompt.
recently I went back to an old workflow of mine and pulled out the expensive model. replaced it with gpt-5.6 luna on high reasoning, which I assumed would eat the savings, because cheaper per token usually means more turns to get there.
It did not. The cost dropped roughly 70% lower.
I only knew the swap was worth trying because I knew what the old one was costing me.
so before your pricing page exists, take the one action your feature actually exists for and run it 20 times on real input. not the demo account. The messy one with many years of data in it. Write the number down.
everything useful follows from it. whether the expensive path runs on its own or waits for someone to click it, whether a cheaper model can take the first pass, and what a fair usage limit even looks like.
inference sits in cost of goods now, next to hosting, and it grows exactly as fast as the thing you are hoping succeeds.
CodeBucks⚡ retweeted
a feature should strengthen at least one real signal: activation, repeated use, or payment intent.
if nobody can explain which signal it serves, the feature is probably comforting the builder more than helping the user.
CodeBucks⚡ retweeted
$11+ in less than 2 minutes 😂
My fastest spend on LLMs, I forgot to change the model from gpt-5.5-pro to gpt-5.6-sol 🙈
using vercel AI gateway 👇🏻👇🏻

CodeBucks⚡ retweeted
A confused robot stops moving.
A confused AI agent updates 400 customer records and tells you it went great.
we accept this from robots because we can SEE the danger. An arm is swinging. A person is standing there. Obviously it should stop.
software hides that. but if your AI agent can edit customer data, it's the same problem with no visible arm.
Here's how I'd build it, step by step:
1. write down what the user actually asked for
before the agent touches any tool, save the plain facts:
who is asking. which account. which record. what it looks like right now.
You need this later when someone says "I never asked for that."
2. not all actions are equal. Sort them.
- reading data → fine, let it run.
- writing a draft you can undo → okay, with limits.
- changing money, emails, or customer data → a human approves first.
- deleting an account → the agent should not have this button at all.
ask one question per action:
if this goes wrong, how bad is it?
3. the agent can ask. It cannot give itself permission.
whe model says "I want to call update Invoice."
your backend decides if it's allowed.
never trust the agent to check its own permissions. That check lives in your server code, tied to the logged-in user same as any normal API. an AI agent is just another client. Treat it like one.
4. passing a schema check is not the same as being allowed
your code might confirm the request is well-formed. great. It still doesn't know:
- that invoice is already locked
- someone edited this record 3 seconds ago
- this account hit its plan limit
- this needs a manager's approval
Those are YOUR business rules. The agent has no idea. Run them yourself.
5. show the human exactly what's about to happen
Bad: "confirm this action?"
Good: "change invoice #3421 status from draft → sent.
This emails the customer. This cannot be undone."
If someone clicks approve without knowing what changed, you didn't build human review. You built a button.
6. make retries safe
If the request times out, did it save or not? nobody knows. so the code retries and now the customer is charged twice.
Fix: send a unique ID with each request. If your server sees that same ID again, it returns the first result instead of doing the work twice. This is called an idempotency key and it prevents a lot of pain.
7. "Done" is not enough. Say what actually happened.
- finished ✅
- half finished ⚠️
- blocked by a rule 🚫
- timed out ⏳
- crashed ❌
each one needs a different message and a different next step. A green checkmark that hides a half-finished job is worse than an error.
8. keep a log of the whole chain
Who asked → what the agent suggested → which rule ran → who approved → what ran → what happened.
When support gets a complaint, they should read this log. Not scroll through a chat history guessing.
The takeaway:
Safe AI agents aren't one smart confidence score.
They're eight boring checks in a row.
Boring is the feature.

CodeBucks⚡ retweeted
smaller pull requests do not automatically make a large feature easier to review.
The dependency order matters just as much as the diff size.
gitHub has released stacked pull requests in public preview. Each layer in a stack can be reviewed independently, while the existing checks and branch protections still apply.
That matters for agent-assisted development because one feature can produce several different review problems at once.
Imagine a feature split like this:
1. contract: types, interfaces, and API shape
2. data: schema changes and migration
3. UI: states, controls, and error handling
Putting all three into one pull request forces a reviewer to keep switching between product behaviour, data safety, and interface detail. Splitting them into three unrelated pull requests creates a different problem: their dependency is hidden.
A stack makes that relationship explicit.
The contract layer can be reviewed first. The data layer can build on an accepted contract. The UI layer can then be checked against both. Each review has one main question, but the sequence still represents one feature.
This does not remove the need to read agent-written code. It improves the shape of the work presented to the reviewer.
The practical test is simple: can someone approve one layer without first reconstructing every decision in the layers above it?
Review quality depends on how the change is arranged, not only on how many lines it contains.

CodeBucks⚡ retweeted
Your portfolio gets ~10 seconds to make an impression.
And most developer portfolios look the same, so I recorded a full tutorial building one that doesn't:
🔸day/night hero with live video backgrounds
🔸real-time visitor weather widget
🔸Smooth scroll animations
🔸an editorial design system (no shadows, no bold, one accent)
It's developed using next.js, tailwind CSS, and framer motion.
Full live portfolio and tutorial links are in the first comment 👇
(It's quite long so I can't upload it here on X)
CodeBucks⚡ retweeted
I disappeared from YouTube for almost 1.5 years.
It's been a while👀
Something's cooking... and it's the one of the beautiful thing I've ever made for this channel.
See you tomorrow. 🔔
Turn on notifications so you don't miss it!
Channel link is in the first comment. If you haven't subscribed yet, now's the perfect time. ❤️

CodeBucks⚡ retweeted
saw a post on top of HN saying DRY matters more with AI agents, not less. this matches what i see every single day. ( written by @ScottWRobinson )
agents don't know a helper already exists somewhere in the repo, they generate from whatever context is in front of them. if the same access check is copy pasted in three places, claude code learns that's the house style and happily pastes a fourth.
so these days i clean up duplication before pointing agents at old code, not because DRY is sacred but because every pattern in the repo is a pattern the model will repeat back at me.
messy code used to slow down the next developer who touched it. now it trains your agents to write more of it.
