
AppleInternal since 2014 @ChiptuneXT@ioc.exchange
Joined June 2013
- Tweets990
- Following358
- Followers1.3K
- Likes7.1K





ChiptuneXT retweeted

A new unpatchable vulnerability has been discovered for the iPhone XS and iPhone 11. The exploit enables booting an unsigned bootloader, which means tools like checkra1n or palera1n could be updated to support these devices.
This quoted post is unavailable.

ChiptuneXT retweeted

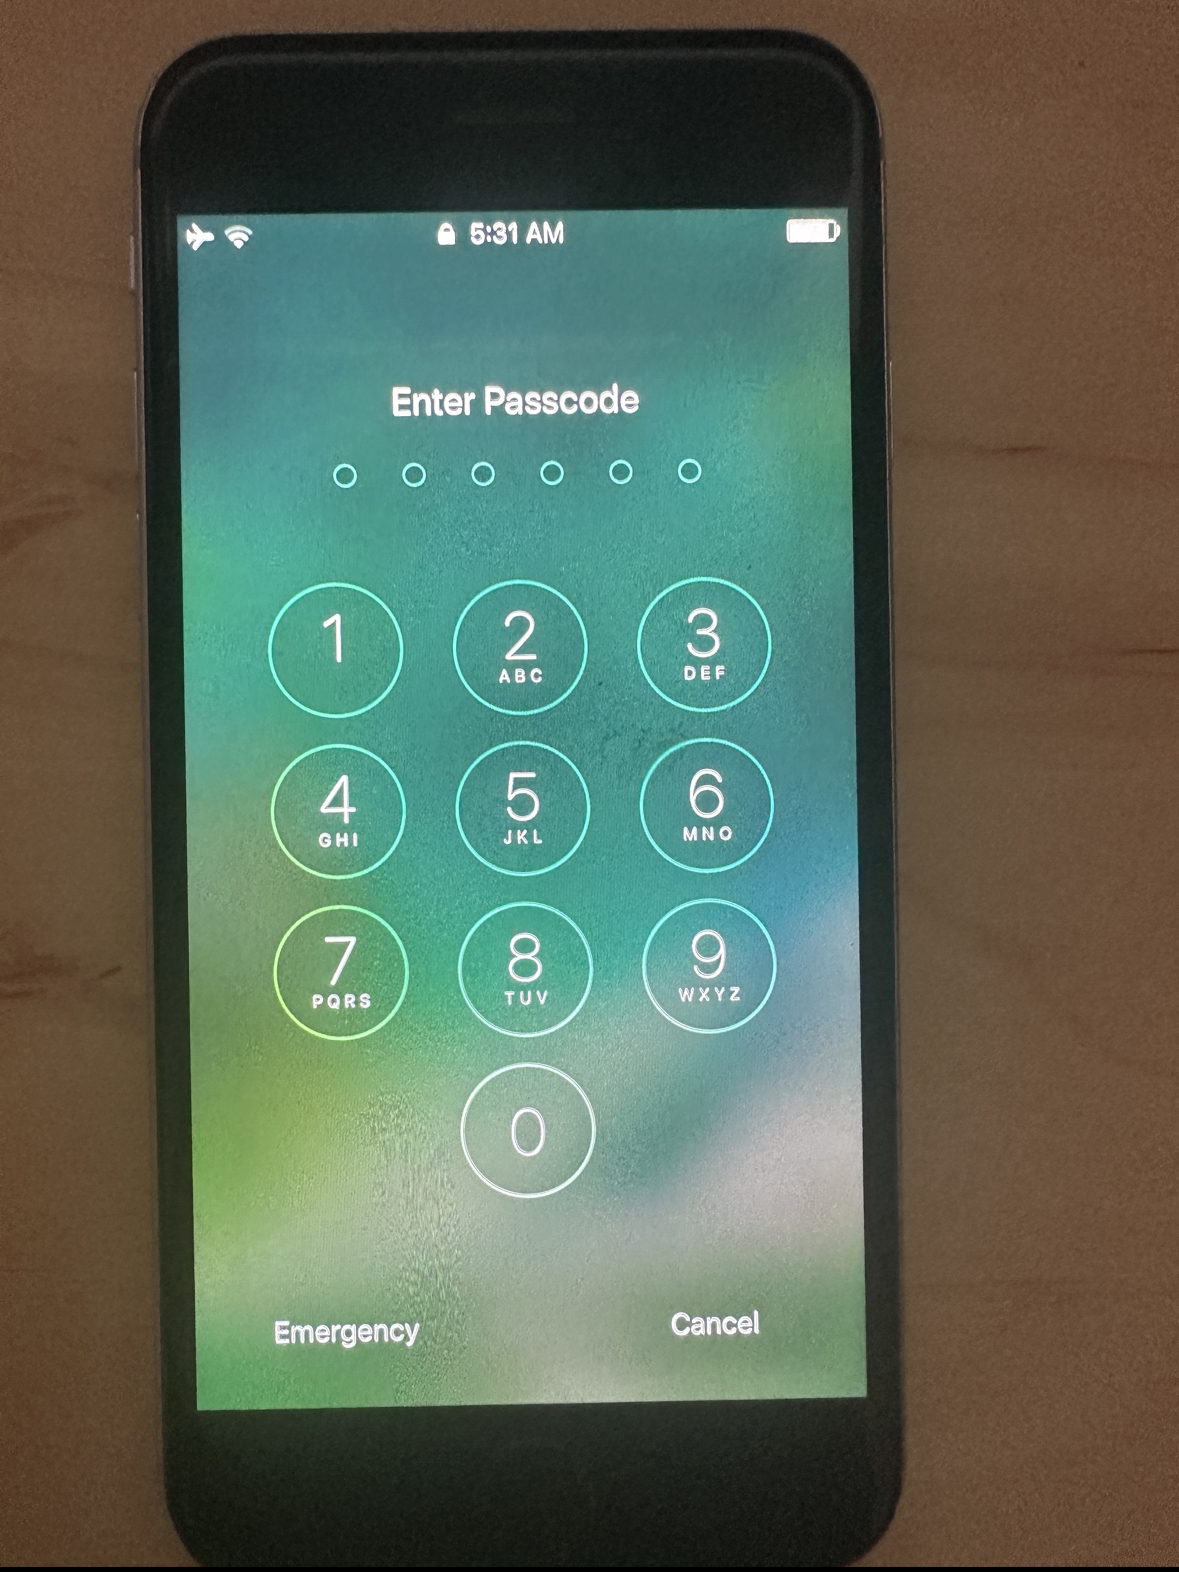
Throwback tech📱! Just got the iPod Touch 2G emulator running smoothly with QEMU. Multitouch and LCD are working nicely, and I’m able to open most of the applications 🎉.




ChiptuneXT retweeted

If you ever had trouble finding writable but SIP-protected files/directories, here's a quick little tool to help you:
github.com/gergelykalman/mac…
ChiptuneXT retweeted
wInd3x, the iPod Bootrom exploit 10 years too late q3k.org/wInd3x.html
ChiptuneXT retweeted
Part II of my blog post on emulating an iPod Touch 1G using QEMU is now available: devos50.github.io/blog/2022/…. This post contains instructions on how to build QEMU, prepare the necessary files, and run the emulator.


ChiptuneXT retweeted
Another checkm8 exploit 😄
github.com/0x7ff/gaster

ChiptuneXT retweeted

Happy #UntetherDay everyone. Fugu14 is now available on GitHub: github.com/LinusHenze/Fugu14

ChiptuneXT retweeted

Finally able to share what I have been working on for the past half a year! I built a set of tools for fuzzing SecureROM and managed to find and trigger checkm8 on A13 ;) No memory leak, so not exploitable though :( Everything is open source at github.com/galli-leo/emmutal…

ChiptuneXT retweeted

SHA256(bug.txt)= 7256683a6ff0271c35802ae9b859c8dfbd04c9716d1e23afce12322064acf604
Two years leading up to this.
Long live iBoot exploits.
KASSAR SAGN


ChiptuneXT retweeted

#checkra1n 0.12.3 released with support for iOS 14.5 and various bug fixes, including M1 support!
Grab it at: checkra.in/releases/0.12.3-b…


