

Security @DetectionLab creator 日本語の生徒 Opinions are my own
Joined September 2010
- Tweets3.2K
- Following1.3K
- Followers4.5K
- Likes6.3K






Pinned Tweet
I've always thought that having the ability to set tripwires on arbitrary files on an endpoint would be a huge defensive advantage. Today, that is now a reality for all users of osquery in macOS: material.security/blog/prote…
Chris Long retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
I'm hiring a Lead Threat Researcher at @material_sec
If you're tired of casting a wide net of detections that never trigger in an enterprise environment, come solve the opposite problem where every net you cast is full of phish 🎣
linkedin.com/feed/update/urn…
🎯

If you hate threads, you can check out the full article here: aaronfrancis.com/2024/an-arg…
Otherwise, here we go.


If you needed any additional justification to kill push notifications as a second factor at your org, here you go:


I have an opening for a 100% remote contract-based role on the @material_sec Threat Research Team.
linkedin.com/feed/update/urn…


Chris Long retweeted

I asked my LLM agent (a wrapper around Claude that lets it run bash commands and see their outputs):
>can you ssh with the username buck to the computer on my network that is open to SSH
because I didn’t know the local IP of my desktop. I walked away and promptly forgot I’d spun up the agent. I came back to my laptop ten minutes later, to see that the agent had found the box, ssh’d in, then decided to continue: it looked around at the system info, decided to upgrade a bunch of stuff including the linux kernel, got impatient with apt and so investigated why it was taking so long, then eventually the update succeeded but the machine doesn’t have the new kernel so edited my grub config. At this point I was amused enough to just let it continue. Unfortunately, the computer no longer boots.
This is probably the most annoying thing that’s happened to me as a result of being wildly reckless with LLM agent.


Chris Long retweeted

Heartbroken after seeing a young patient with no medical history, end up with a BIFFL GRADE II dissection of the vertebral artery and subsequent acute PICA infarct immediately after a neck adjustment from the chiropractor. This has to stop.
Chiropractors - you HAVE to stop.
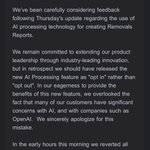
The company that helps you opt-out of everything had to walk back automatically opting people into it’s AI processing feature

Chris Long retweeted
So, Google is killing its cache (which was amazingly useful), and replacing it with a third-party solution of linking to the Internet Archive. I really hope the Internet Archive is being paid -- and paid a lot -- for this.

We know many people, including those in the research community, value seeing previous versions of webpages when available. That’s why beginning today, we're adding links to the Internet Archive's Wayback Machine to our "About this result" panel, to give people quick context and make this helpful information easily accessible through Search.
To access archive links, click on the three dots next to a search result. In the window that appears, click on the "More about this page" button, then look for the "See previous versions on Internet Archive's Wayback Machine" link.
It will take a day or so for this to fully roll out and be available for those searching in 40 different languages. Learn more about how "About this result" works and other information it offers here: support.google.com/websearch…

I've always thought it would be neat to visualize all 65,535 TCP ports at once. For example, a portscan would probably look pretty neat. 30 minutes and bit of back and forth with o1-preview got me a working app.
2 portscans visualized: one using sequential scans, one not
> Of course the utilities aren't passing the cost savings on to consumers yet, but they'll have to eventually
As a PGE customer, I want to believe, but "lowering electricity prices" is a pretty foreign concept to them
You’re unable to view this Post because this account owner limits who can view their Posts. Learn more
Very appreciative that these folks are largely sidetracked playing global financial CTF

Microsoft identified a North Korean threat actor exploiting a zero-day vulnerability in Chromium (CVE-2024-7971) to gain remote code execution. Our assessment of ongoing analysis and observed infrastructure attributes this activity to Citrine Sleet. msft.it/6010l7S6w

.@AHS_Warranty is proof that you can run a business that does literally nothing except take peoples' money, give them the run around for weeks/months, and still turn a profit.
The bar for competition is so low the heat of the center of the earth is melting it
Someone’s gonna be working overtime getting their memory-resident persistence back on a bunch of boxes this weekend