

Open-source builder. Solana developer tooling. Prev: @trufflesuite • @Consensys • @infura_io (DIN). Rust. Testing, observability, compilers & debuggers.
New York, NY
Joined January 2012
- Tweets420
- Following1.1K
- Followers241
- Likes781





Pinned Tweet
I went through @solanaturbine Builders program on purpose, with a background in blockchain and developer tooling already behind me.
Not to relearn the basics. To feel the gaps a newcomer feels, from the inside.
A thread on what I found, and why I'm grateful for it. 🧵
cds-amal retweeted
Really brutal. The phishing email is written quite convincingly, and it comes from the official Trezor domain.
At least tens of millions will be lost; hopefully not hundreds of millions. Insane f*ckup from Trezor.


Our third-party e-mail provider has been breached. Please be aware that the email named ‘Critical Security Alert: STM32 Entropy Vulnerability’ is not coming from us, and it’s a phishing attempt. Do not click on any link.
We have taken down the domain, and we are investigating the situation, including how the hackers got access to our legit domain.
cds-amal retweeted

this wild defcon talk is finally out
researchers created a fake defi startup, hired lazarus it workers, put them into a sandbox and recorded their tooling, workflows, and faces from inside the operation
starts at 5:46:09
youtube.com/live/_uYQr8hfpbI…

cds-amal retweeted

everyone check your rust codebases!!! short prompt
Check <repo> and this machine for the Aug 2026 crates .io compromise:
arrayref 0.3.10, append-only-vec 0.1.9, proc-macro1, proc-macro-en.
Grep every Cargo.lock/toml, then check ~/.cargo/registry for those crates, /tmp/rust-setup, egress to 23.254.165.112, and new LaunchAgents
since 2026-08-19. Report only, don't fix.


cds-amal retweeted
19 DeFi exploits that weren't in the open-source record — now fully reproducible.
If you work in smart-contract security, you know DeFiHackLabs — the standard, comprehensive library of reproducible on-chain exploit PoCs. A handful of exploits just aren't in it. We found 19, analyzed each one end-to-end, and published everything:
🔹 Foundry PoCs (offline-reproducible, exact on-chain profit) → github.com/sanbir/evm-hack-r…
🔹 Loadable PoC bundles → github.com/sanbir/evm-hack-p…
🔹 Interactive EVM Playground pages — step through each exploit opcode-by-opcode, with the vulnerability and every exploit step marked → crypto.training/hacks
All 19, newest first:
• BarnBridge SMART Yield (DAO governance capture) — crypto.training/hacks/2026-0…
• Bonzo Lend / Supra oracle (BLS zero-signature price forge) — crypto.training/hacks/2026-0…
• Hinkal (legacy-note multi-nullifier double-spend) — crypto.training/hacks/2026-0…
• Drips DaiHub (uint128→int128 cast) — crypto.training/hacks/2026-0…
• Gnosis Pay / Zodiac Delay (EIP-1271 signature bypass) — crypto.training/hacks/2026-0…
• ATOHook (Solady ReentrancyGuard storage collision) — crypto.training/hacks/2026-0…
• JaredFromSubway MEV bot (residual ERC-20 approvals) — crypto.training/hacks/2026-0…
• BoostHook (leveraged long, no post-open solvency check) — crypto.training/hacks/2026-0…
• Aurellion Labs (unprotected diamond re-init) — crypto.training/hacks/2026-0…
• ONTR (zero-owner onlyOwner free mint) — crypto.training/hacks/2026-0…
• BlastFOMOVault (claimBonus clone-churn) — crypto.training/hacks/2026-0…
• HeisenbergHook (Uniswap v4 fee-path hijack) — crypto.training/hacks/2026-0…
• Sat1Hook (grindable hook identity) — crypto.training/hacks/2026-0…
• QNT Reserve (EIP-7702 + permissionless BatchCall) — crypto.training/hacks/2026-0…
• Yearn stETH Accumulator (missing execute() auth) — crypto.training/hacks/2026-0…
• Blockchain Bets (ERC-1155 stake/transform inflation) — crypto.training/hacks/2026-0…
• TTSwap Market (permissionless initGood mispricing) — crypto.training/hacks/2026-0…
• WUKONG Staking (classical reentrancy in unstake) — crypto.training/hacks/2026-0…
• FoomCash / FOOM Lottery (Groth16 verifier with gamma == delta) — crypto.training/hacks/2026-0…
One recurring lesson: the interesting part of an attack is often not the drain. BarnBridge is the clearest example — the money left through the front door of the DAO. The real exploit was obtaining access: buy ~$2,200 of a dead governance token, stake it with a lock multiplier, and pass a proposal because quorum was measured on raw stake while votes counted multiplied power. So we reproduced the governance capture, not just the payoff.
And you can do all of this yourself.
github.com/sanbir/evm-hack-a… is an open-source, fully local EVM Playground. Point it at any exploit transaction — it pulls the verified sources, replays the whole thing opcode-by-opcode, and lets you mark the vulnerability and the exploit execution steps.
Then share your PoC however you like — open a PR to github.com/sanbir/evm-hack-p…, or publish it in your own repo, on IPFS, anywhere. No lock-in: the analyzer doesn't depend on evm-hack-poc or crypto.training.
The best way to understand an exploit is to reproduce it. The second best is to make it easy for the next person to.
#Web3Security #SmartContracts #DeFi #EVM #Solidity #BlockchainSecurity #OpenSource


cds-amal retweeted

LiteSVM 0.14.0 is out!
Enhanced performance and features are now synced in the right slot.
Node LiteSVM with Kit is 1.3.0
Thanks to all contributors! github.com/LiteSVM/litesvm/r…

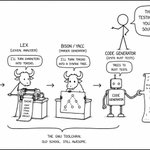
After days immersed in generator design, I suspect every mature ecosystem converges on the same architecture.
Lookup for known names.
Scope for introduced names.
Enforcement.
It wasn't invented.
It’s the shape of the job.
70
Every code generator has two namespace problems:
• resolving names that already exist
• introducing names that don't collide
Separate those and proc-macro design clicks.
open.substack.com/pub/cdsama…
cds-amal retweeted
Use npm v12 to mitigate some of the supply chain attacks! this should be read by anyone who runs any npm related software

🎉 npm v12 is here! Install scripts are now off by default, git and remote-URL deps no longer resolve unless you allow them, and 2FA-bypass tokens are starting to be phased out.
Details → socket.dev/blog/npm-12 #nodejs
cds-amal retweeted

12/ Live on devnet now.
App: vesting-position.vercel.app/
Docs: github.com/Canguilhem/Vestin…
If you're launching a token and need vesting infrastructure, let's talk.
Repost if you know a project that needs this.
@rajgokal @SOLBigBrain

That's why the Zen has stuck with me for so many years.
It's not a checklist @DiscRisknBisque
It's a collection of reminders that good software is often less about cleverness than about reducing unnecessary ambiguity.
1
2
48
That's a tiny design choice, but it's representative of a larger principle.
Software lives longer than we expect. Every bit of context you make explicit is one less thing a client, reviewer, or maintainer has to infer.
1
34
I was reminded of that last one while working on Rust macros.
Macro-generated code can use unqualified paths (which lean on whatever's imported at the call site) or absolute ones.
macro_rules! macros write `$crate::…` to name their own crate;
proc-macros emit `::crate_name::…`
The absolute form makes it clear where each symbol resolves and doesn't depend on the caller's scope. It's also structural insurance to avoid collisions when playing with other crates.
1
29