






ChatGPT 广告又扩了 26 个国家,
现在 89 个国家都能投,广告主已经超过 10 万家了!
照这个速度,ChatGPT 很可能成为最会赚钱的 AI 公司,以后广告业务说不定能跟 Google Ads 掰掰手腕
如果你是广告主,ChatGPT 广告值得试一试:用户在对话里会把需求说得很具体,比搜关键词时精准多了

OpenAI 又出位了!
这次 PHP 重大漏洞是由 OpenAI 最先发现的。

OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

Readers added context they thought people might want to know
Wiz Research wasn't the first one to discover the exploit. An independent researcher first discovered it: x.com/calif_io/statu…


这次 PHP 安全更新,官方提供的正式修复版本最低到了 PHP 8.2。只停机、不升级,解决不了根本问题。
老版本连官方安全补丁都接不到,想修也无从下手。
借着这次严重漏洞,日本那些还在使用老旧 PHP 版本的系统,是不是也该被“强制”推动升级了吧?php.net/archive/2026.php#202…


PHP 存在重大安全风险!
PHP 官方宣布,将于 10 月 21 日 23:00(日本时间)发布紧急安全更新,修复两项严重漏洞,CVSS 4.0 评分均达 9.2。
据安全机构提示,漏洞可能导致远程代码执行(RCE)。简单说,攻击者可能在未经授权的情况下,让服务器执行恶意代码。
网站被篡改、数据泄露,甚至服务器被控制,都可能成为后续风险。
最近日本频频出现用户信息泄露、异常登录等安全事件。这些事件是否与此次漏洞有关,目前还没有证据证实,但值得所有网站运营者提高警惕。
还在使用 PHP 的朋友,尤其是 WordPress 站长,请关注官方公告,修复版本发布后及时升级。
安全补丁不是可选项,别等网站被黑了才想起来更新。
厉害咯,PHP发生重大漏洞!
竟然惊动日理万机的高市首相;
亲自关心,亲自部署。

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X
PHP 存在重大安全风险!
PHP 官方宣布,将于 10 月 21 日 23:00(日本时间)发布紧急安全更新,修复两项严重漏洞,CVSS 4.0 评分均达 9.2。
据安全机构提示,漏洞可能导致远程代码执行(RCE)。简单说,攻击者可能在未经授权的情况下,让服务器执行恶意代码。
网站被篡改、数据泄露,甚至服务器被控制,都可能成为后续风险。
最近日本频频出现用户信息泄露、异常登录等安全事件。这些事件是否与此次漏洞有关,目前还没有证据证实,但值得所有网站运营者提高警惕。
还在使用 PHP 的朋友,尤其是 WordPress 站长,请关注官方公告,修复版本发布后及时升级。
安全补丁不是可选项,别等网站被黑了才想起来更新。
都快深秋了,日本最近的天气却反常地炎热。
根据日本气象厅的统计,日本大部分地区气温仍达到30℃以上,刷新了有气象观测记录以来的最晚高温纪录。
秋天的脚步越来越迟,反常高温却还在持续。
日本的季节感,似乎正在被打乱。


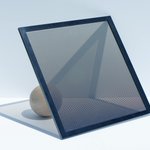
让玻璃也能发电!
松下宣布2029年开始量产一种会发电的玻璃。
名字叫「ENEFACE」,是把钙钛矿太陽電池和建筑玻璃做成一体。
一块最大1.8米高、1.2米宽,发电效率目标20%左右,跟现在常见的硅太阳能板差不多。
价格呢,目标控制在普通建材玻璃的5倍以内。
大阪的东阪急大楼重建,阳台部分已经定了要用它,海外客户也开始谈了。
松下还在研究叠层印刷的「串联型」,将来想把效率做到30%。
以后高楼的窗户不只是用来看风景,整栋楼都可能变成一座发电站。
真正的考验是价格,5倍的价差能不能被电费赚回来,决定了它能不能走出样板楼。


遭遇 App Store「订阅刺客」。
Bini Bambini Academy 出品的一款儿童绘画软件,居然每周收费 660 日元。一个没注意,就已经无意识订阅、消费了近 1 万日元。太狠了,连 ChatGPT 订阅我都没这么豪横地花过。
