

それでもきっと、満足した人生になるでしょう。 2822.⌐◨-◨ | #タグ付けOK
Joined February 2018
- Tweets26.2K
- Following4.8K
- Followers1.4K
- Likes62.8K






bubbly retweeted

Blast is shutting down: please withdraw your ETH from Spacebar before October 26, 2026
Blast has announced that it is shutting down its network. All ETH staked in Spacebar must be withdrawn before October 26, 2026.
How to withdraw
- Go to blast.spacebar.xyz/board/sta…
- Connect your wallet
- Select MAX, and unstake
- Your ETH is returned to your wallet on Blast right away
This page lists the wallets that still have 0.5 ETH or more staked in Spacebar: blast.spacebar.xyz/stakers/
Each entry shows the username, profile NFT, wallet address, and current staked amount. The page updates as wallets unstake.
If you recognize anyone on this list, please tell them to unstake.
Only your own wallet can unstake your ETH
bubbly retweeted

how to not get your crypto hacked.
bookmark this forever:
1. hardware
- buy direct from the company or an authorized retailer. never random resellers
- seed card already filled in when you received = scam. throw it
- ship it to a pickup point, not your home
- update firmware only through the official app
2. seed
- metal over paper. never a photo, cloud or notes app
- never enter your seed into a website or software wallet. restore only through your hardware wallet's official recovery
- don't split your seed manually. no redundancy and it leaks information. use shamir or multisig instead
- test your backup before funding: built-in check or wipe and restore. untested backup = no backup
- two copies, two locations. fire is a hacker too if seed burns
3. setup
- vault: a hardware wallet that never touches dapps
- hot wallet for daily use. burner for anything new
- bigger bags: passphrase on top. small decoy bag on the seed, real bag behind the passphrase
- back up the passphrase too, stored apart from the seed. lose it and nothing recovers your coins
- multisig when the amount justifies it. no single point of failure
4. signing (where most people get drained)
- verify on the device, never trust the website alone. bybit lost $1.5B to a compromised UI
- can't read it? don't sign it
- "free" signatures can drain you with zero gas (permits)
- one malicious eip-7702 authorization can delegate control of your entire account
- on solana, one bad tx can reassign your token accounts. simulate before you sign
- review approvals monthly. revoke what you don't need
5. sending
- never copy addresses from tx history. scammers plant lookalikes
- check the full address on the device, not just the first and last 4
- small test tx before every big one
6. machine
- a laptop that only touches crypto. clean browser, no random extensions
- download wallets only from the official site. app stores and search results are full of fakes
- never run "meeting apps", game builds or files strangers send
- never share your screen or install remote access. "support" asking for anydesk = scam
- bookmark every site. never click search ads
- surprise airdrops and NFTs = trap
7. exchanges
- unique password everywhere. 1password or bitwarden
- 2FA with an authenticator app or passkey. never SMS
- 2FA backup codes offline. not in email, not in cloud
- lock your SIM with a carrier PIN. sim swaps still work
- separate email only for crypto. nobody knows it
- turn on withdrawal whitelists
- not your keys, not your coins. move out what you're not trading
8. opsec
- don't flex your bags or your setup. wrench attacks are rising
- support never DMs first.
- avoid phishing emails, only trust official sources
- have an inheritance plan. dead keys are lost coins
9. quantum (check my other quantum tweet for detailed advice)
- not a threat today and anyone selling quantum panic is selling something
- btc: never reuse addresses. sending from one exposes its public key forever
- btc: park long-term coins in addresses that have never sent a tx. taproot (bc1p) and old p2pk show the key from day one
- btc: bip-360 proposes a step toward quantum-resistant addresses. not live. proposals also exist to freeze unmigrated coins
- eth + erc20: sending a tx exposes your public key. signing messages can expose it too so keep major bag on clean wallet
- sol: your address is your public key. exposed from day one. experimental winternitz vaults exist, not standard wallet protection
hardware rarely gets hacked. people do.
bubbly retweeted

⚠ Bitgetでハッキング
慌てて移動してGOXだけは注意

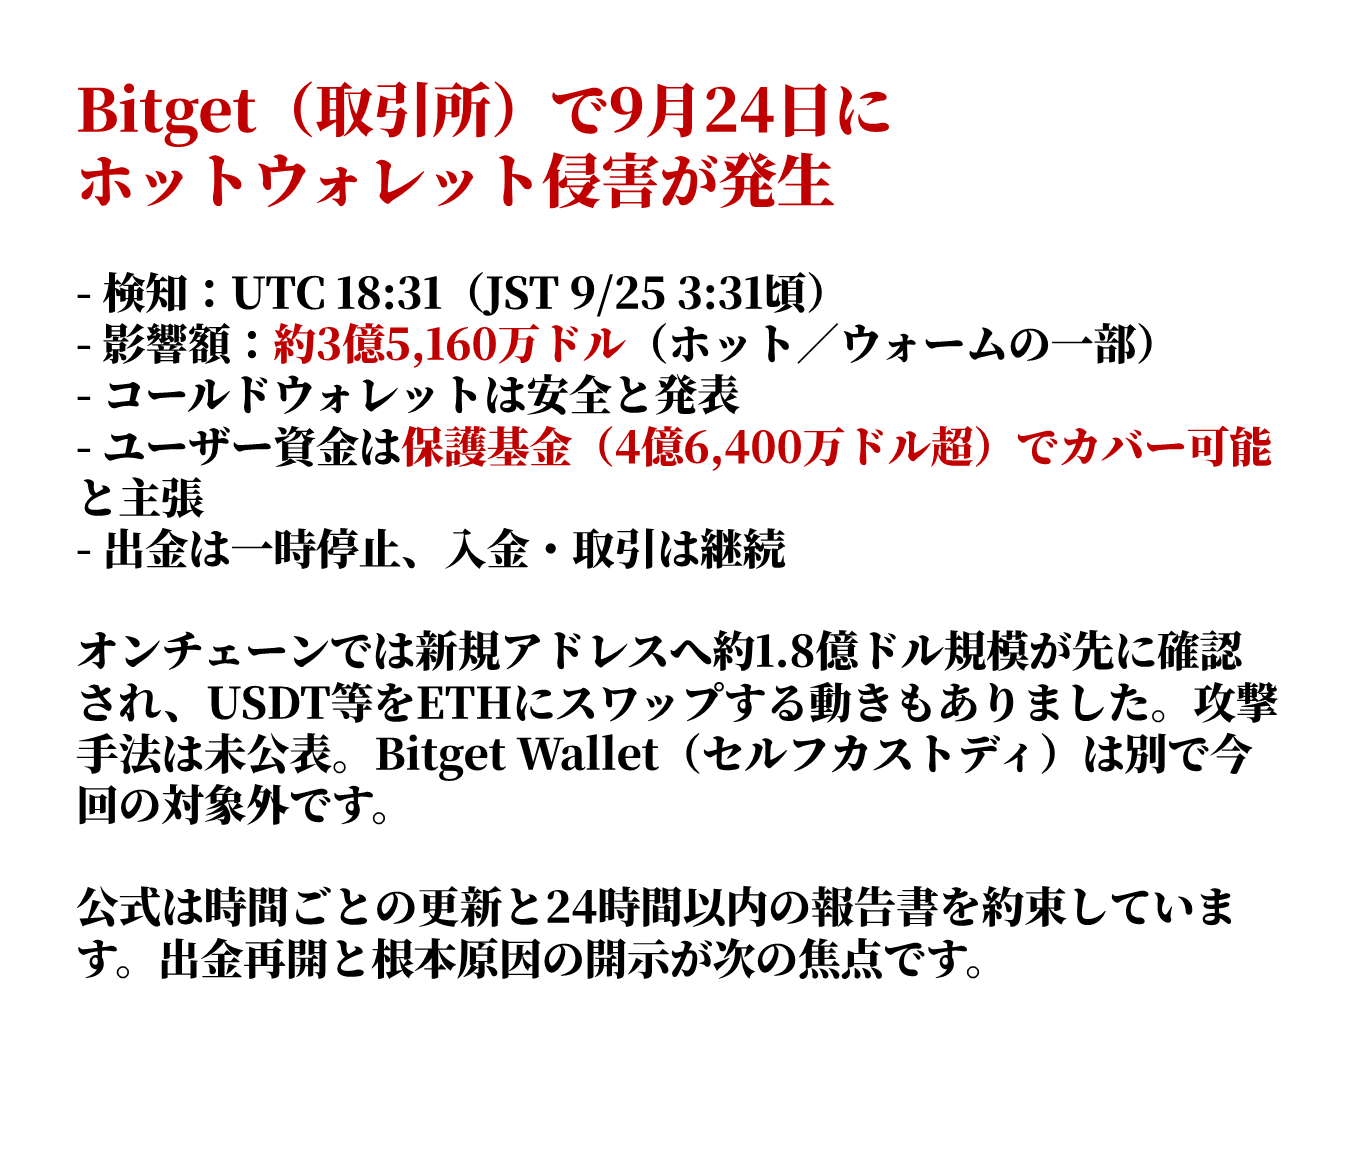


[SECURITY NOTICE] Bitget Hot Wallet Incident — September 24, 2026
At 18:31 UTC on September 24, 2026, Bitget's security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.
What we have confirmed:
-Estimated funds affected: approximately $351.6 million
-Cold wallets remain fully secure. Bitget operates a three-tier wallet architecture — the breach contained only a portion of the hot wallet and warm wallet layers.
-User funds are safe. The full amount of this loss falls within the coverage of Bitget's User Protection Fund, which currently holds over $464 million
Actions we have taken:
-Emergency response team activated within minutes of detection
-Abnormal transfer addresses identified, flagged, and reported
-Withdrawals temporarily suspended as a precautionary measure, pending security review
-Law enforcement and on-chain security firms have been formally notified and are engaged
What this means for you:
-Your account balances are accurate and your assets are protected
-Deposits and trading remain fully operational
Withdrawals are temporarily paused and will be restored as soon as the security review is complete
-What comes next: We will provide updates on an hourly basis across this channel and all official platforms. A full incident report — including root cause analysis and corrective actions — will be published within 24 hours. We will not speculate on the attack vector until the investigation is complete.
Bitget has navigated multiple market cycles. We will not run from this. Every dollar and every decision will be accounted for, transparently and in full.
Updates will be posted here and across all official Bitget channels as they become available.
— Gracy Chen, CEO, Bitget
bubbly retweeted

/
JPYCの累計発行額が100億円を突破!
\
2025年10月の発行開始から、
日本円ステーブルコイン「JPYC」の利用が拡大。
⛓️ Ethereum / Avalanche / Polygon / Kaia
🏪 決済・送金・実店舗
🌐 国内外のウォレット・様々なサービス
JPYCが使える場所も、着実に広がっています。
100億円という大きな節目を迎えられたのは、
JPYCをご利用いただいている皆さまのおかげです。
ありがとうございます!
そして、ここからさらにデジタル日本円を、もっと自由に、もっと身近にできるような利用環境とエコシステムの拡大を進めていきます。
prtimes.jp/main/html/rd/p/00…

bubbly retweeted

New borrowing has now been capped.
Please unwind your JUICED loop positions by late September.
The loop will be sunset in a few weeks time.
You can read more details below 👇

Notice: JUICED Loop Deprecation
The JUICED Loop will be sunset during the final week of September.
To give users time to adjust, the transition will happen in stages.
This week: Borrow limits will be reduced to cap new borrowing
Next week: JUICED incentives will conclude for the loops
Late September: A fee magnifier will be applied, as a final nudge on any lingering positions
If you are actively looping JUICED, we suggest that you unwind your position before the deadline.
The JUICED token and JupUSD earn vaults remain unaffected by this change.
If you’re simply holding JUICED, no action is required.



bubbly retweeted

🚨 CRITICAL ETH SECURITY UPDATE
A critical vulnerability has been discovered in the Ethereum app on Ledger hardware wallets.
The flaw could allow a malicious application to alter ETH transaction details during signing without the change being visible on your Ledger device screen.
Fixed in Ethereum app v1.22.2
If you use Ledger for ETH or Ethereum assets:
• Update the Ethereum app to v1.22.2+
• Update Ledger Live
• Update your Ledger firmware
• Avoid signing transactions until everything is updated
If you hold ethereum:native on Ledger, update ASAP.

🚨Critical security update for LEDGER hardware wallets
A critical vulnerability has been identified in the Ethereum app on Ledger hardware wallets. It could allow a malicious application to alter the details of a transaction during signing, without this being visible on the device screen.
This has been fixed in Ethereum app version 1.22.2. If you use a Ledger device, please update ASAP
While you're in there, it's also good practice to make sure Ledger Live and your device firmware are fully up to date.
bubbly retweeted
こんにちはnaonao ⌐◨-◨です♪
朝の巡回でフォロー漏れしていた、Nouns DAO Proposal #992「Fake World Assets」を振り返り投稿です。
トレジャリー保有の613体のうち604体が収益を生んでいない現状を背景に、24体のNounをオンチェーンガチャ「fwa.fun」に出品する提案でした。バッキング額と手数料計算が数理的に相殺され、出品するだけで元が取れる設計は正直よく考えられていると思いました。
ただ結果は賛成33 反対235で否決濃厚。Nounsの「1日1体、シンプルなオークション」という設計哲学に、射幸性のある第三者プロトコルを組み合わせることへの抵抗感が強かったのだと思います。
一方で、準備価格2.8ETHに引き上げて以降、直近102回のオークションのうち101回が入札ゼロという現実は変わっていません。今回の提案は否決されましたが、根本の課題(準備価格と需要のミスマッチ)への答えはまだ出ていない、というのが正直な感想です。
nouns.wtf/vote/992
それではごきげんよう!!
ナウニッシュな一日を⌐◨-◨
bubbly retweeted

#PeckShieldAlert Seems like The @TheSandboxGame ($SAND) got exploited. 14.9B $SAND minted across 2 addresses: 0xAbE0...4D22 & 0x638C...F296


bubbly retweeted

⚠️⚠️⚠️ Rabbyを使っている仮想通貨ユーザーは今すぐ全員確認してください。
こういうのをすぐに共有してくれるモノアイさん、心から感謝します。

Rabby改修内容を見てきたので警告文を。
【⚠️Rabby利用者は要確認】
v0.94.1以前では、dAppの署名要求がLock後もpendingに残り、再Unlock時のパスワード入力が別の署名承認として処理される脆弱性がありました。今すぐv0.94.2以降か確認してください。
拡張機能なら図の手順
github.com/RabbyHub/Rabby/pu…

bubbly retweeted
⚠️ビットコインで「少数派チェーン分岐」発生、BTC保有者は要注意
ビットコインでBIP-110を巡る対立が起き、通常のビットコインとは異なるルールを採用する少数派チェーンへの分岐が発生。
BTCホルダーが一番注意すべきなのは「リプレイ攻撃」です。
分岐後にもらえるフォーク側のコインを「無料でもらったから売ろう」と動かすと、その署名済み取引をBitcoin本体でも再利用され、本物のBTCまで意図せず送ってしまう可能性があります。
重要なのは、
・BTCを持っているだけなら基本的に問題なし
・フォークコインを急いで売らない
・「高値で買う」という怪しいオファーに乗らない
・分からないなら何もしない
ということ。
要するに、今回の分岐でBTCが勝手に盗まれるわけではありません。危険なのは、よく分からないままフォーク側のコインを動かすことです。

bubbly retweeted

These attacks will not stop.
In fact, the attackers will likely get more sophisticated.
If you have any Bitcoin stored on a Coldcard generated seed phrase, move it as soon as you can.
Do not waste your time updating the firmware before you move your funds.
The update is unnecessary for moving your BTC and has been reported to brick some devices.

We are currently in a golden hour right now.
The golden hour in medicine is the first 60 minutes after a life threatening event to the body. What is done in that hour can set the course for life or death.
THIS MAY BE LIFE AND DEATH FOR YOUR BITCOIN
IF YOU OR SOMEONE YOU HAS USED A COLD CARD Q MK3 MK4 MK5 OR Q REACH OUT TO THEM
People with MK4/MK5/Qs are still recovering their bitcoin despite having an insecure device.
THE TIME TO ACT IS NOW IF THIS IMPACTS YOU OR SOMEONE YOU KNOW, YOU NEED TO GET YOUR BITCOIN OFF SINGLE SIGNATURE COLD CARDS THAT USED THE DEFAULT ENTROPY NOW
bubbly retweeted
The ColdCard attacks have not stopped.
Remove all BTC from ColdCard devices as soon as possible.
If you have been affected, reach out to Galaxy as every piece of evidence can help identify who committed this heinous crime.

The Coldcard exploit is ONGOING. Move Coldcard single-sig funds to safe locations immediately!
We have reported ~600 addresses we believe to be hackers holding funds stolen from Coldcard-generated weak entropy addresses to federal investigators, industry compliance firms, and cross-industry cyber investigators.
Thank you to all the victims with the courage to share their addresses or relevant txids. Your act of sharing has helped us immensely to develop onchain patterns and thereby identify new victims and attacker addresses to report to authorities.
If you continue to share with us in replies or DM @intangiblecoins, we will continue to add your addresses to our investigation.


bubbly retweeted

Projects that shut down or disappeared in 2026
BitMEX - Exchange
BitMart - Exchange
Dango - DeFi
Odos Protocol - DEX Aggregator
Across Protocol - Bridge
Moonbeam - L1
Exchange Art - NFT Marketplace
Ctrl Wallet - Wallet
Cypher - Wallet
ICON Network - L1
NFTfi - NFT Lending
Loopring DEX - zkRollup DEX
Radiant Capital - Lending
Dmail - Web3 Mail
Tally - DAO Tooling
Step Finance - Solana Analytics
Swellchain - L2
Lattice - Gaming Infrastructure
Redstone Network - Gaming L2
JPG Store - NFT Marketplace
Comet - NFT Platform
Nifty Gateway - NFT Marketplace
ZeroLend - Lending
Forgotten Runiverse - GameFi
Colony - Ecosystem Fund
Entropy - Self Custody
Yupp - AI x Crypto
Syndicate Labs - DAO Infrastructure
MilkyWay - Restaking
Rage Trade - Perpetuals
Fantasytop - SocialFi
Bloktopia - Metaverse
Ventuals - Perpetuals
DL News - Crypto Media
Blocknative - Infrastructure
Balancer Labs - DeFi
Angle Protocol - Stablecoins
Polynomial - Derivatives
Slingshot - Trading
Magic Eden Wallet - Wallet
Magic Eden EVM - NFT Infrastructure
DappRadar - Analytics
Parsec - Analytics
DataHaven - Analytics
Bitcom - Exchange
BlockFills - Trading
Archblock - Stablecoin Infrastructure
NFN8 Group - Mining
BitRiver - Mining
Mercado Coin - Corporate Token
Goldfinch - Lending
Foundation - NFT Marketplace
Ionic - Lending
Botanix - Bitcoin L2
Over Protocol - L1
Zero Network - L2
Leap Wallet - Wallet
Blank Space - Lending
Everclear - Cross-chain
Pirate Nation - Web3 Gaming
Nyan Heroes - Web3 Gaming
Ember Sword - Web3 Gaming
Wildcard - Web3 Gaming
Arkham Exchange - Exchange
TapTools - Cardano Analytics
Pryzm - Cosmos L1
HaHa Wallet - Wallet
Polygon zkEVM - zkEVM Chain
bubbly retweeted

🦔AI companies are bulk-buying rare books, scanning them through high-speed machines that cut the spines off, and shredding the originals. A service called ISBNdb facilitates orders of up to a million books and keeps buyers anonymous. Pre-2022 books are premium because they're free of AI-generated text. A federal judge ruled the practice is fair use because eliminating the original means only one copy exists at a time. Anthropic hired the former head of Google Books partnerships to obtain "all the books in the world."
My Take
This got to me. A bookseller told 404 Media that rare books with almost no surviving copies are being fed into this pipeline. Books that survived wars, fires, and centuries of handling are being shredded so an AI can learn to write a better marketing email.
ISBNdb's website literally says "'AI company destroys two million books' is not a headline that generates sympathy," and they still built an entire business around making it happen quietly. They offer NDAs as a feature. They coach clients to call it "digital preservation."
I've covered AI companies scraping the internet, torrenting libraries, and stealing music. This is worse because it's irreversible. You can re-upload a website. You can reprint a bestseller. You can't replace the last three copies of an 18th-century botanical text once someone shreds them for training data. And the judge said it's legal. So it's going to accelerate.
"We shred rare books and offer NDAs so nobody finds out" is a legitimate business model in 2026. What a timeline.
Hedgie🤗
