

Windows Offensive Security Enthusiast 🤠 Blog: https://xitter.cf/t.co/CAwdjs2rKS GitHub: https://xitter.cf/t.co/YG2YOxfosm
Amsterdam, The Netherlands
Joined March 2016
- Tweets240
- Following107
- Followers1.7K
- Likes266




Arris Huijgen retweeted
Malware authors often hide their tracks using COM, but our latest guide provides the roadmap you need to decode those cryptic vtable calls and finally see exactly what’s happening under the hood: cs.co/6014BDgbFs

Arris Huijgen retweeted

Wrote a new blog about caveats with tools detecting(or mis detecting) relay exploit primitives against http(ESC8) and MSSQL endpoints. Kept noticing issues in tools reporting the absence or presence of vulns that I thought others may have noticed too abdulmhsblog.com/posts/pitfa…
I just added @ExploitDB as additional source of exploits to #WESNG's collector making "Windows Exploit Suggester - Next Generation" even more comprehensive for identifying unpatched vulnerabilities and exploiting those. Happy hacking! 😎
github.com/bitsadmin/wesng

Arris Huijgen retweeted

Small updated to DRSAT just pushed that will also allow Group Policy Editor and Certificate Authority / Templates MMC snap-ins work over a TCP only SOCKS connection.
github.com/CCob/DRSAT

Many more examples are in the CHEATSHEET at github.com/bitsadmin/nopower… or use the Get-Help/man command followed by the cmdlet, e.g. man iwr.
Regularly new cmdlets are added in NoPowerShell's DEV branch so keep an eye there to get the latest and greatest! 🔥
github.com/bitsadmin/nopower…

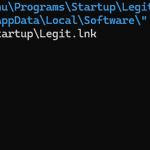
📡 To accomplish persistence, creating a shortcut in the Startup folder using the (unofficial) New-Shortcut cmdlet.

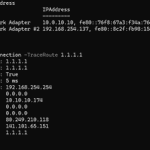
🛜 Checking IP configuration and testing routing using Get-NetIPAddress and Test-NetConnection.
🔐 Checking TLS certificate chain details using Invoke-WebRequest.


💻 User/session reconnaissance, on both the local as well as remote machines using the Get-LocalUser and Get-WinStation (unofficial) cmdlet.
📄 Hunting for authentication details of a specific user in the DC Security event log using Get-WinEvent.


Because the last release of #NoPowerShell was 2 years ago and to celebrate the repo has 999 stars, I just merged DEV ➡️ MASTER and published Release 1.50 containing over 60 offensive cmdlets! 🥳
github.com/bitsadmin/nopower…
See examples of some of the cmdlets below 👇

Interesting! Back in 2020 I wrote a blog on how to remotely over WMI create a shadow copy of SAM or NTDS.dit and use the @GMT syntax to download it over SMB. See details here: blog.bitsadmin.com/extractin…

Arris Huijgen retweeted

🚀 We just released my research on BadSuccessor - a new unpatched Active Directory privilege escalation vulnerability
It allows compromising any user in AD, it works with the default config, and.. Microsoft currently won't fix it 🤷♂️
Read Here - akamai.com/blog/security-res…

Arris Huijgen retweeted

What if you skipped VirtualAlloc, skipped WriteProcessMemory and still got code execution?
We explored process injection using nothing but thread context.
Full write-up + PoCs:
blog.fndsec.net/2025/05/16/t…

Arris Huijgen retweeted

Blogpost from my colleague about what’s still possible with recently published COM/DCOM toolings, Cross Session Activation and Kerberos relaying 🔥
r-tec.net/r-tec-blog-windows…

Arris Huijgen retweeted

ProxyBlob is alive ! We’ve open-sourced our stealthy reverse SOCKS proxy over Azure Blob Storage that can help you operate in restricted environments 🔒
🌐 github.com/quarkslab/proxybl…
Blog post for more details right below ⬇️


Look at those cute little blobs in your internal network. They look harmless, but how about the one carrying SOCKS? It's ProxyBlob, a reverse proxy over Azure.
Check out @_atsika's article on how it came to exist after an assumed breach mission ⤵️
👉 blog.quarkslab.com/proxyblob…

ALT Proxybloby is the red teamer's mascot. Be careful, if left alone in you network it will byte your SOCKS
Cool, novel, lateral movement technique by @william_knows by dropping a .dll file on a remote host obtaining code execution! 💡


Arris Huijgen retweeted

I just published a blog post where I try to explain and demystify Kerberos relay attacks. I hope it’s a good and comprehensive starting point for anyone looking to learn more about this topic. ➡️decoder.cloud/2025/04/24/fro…

Arris Huijgen retweeted

The S is for Security. How to use WinRMS as a solid NTLM relay target, and why it’s less secure than WinRM over HTTP. By @Defte_
Writeup: sensepost.com/blog/2025/is-t…
PR to impacket:
github.com/fortra/impacket/p…
Demo: youtu.be/3mG2Ouu3Umk