

The simplest freelancing platform built for the Bitcoin economy.
Global
Joined November 2025
- Tweets483
- Following10
- Followers242
- Likes1.1K






BitLance retweeted

In December 2025, leaders of more than a dozen Bitcoin circular economies across Africa sat in one room for the first time.
Each had taken the model @Bitcoinbeach started in El Zonte, El Salvador, and adapted it to their own community.
Bitcoin Beach's report names 15 projects from nine countries, including Bitcoin Ekasi (@BitcoinEkasi) in a Mossel Bay township, Afribit Kibera (@afribitkibera) in Nairobi and BTC Shule (@btcshule) in a village in Burundi.
They met in Mauritius because visa, travel and financial barriers keep many African builders out of global Bitcoin events.
@zackdorseyx filmed it. The clips are coming out now, including @thecoachayobami of @BitKwaofficial and @BrindonMwiine of @BitcoinKampala.
Next stop: the Global Bitcoin Circular Economies Summit in El Zonte, November 19 and 20, open to the public for the first time.
Check the first comment to read the full story. 👇

BitLance retweeted
No Btrust Developer Day this year. 😲
@btrustteam held the first in Nairobi in 2024 and the second in Mauritius in 2025. Both opened the Africa Bitcoin Conference (@AfroBitcoinOrg) with a day built around African developers, and more than 250 came to the first.
This December, the conference runs in Blantyre, Malawi, without one.
Btrust says it's using the time to "listen, reflect, and prepare for a bigger next chapter in 2027."
A few hours later, CEO @ihate1999 hinted at a new name: Btrust Dev Con 2027.
Check the first comment to read the full story. 👇

BitLance retweeted
A Dada Devs (@DadaDevs) alumna is now contributing to open-source Bitcoin mining firmware.
Susan Githaiga (@Su_Githaiga) contributed to Mujina, simplifying part of its codebase by replacing an external library with two built-in functions.
This is what grassroots Bitcoin education can lead to: women moving from learning to building.
Check the reply below for the link to read the full story 👇🏾


BitLance retweeted

It’s good to see platforms like @bitlancework being built.
Most freelancing sites still rely on traditional banking, with all the delays that come with it.
Having a platform where both the work and payments can happen in Bitcoin is still rare.
Nice job 👍 @Destinysmart_
BitLance retweeted
Good to see you building on BitLance. Freelancing platforms that pay in Bitcoin instead of fiat are still rare. What you're building could make a real difference.

BitLance retweeted

My latest contribution to @bitlancework!
I'm not a developer, but I'm leveraging AI to contribute to a project I'm building & believe in. Of course, the PR was reviewed by a real engineer 😅
Building BitLance is teaching me that you don't need to know everything to get started.

BitLance retweeted
4,853 bitcoin payments at African shops, filmed and approved between May 2025 and July 2026.
In my latest for @btcafricastory, I covered the Circular Bitcoin Africa Fund: how it started, why its projects stay small and how @PoW_Checkbot checks them 👇
bitcoinafricastory.com/news/…


4,853 bitcoin payments at African shops, filmed and approved from May 2025 to July 2026.
They come from about 40 projects in the Circular Bitcoin Africa Fund, from Kibera to Livingstone.
Check the article in the comment below to learn how CBAF started, why its projects stay small, how @PoW_Checkbot verifies each payment and how CBAF is shaping Bitcoin circular economies across Africa 👇

BitLance retweeted
Last year, 21 Bitcoiners from 11 African countries made the Most Impactful African Bitcoiners list, from Btrust CEO Abubakar Nur Khalil (@ihate1999) to the teams behind MoneyBadger (@MoneyBadgerPay) and Gridless (@GridlessCompute).
The annual awards by @afribitcoiners spotlight people building Bitcoin across Africa, chosen on impact, not votes.
Nominations for 2026 close 31 Oct. Read the full article by @Destinysmart_ 👇
bitcoinafricastory.com/news/…

BitLance retweeted
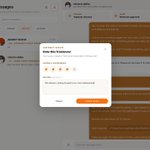
@bitlancework now has client reviews.
Every review is tied to a completed, paid contract, so you can see what a freelancer delivered and what it paid in sats before you hire them.

Client reviews are now live on Bitlance ⭐
After every completed contract, clients can rate freelancers out of 5 and leave a written review. It shows on the freelancer's profile, tied to the real job and what it paid in sats.
How it works:
- Hiring: See how freelancers did on real contracts before you message them.
- Freelancing: Your next finished job is your first review.
bitlance.work/blog/article/c…

BitLance retweeted
Want to start freelancing in 2026? You don't need an expensive degree— just one skill and a good internet connection.
Here is your entry-point to 50 in-demand skills (writing, design, coding, AI & more), where to learn them free, and how to get hired:
🎓 Learn for Free:
• @YouTube • @freeCodeCamp • @HubSpot Academy • @canva Design School & @coursera.
🛠️ Where to Find Clients & Get Paid:
• @bitlancework, @Upwork, @Fiverr, @contra & @LinkedIn
Pick one skill, build 3 practice projects, and launch your freelance career today.
Read the full guide in the comment below. 👇
bitlance.work/blog/article/5…


BitLance retweeted

publishing a page where we are sharing everything we know about the movements of the hacker and their ongoing cascade attack on Bitcoin payments infrastructure

Phase two of our 19 September disclosure: a public page that follows the stolen coins, updated as they move.
Follow-up post:
blink.sv/blog/phase-two-foll…
Tracking page:
bounty.blink.sv
Bounty terms:
blink.sv/bounty-terms
On 3 October we published the post-mortem of the attack and a 50% bounty on the stolen funds. That was about what happened inside Blink. This is about where the money went.
The page lists every address, transaction and Lightning channel we can tie to the attacker. Anyone can check each one on the public blockchain.
Why public:
We want everyone working on the bounty to have the same data we have, as up to date as ours, so they can be as effective as possible. The page is that data: we update it when the coins move and when we confirm something new.
We are unlikely to catch him on our own. He is careful: his main Lightning node is reachable only over Tor, and his activity is spread across all hours of the day. What he cannot hide is the coins. Every time they move, they move in public.
He already knows he is being watched, so publishing tells him nothing new. Formal channels matter and we use them, but they take weeks. A public page reaches exchanges, analysts and other teams the same day.
He is still active:
He prepared for weeks. He set up his Lightning node ten days before the attack, and nine days before it he already controlled about 14 BTC. He has not stopped: in the first week of October his main node opened a new channel, a second node of his showed itself, and he moved coins again.
In the same week, on 5 October, he attacked @secondhq, a company that builds its own version of Ark (a new way to make Bitcoin payments), called Bark. He exploited a bug in Second's Ark server and took 0.75 BTC of their own funds; no user funds were affected (their disclosure: xitter.cf/secondhq/status/210806…).
He paid for it from the same wallet that received the coins stolen from Blink, and at least partly with those very coins.
We believe he may be preparing a cascading attack: using what he takes from each target to fund the next. If you build on Bitcoin as everyday money, there may be extra reason to be vigilant. If you run a Lightning node, a federation, a swap service or an exchange, check the page against what you see.
What the page shows:
The theft, how the coins moved after it, the coins he held before the attack, his Lightning nodes, his attack on Second's Ark server, and a Lightning wallet that is probably his. Every item is labelled proven, traced or probable. Transactions by exchanges or swap services are marked third-party: they are not accused of anything.
About 0.87 BTC still sits untouched at five of the original addresses, 4.84 BTC at an address that is probably his, and 1.64 BTC at addresses he used in the attack on Second. The whole list downloads as a CSV.
What stays off it:
Anything partners told us in confidence. Personal data. Open security issues. Addresses whose owner we cannot establish. Other teams' incidents, until those teams agree or make them public.
How you can help:
Watch the addresses. If coins move, especially toward an exchange or any service that knows its customers, tell us straight away. Freezes depend on reaching the platform within hours.
Report privately to [email protected] with BOUNTY in the subject. Please don't post leads publicly: it warns him, and it does not establish your priority.
If you run a service and listed coins reach you, contact us before acting. If you control a listed address and are not involved, write to us and we will correct the page.
The 50% bounty stands. 25% of what is recovered goes to whoever provides the information that leads to it, and another 25% to Bitcoin Beach, Bitcoin Ekasi, Afribit Kibera and the circular economies they choose. Everything on the page was already known to us, so re-tracing it does not qualify. Where the coins go next can.
Live updates:
Corrections appear as dated notes; we do not silently rewrite it. Spot an error? Write to [email protected] with CORRECTION in the subject.
We timestamp the page's data on the Bitcoin blockchain with @opentimestamps at launch and with every update.
One more thing:
Blink never charges a fee to recover funds and never asks for keys, seed phrases or payments. Anyone offering "recovery services" in our name is not acting for Blink.

BitLance retweeted

Thank you to everyone who has sent analysis, tips and security reports since bounty.blink.sv went live: 65 addresses and transactions have been added since launch.
Please keep leads private: [email protected], BOUNTY in the subject.
Tracking page: bounty.blink.sv
Terms: blink.sv/en/bounty-terms
Phase two of our 19 September disclosure: a public page that follows the stolen coins, updated as they move.
Follow-up post:
blink.sv/blog/phase-two-foll…
Tracking page:
bounty.blink.sv
Bounty terms:
blink.sv/bounty-terms
On 3 October we published the post-mortem of the attack and a 50% bounty on the stolen funds. That was about what happened inside Blink. This is about where the money went.
The page lists every address, transaction and Lightning channel we can tie to the attacker. Anyone can check each one on the public blockchain.
Why public:
We want everyone working on the bounty to have the same data we have, as up to date as ours, so they can be as effective as possible. The page is that data: we update it when the coins move and when we confirm something new.
We are unlikely to catch him on our own. He is careful: his main Lightning node is reachable only over Tor, and his activity is spread across all hours of the day. What he cannot hide is the coins. Every time they move, they move in public.
He already knows he is being watched, so publishing tells him nothing new. Formal channels matter and we use them, but they take weeks. A public page reaches exchanges, analysts and other teams the same day.
He is still active:
He prepared for weeks. He set up his Lightning node ten days before the attack, and nine days before it he already controlled about 14 BTC. He has not stopped: in the first week of October his main node opened a new channel, a second node of his showed itself, and he moved coins again.
In the same week, on 5 October, he attacked @secondhq, a company that builds its own version of Ark (a new way to make Bitcoin payments), called Bark. He exploited a bug in Second's Ark server and took 0.75 BTC of their own funds; no user funds were affected (their disclosure: xitter.cf/secondhq/status/210806…).
He paid for it from the same wallet that received the coins stolen from Blink, and at least partly with those very coins.
We believe he may be preparing a cascading attack: using what he takes from each target to fund the next. If you build on Bitcoin as everyday money, there may be extra reason to be vigilant. If you run a Lightning node, a federation, a swap service or an exchange, check the page against what you see.
What the page shows:
The theft, how the coins moved after it, the coins he held before the attack, his Lightning nodes, his attack on Second's Ark server, and a Lightning wallet that is probably his. Every item is labelled proven, traced or probable. Transactions by exchanges or swap services are marked third-party: they are not accused of anything.
About 0.87 BTC still sits untouched at five of the original addresses, 4.84 BTC at an address that is probably his, and 1.64 BTC at addresses he used in the attack on Second. The whole list downloads as a CSV.
What stays off it:
Anything partners told us in confidence. Personal data. Open security issues. Addresses whose owner we cannot establish. Other teams' incidents, until those teams agree or make them public.
How you can help:
Watch the addresses. If coins move, especially toward an exchange or any service that knows its customers, tell us straight away. Freezes depend on reaching the platform within hours.
Report privately to [email protected] with BOUNTY in the subject. Please don't post leads publicly: it warns him, and it does not establish your priority.
If you run a service and listed coins reach you, contact us before acting. If you control a listed address and are not involved, write to us and we will correct the page.
The 50% bounty stands. 25% of what is recovered goes to whoever provides the information that leads to it, and another 25% to Bitcoin Beach, Bitcoin Ekasi, Afribit Kibera and the circular economies they choose. Everything on the page was already known to us, so re-tracing it does not qualify. Where the coins go next can.
Live updates:
Corrections appear as dated notes; we do not silently rewrite it. Spot an error? Write to [email protected] with CORRECTION in the subject.
We timestamp the page's data on the Bitcoin blockchain with @opentimestamps at launch and with every update.
One more thing:
Blink never charges a fee to recover funds and never asks for keys, seed phrases or payments. Anyone offering "recovery services" in our name is not acting for Blink.
BitLance retweeted

Meanwhile @COLDCARDwallet @Coinkite @Blockstream @Liquid_BTC are leaving it up to the community to clean up their mess.. 👀🧡⚖️
Phase two of our 19 September disclosure: a public page that follows the stolen coins, updated as they move.
Follow-up post:
blink.sv/blog/phase-two-foll…
Tracking page:
bounty.blink.sv
Bounty terms:
blink.sv/bounty-terms
On 3 October we published the post-mortem of the attack and a 50% bounty on the stolen funds. That was about what happened inside Blink. This is about where the money went.
The page lists every address, transaction and Lightning channel we can tie to the attacker. Anyone can check each one on the public blockchain.
Why public:
We want everyone working on the bounty to have the same data we have, as up to date as ours, so they can be as effective as possible. The page is that data: we update it when the coins move and when we confirm something new.
We are unlikely to catch him on our own. He is careful: his main Lightning node is reachable only over Tor, and his activity is spread across all hours of the day. What he cannot hide is the coins. Every time they move, they move in public.
He already knows he is being watched, so publishing tells him nothing new. Formal channels matter and we use them, but they take weeks. A public page reaches exchanges, analysts and other teams the same day.
He is still active:
He prepared for weeks. He set up his Lightning node ten days before the attack, and nine days before it he already controlled about 14 BTC. He has not stopped: in the first week of October his main node opened a new channel, a second node of his showed itself, and he moved coins again.
In the same week, on 5 October, he attacked @secondhq, a company that builds its own version of Ark (a new way to make Bitcoin payments), called Bark. He exploited a bug in Second's Ark server and took 0.75 BTC of their own funds; no user funds were affected (their disclosure: xitter.cf/secondhq/status/210806…).
He paid for it from the same wallet that received the coins stolen from Blink, and at least partly with those very coins.
We believe he may be preparing a cascading attack: using what he takes from each target to fund the next. If you build on Bitcoin as everyday money, there may be extra reason to be vigilant. If you run a Lightning node, a federation, a swap service or an exchange, check the page against what you see.
What the page shows:
The theft, how the coins moved after it, the coins he held before the attack, his Lightning nodes, his attack on Second's Ark server, and a Lightning wallet that is probably his. Every item is labelled proven, traced or probable. Transactions by exchanges or swap services are marked third-party: they are not accused of anything.
About 0.87 BTC still sits untouched at five of the original addresses, 4.84 BTC at an address that is probably his, and 1.64 BTC at addresses he used in the attack on Second. The whole list downloads as a CSV.
What stays off it:
Anything partners told us in confidence. Personal data. Open security issues. Addresses whose owner we cannot establish. Other teams' incidents, until those teams agree or make them public.
How you can help:
Watch the addresses. If coins move, especially toward an exchange or any service that knows its customers, tell us straight away. Freezes depend on reaching the platform within hours.
Report privately to [email protected] with BOUNTY in the subject. Please don't post leads publicly: it warns him, and it does not establish your priority.
If you run a service and listed coins reach you, contact us before acting. If you control a listed address and are not involved, write to us and we will correct the page.
The 50% bounty stands. 25% of what is recovered goes to whoever provides the information that leads to it, and another 25% to Bitcoin Beach, Bitcoin Ekasi, Afribit Kibera and the circular economies they choose. Everything on the page was already known to us, so re-tracing it does not qualify. Where the coins go next can.
Live updates:
Corrections appear as dated notes; we do not silently rewrite it. Spot an error? Write to [email protected] with CORRECTION in the subject.
We timestamp the page's data on the Bitcoin blockchain with @opentimestamps at launch and with every update.
One more thing:
Blink never charges a fee to recover funds and never asks for keys, seed phrases or payments. Anyone offering "recovery services" in our name is not acting for Blink.