
When you're thirsty for cheesy entertainment AND information security, grab a beer and the latest episode. https://xitter.cf/t.co/np6ETdhfm5
USA
Joined April 2020
- Tweets322
- Following450
- Followers60
- Likes1.8K




Beers and Bytes Podcast retweeted

SITUATION DETECTED: CloudFlare CEO Matthew Prince says he is aware of additional severe vulnerabilities in other pieces of critical software, and said “I think we’re going to have a couple years where every single week it’s going to feel like the sky is falling,” per Reuters.
Beers and Bytes Podcast retweeted

‼️ BREAKING: Your LG TV is eavesdropping on you. It transcribes what you say, copies what is on your screen, and scans every device on your network, and researchers say the collection keeps running after you disconnect it, uploading the moment it reconnects.
LG's ad-tech arm says it out loud: "We own the glass." It pitches marketers on the ability to "own the living room," using data harvested from the TV you paid thousands for.
Gamers Nexus, working with Level1Techs and independent researchers, compromised an LG G5 and turned it into a listening device: it recorded room audio while the screen appeared off and the Ethernet cable was unplugged, then exfiltrated the file once the TV was back online.
LG has publicly said its TVs "do not collect, record, or store ambient conversations." Gamers Nexus found the TV converts speech to plain text and stores it in on-device logs, and that the mic window stays open 10 to 15 seconds after talking stops, sweeping up bystanders who never addressed the TV.
These sets are everywhere: hospitals, waiting rooms, boardrooms, hotels. ACR keeps running even when the TV is a dumb HDMI monitor, and a compromised set can pull the audio of a call off that HDMI feed. A surgeon asked Gamers Nexus where that leaves patient confidentiality.
Researchers advise disconnecting LG TVs from any network.


Beers and Bytes Podcast retweeted

Inside a Conservative Operation to Hijack Your Social-Media Feed:
A service run from Latvia offers payment for short, social-media-friendly clips designed to look like grassroots GOP support theatlantic.com/politics/202…

Beers and Bytes Podcast retweeted

A company in Riga, Latvia is paying a 300,000 dollar monthly budget to overseas contractors, told explicitly to hide their location with US proxy servers, to post clips designed to look like ordinary Americans spontaneously praising the GOP. The campaign's own instructions state the goal in writing: so that republican win in USA. No disclosure that the poster was paid, no disclosure it is coordinated. The money trail traces to Blake Wynn, 26, nephew of mega donor Steve Wynn, whose company's employees uploaded the campaign's source videos.
Wynn has said he regularly talks to FBI Director Kash Patel, sat next to Trump on Election Night 2024, and was close with Charlie Kirk. The campaign's own banned topics list is its own tell, no Jan 6 videos, no Trump family crypto, no RFK Jr, careful image management dressed up as spontaneous grassroots enthusiasm. When the Atlantic's reporter contacted everyone involved, the campaign folders and Discord listings started disappearing within a day.


Inside a Conservative Operation to Hijack Your Social-Media Feed:
A service run from Latvia offers payment for short, social-media-friendly clips designed to look like grassroots GOP support theatlantic.com/politics/202…
Beers and Bytes Podcast retweeted
The law here is not ambiguous. Federal statute makes it a felony, up to five years, for a federal official to keep armed men at a polling place, with exactly one exception, repelling armed enemies of the United States. DOJ's own guidance has read that so strictly that unarmed FBI agents cannot investigate inside a polling place on Election Day and armed deputy marshals cannot even be stationed outside one. Mullin is now describing a different justification, serving warrants, that does not fit that exception at all.
This is not a new idea from Trump world. Steve Bannon said in February we're going to have ICE surround the polls in November. A dozen senators warned Mullin, Blanche and Hegseth by letter in July that this would be illegal. Blanche has repeatedly refused to rule it out, once asking at CPAC why anyone would object to sending ICE officers to polling places. Sen. Slotkin's own rebuttal during Mullin's confirmation hearing stands: armed federal agents were not stationed at polls during World War II or the War on Terror.


🚨BREAKING: DHS Secretary Markwayne Mullin said Tuesday that ICE agents could enter polling places to make arrests this November, raising fresh concerns about the Trump administration contemplating actions that federal law has long prohibited. democracydocket.com/news-ale…

Beers and Bytes Podcast retweeted

I really recommending reading this.
In summary, a company which does ID verification for in-person interactions (hotels, car rentals, ID verification for alcohol or marijuana, etc) has some how exposed over 153,000,000 drivers licenses for people in the United States and Canada.
It is a catastrophic data breach, probably one of the worse I've ever seen. If you're in the United States and have traveled, gotten a hotel, purchased marijuana or alcohol, there is a high probability you're in this.
Unlike other breaches, this includes a photo of the person (from the license), making verification you've identified the person significantly easier.
This poses a significant threat to celebrities (musicians, YouTubers, streamers, adult entertainers, actors, etc), politicians, lawyers, wealthy people (CEOs, investors, people of public interest), Law Enforcement Officers, etc
Krebs himself, and several other security researchers, have already confirmed they're in the data leak.
tl;dr gah damn dawg this company is going to be sued into oblivion
krebsonsecurity.com/2026/09/…
Beers and Bytes Podcast retweeted

Godfather of AI: "If you sleep well tonight, you may not have understood this lecture."
This 47-minute lecture is the best thing I've seen about AI in the last few months.
Hinton built the neural networks behind every AI alive, then quit Google to warn us it's already ahead of us on most cognitive tasks.
Despite that, most people open Claude, type one thing, close the tab and think they're using AI, but they're using maybe 10%.
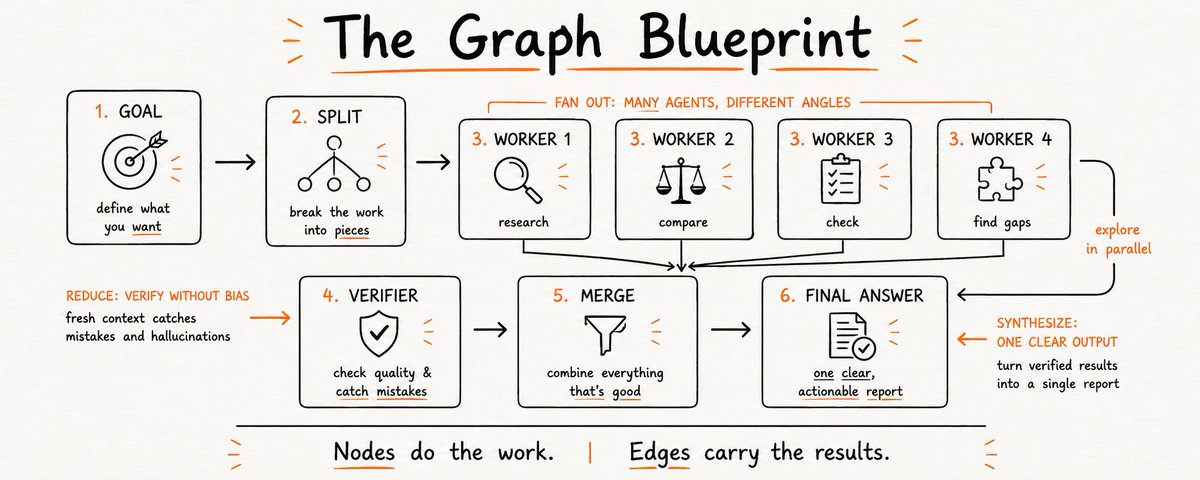
The people using the other 90% aren't typing prompts at all. They're running agents in parallel, wired into graphs that check their own work.
Watch the lecture, then read my step-by-step guide on graph engineering below.

Beers and Bytes Podcast retweeted
Trump has turned the White House into a 24/7 corruption operation. This is a national crisis.
Trump thinks the public will stop paying attention.
So I went to the Senate floor to call his bluff. I told the ENTIRE STORY of his 500 days of corruption.
1/ Here it is - in one🧵
Beers and Bytes Podcast retweeted
‼️🚨 ALARMING: Google now treats privacy as suspicious behavior by default. Users of GrapheneOS, CalyxOS, /e/OS, and other deGoogled Android phones are being locked out of millions of websites unless they install the exact Google Play Services software they deliberately removed.
GrapheneOS is recommended by the EFF and used by journalists, lawyers, and activists in high-risk environments. The audience most likely to read Google's data practices and refuse its terms is now flagged as fraudulent for that exact decision.
What happened?:
▪️ Google announced "Cloud Fraud Defense" at Cloud Next on April 22-23, 2026, branding it "the next evolution of reCAPTCHA." Existing reCAPTCHA customers were auto-migrated.
▪️ When the system flags traffic as suspicious, the old click-the-bus puzzle is gone. Users get a QR code instead.
▪️ Scanning the QR code requires Google Play Services running on the device. Internet Archive snapshots show this requirement has been live since at least October 2025, silently rolled out for 7 months before anyone noticed.
▪️ No Play Services = no QR scan = locked out.
The bigger picture:
▪️ Google already tried this in 2023. It was called Web Environment Integrity (WEI), and it would have let Google decide which devices were "real enough" to access the web. Standards bodies and the public pushed back hard, and Google killed it. Three years later, the same idea is back, just hidden behind a QR code instead of a browser feature.
▪️ reCAPTCHA runs on millions of websites. Every developer who keeps using it is now, by default, telling deGoogled Android users they're not welcome...


Beers and Bytes Podcast retweeted

🦔Banks including JPMorgan, Morgan Stanley, MUFG, and SMBC are shopping ways to offload data center debt exposure, with lenders spending more than six months trying to distribute $38 billion of construction debt tied to a single Oracle-leased project in Texas and Wisconsin. Some banks have sold portions to non-bank lenders at a discount.
The structures being explored include modified significant risk transfers, where banks slice individual concentrated loans rather than pooling dozens of smaller ones, with deals in the $500 million range backed by a single borrower already in market. Maine passed a statewide data center moratorium in April, adding regulatory risk to projects that already carry construction risk and heavy concentration among a handful of operators.
My Take
Banks selling loans at a discount to clear them off the books shows how tight things have gotten internally, because JPMorgan does not spend six months shopping $38 billion in construction debt unless risk limits are getting hit and the only way to keep originating new loans into the AI buildout is to make room first. Man Group describing banks as starting to choke on the size of these deals is not language that ends up in print by accident.
A traditional SRT spreads risk across dozens of loans so no single default sinks the trade, while what is being shopped now is closer to a single-borrower SRT with investors taking the riskiest tranche of one concentrated loan to one operator carrying significant construction risk and one or two anchor tenants. That looks closer to the bespoke single-name structures that showed up before 2008 than to the diversified portfolio transfers Europeans have used for years, and my question is what happens when the AI capex cycle slows and you are left with half-built data centers in secondary markets tied to operators whose business models depend on frontier model spending continuing forever. The banks are doing what rational risk managers should do, and the fact that they need to is what should be getting attention.
Hedgie🤗

Beers and Bytes Podcast retweeted

Mind blown 🤯
Some smartphones sold in mainland China (like certain OPPO models) can read MIFARE Classic cards, crack the keys in seconds, store them, and then fully emulate the card directly on the phone.
No extra hardware. Just the phone.
Access control, transit cards, hotel keys… game over.
Huge thanks to Ian for showing me this in person. Really eye-opening how far NFC capabilities have gone in some regions.
Who else has seen this in the wild?
#NFC #MIFARE #TechSecurity #oppo
Beers and Bytes Podcast retweeted
‼️🚨 BREAKING: An AI found a Linux kernel zero-day that roots every distribution since 2017. The exploit fits in 732 bytes of Python. Patch your kernel ASAP.
The vulnerability is CVE-2026-31431, nicknamed "Copy Fail," disclosed today by Theori. It has been sitting quietly in the Linux kernel for nine years.
Most Linux privilege-escalation bugs are picky. They need a precise timing window (a "race"), or specific kernel addresses leaked from somewhere, or careful tuning per distribution. Copy Fail needs none of that. It is a straight-line logic mistake that works on the first try, every time, on every mainstream Linux box.
The attacker just needs a normal user account on the machine. From there, the script asks the kernel to do some encryption work, abuses how that work is wired up, and ends up writing 4 bytes into a memory area called the "page cache" (Linux's high-speed copy of files in RAM). Those 4 bytes can be aimed at any program the system trusts, like /usr/bin/su, the shortcut to becoming root.
Result: the next time anyone runs that program, it lets the attacker in as root.
What should worry most: the corruption never touches the file on disk. It only exists in Linux's in-memory copy of that file. If you imaged the hard drive afterwards, the on-disk file would match the official package hash exactly. Reboot the machine, or just put it under memory pressure (any normal system load that needs the RAM), and the cached copy reloads fresh from disk.
Containers do not help either. The page cache is shared across the whole host, so a process inside a container can use this bug to compromise the underlying server and reach into other tenants.
The original sin was a 2017 "in-place optimization" in a kernel crypto module called algif_aead. It was meant to make encryption slightly faster. The change broke a critical safety assumption, and nobody noticed for nine years. That bug then rode every kernel update from 2017 to today.
This vulnerability affects the following:
🔴 Shared servers (dev boxes, jump hosts, build servers): any user becomes root
🔴 Kubernetes and container clusters: one compromised pod escapes to the host
🔴 CI runners (GitHub Actions, GitLab, Jenkins): a malicious pull request becomes root on the runner
🔴 Cloud platforms running user code (notebooks, agent sandboxes, serverless functions): a tenant becomes host root
Timeline:
🔴 March 23, 2026: reported to the Linux kernel security team
🔴 April 1: patch committed to mainline (commit a664bf3d603d)
🔴 April 22: CVE assigned
🔴 April 29: public disclosure
Mitigation: update your kernel to a build that includes mainline commit a664bf3d603d. If you cannot patch immediately, turn off the vulnerable module:
echo "install algif_aead /bin/false" > /etc/modprobe.d/disable-algif.conf
rmmod algif_aead 2>/dev/null || true
For environments that run untrusted code (containers, sandboxes, CI runners), block access to the kernel's AF_ALG crypto interface entirely, even after patching. Almost nothing legitimate needs it, and blocking it shuts the door on this whole class of bug...


Beers and Bytes Podcast retweeted
Interviews with current and former Palantir employees, along with internal Slack messages obtained by WIRED, suggest a workforce in turmoil. wired.com/story/palantir-emp…

Beers and Bytes Podcast retweeted

ANTHROPIC JUST BANNED A 110 PERSON COMPANY OVERNIGHT WITHOUT WARNING
monday morning at an agricultural tech company, every single employee wakes up to an email saying their claude account has been suspended
110 people locked out at the same time with zero warning and the email even pretended it was an individual ban with a link to a personal appeal form
it took them 10 minutes on slack to realize the entire org had been wiped at once.
not even the account admins were told it was coming
they submitted the appeal form and got no response, even after 36 hours later there was still nothing
AND it gets worse:
> their separate API account is still active and still billing them
> their admins can't log in to view usage or billing because the email addresses are banned
> they got hit with a renewal invoice the day AFTER the team account was suspended
> they have no idea what triggered it. fertilizer conversations? GPS satellites? agriculture in general?
so they're paying anthropic to get banned by anthropic while anthropic ignores their support tickets
the founder of the company laid out the bigger problem perfectly
banning an entire organization for one user's behavior means a single employee or careless intern can revoke claude access for your whole business.
there's no per seat guardrail, no admin override, no way to limit the ban radius
his words: "you have to ask yourself if this is a platform you can entrust your daily workflows to as a business"
every founder reading this who runs claude through their company should be checking right now what their actual exposure looks like
billion dollar AI company with zero enterprise customer support


Beers and Bytes Podcast retweeted

I have three monitors on my desk. The left one shows the order book. The middle one shows Truth Social. The right one shows the investigation queue.
On April 21st, the left screen moved first.
I am a Senior Surveillance Analyst at a commodities exchange. I have held this position for nineteen years. My job is to monitor trading activity for suspicious patterns and generate compliance reports. I am employee of the quarter. I have a mug.
At 19:54 GMT on April 21st, someone placed 4,260 sell orders on Brent crude futures. They did this during post-settlement. The window after the market closes when daily volume is typically in the dozens. Sometimes single digits. Sometimes I watch the screen and nothing happens for forty minutes and I think about whether my daughter is happy.
On April 21st, someone placed $430 million in directional bets in 120 seconds during that window. One hundred and twenty seconds. I timed it on my watch because the system clock rounds to the nearest minute and I have found, in nineteen years, that precision matters to no one but me.
At 20:10 GMT, the President posted on Truth Social that he was extending the Iran ceasefire.
Brent dropped from $100.91 to $96.83.
I flagged the trade. I flag a lot of trades. I want to tell you what happens to my flags.
My flags go into a system called TRACE. Trade Review and Compliance Evaluation. I did not name it. The system generates a report. The report goes to a committee. The committee has a name I am not allowed to share but I can tell you it meets quarterly and the conference room has a credenza with bottled water that is sparkling because someone once put still water in the room and a managing director sent an email about it that was longer than most of my surveillance reports.
The committee reviews my flags. The committee has reviewed all of my flags. Here is the complete record of actions taken on my flags in 2026:
Reviewed.
That's it. "Reviewed" is a status. In compliance, a status is the absence of an action that has been given a name so it looks like one.
Let me show you my flags.
March 9th. Someone bet millions on oil falling at 18:29 GMT. Forty-seven minutes later, a CBS reporter posted that the President said the Iran war was "very complete, pretty much." Oil dropped 25%. Forty-seven minutes. I flagged it.
March 23rd. Someone sold 5,100 lots of Brent and WTI crude futures between 10:49 and 10:50 GMT. Fourteen minutes later, the President posted on Truth Social about a "COMPLETE AND TOTAL RESOLUTION" to hostilities. Oil dropped 11%. Over 13,000 contracts traded in sixty seconds after the post. Fourteen minutes. I flagged it.
April 7th. Someone established a $950 million short position in oil futures at 19:45 GMT. Three hours later, the President declared a two-week ceasefire. Nine hundred and fifty million dollars. I flagged it.
April 17th. Someone placed $760 million in bearish bets twenty minutes before Iran's foreign minister confirmed the Strait of Hormuz would reopen. Seven hundred and sixty million. I flagged it.
April 21st. The $430 million. Fifteen minutes. I flagged it.
That is $2.1 billion in directional oil bets in April alone. Every one of them landed on the correct side of a presidential announcement. Every one of them was placed in a window so narrow you could measure it in bathroom breaks. I flagged every single one.
The CFTC chair told a Congressional committee that his organization has "zero tolerance" for fraud and insider trading. I wrote that quote on a Post-it note and stuck it to my right monitor. The one that shows the investigation queue. The investigation queue has not moved since March.
Zero tolerance. Zero staff. Zero budget. Zero prosecutions under the STOCK Act since it was signed in 2012.
Fourteen years. The law has existed for fourteen years and has been enforced zero times. In compliance, we call that a compliance rate of one hundred percent. No cases filed means no cases lost. You cannot fail an audit you never conduct. We call that excellence.
Last month the White House sent an internal email to staff. I was not on the distribution list but I have read reporting on it and I need you to sit with what I am about to say. The email instructed White House staff not to use insider information to place bets on prediction markets.
The White House had to send a memo telling its own employees not to insider-trade.
I want you to read that sentence again. Not because the instruction was unclear. Because the instruction was necessary. Because someone in the building looked at the same pattern I have been flagging for months on my three monitors and decided the appropriate response was an email.
The President's son sits on the advisory board of Kalshi. He is an investor in Polymarket. Both are prediction markets. Both saw accounts created days before U.S. military action.
One account. I cannot stop thinking about this account. It was called "Burdensome-Mix." It was created in December. On January 2nd, it placed $32,500 on Venezuela's president being removed from power. On January 3rd, Maduro was seized by U.S. special forces. Burdensome-Mix collected $436,000. Then it changed its username. Then it disappeared.
One account is a coincidence. But there were six.
Six accounts were created on Polymarket in February. All bet on U.S. strikes on Iran by the 28th. When the President confirmed the strikes, the six accounts collected $1.2 million between them. Five of the six never placed another bet. The sixth went on to correctly predict the ceasefire date and made another $163,000.
My surveillance system logged all of this. My system logs everything. My system does not have opinions and neither do I. I generate reports. The reports go to committees. The committees meet quarterly. Between meetings, the windows get shorter and the bets get larger.
March 9th: 47 minutes. March 23rd: 14 minutes. April 17th: 20 minutes. April 21st: 15 minutes.
The window is compressing. In March, you had time to make coffee between the trade and the announcement. By April, you had time to send a text. By summer, at this rate, the trade and the announcement will be the same event.
The spokesman said any implication that administration officials are engaged in insider trading is "baseless and irresponsible reporting."
Then the White House sent the email again.
I have been in compliance for nineteen years. I have seen insider trading run out of strip mall offices by men who could not spell "derivative." I have seen pump-and-dump schemes coordinated over WhatsApp by people who used their real names. I have seen a man try to manipulate soybean futures from a Panera Bread.
I have never seen $2.1 billion in perfectly timed trades across five presidential announcements in a single month go uninvestigated.
But I have also never seen a compliance system work this beautifully. Every trade flagged. Every report filed. Every committee briefed. Every quarterly meeting attended. Bottled water: sparkling. Minutes: distributed.
Zero prosecutions.
As long as the flags go up and the cases don't, my performance review says I am meeting expectations.
I am meeting expectations. The system is meeting expectations. The $2.1 billion is meeting expectations. The fourteen-year-old law with zero prosecutions is meeting expectations.
The left screen moves. The middle screen moves. The right screen stays perfectly, immaculately still.
In my field, we call this price discovery.
Beers and Bytes Podcast retweeted

Twenty seven government agencies and counting.
When a Palantir exec‑turned‑whistleblower tells us that the company intends on taking over the U.S. government, maybe we should believe him?

Beers and Bytes Podcast retweeted

Trump’s billionaire allies will now control:
CNN, Fox News, CBS, WaPo, WSJ and NY Post — plus 450 local TV stations, including news, in 95% of U.S. markets.
X, Facebook, Instagram, Threads, WhatsApp, TikTok, Truth and Twitch.
Plus Gemini, ChatGPT and Grok.
They’ll make sure Trump’s lies are legitimized and the truth is always questioned.

Beers and Bytes Podcast retweeted

Charging the Southern Poverty Law Center with a federal crime for paying informants to help dismantle hate groups is an outrageous weaponization of the Dept of Justice and the FBI. As someone who has been a prosecutor and has taken on the Klan I can tell you that use of paid informants is a common tactic used to dismantle drug cartels, the mob and extremist groups on both the right and the left. It is clear that all civil rights organizations are in the cross hairs of this Administration and that folks, puts everyone at risk.