

We provide cyber #threatintel on emerging threats, DDoS botnets, and network abuse.
Chicago, IL
Joined April 2017
- Tweets2K
- Following2
- Followers50.7K
- Likes6



Threat actors love disabling security tools. What if you verified your security stack was running before granting access?
Okta Verify + osquery solve this with Advanced Posture Checks, turning every authentication flow into a security watchdog: bit.ly/45nOrde

🚨 Discount AI services promise suspiciously cheap tokens. In reality, they're backed by bots and fake accounts. Okta Threat Intelligence uncovered the scheme, profiled the signup fraud TTPs and took disruptive action. bit.ly/4yTiQ0x


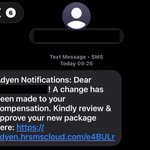
🚨 Smishing campaign targeting hundreds of enterprises: fake "Benefits Portal" texts steal creds, MFA & session cookies, then establish persistence. Advisory & full IoCs for Okta customers: bit.ly/4bCE9cr Blog post for everyone: bit.ly/44uuG3g

3️⃣ Proxy: Targets are forwarded to an AiTM proxy mimicking an enterprise login
4️⃣ Theft: As the user logs in, the proxy steals credentials and the authenticated session cookie
5️⃣ Persistence: Post-auth, the attacker attempts to enroll their own authenticator to maintain access
🛡️ Defensive Actions:
- Monitor Okta System Logs for suspicious, rapid Okta Verify enrollment events.
- Block the listed domains at your gateway.
Full recommendations and public write up here 👉 bit.ly/44uuG3g
Anyone reusing credentials on their Fortinet device? Asking for a friend on AS17511 (219.75.254[.]166) who keeps failing to get their password right.
We analyzed over 300,000 rows of the January 2026 BreachForums database leak to find their users' anonymizers of choice.
Join us in the cantina. 🧵

BreachForums never verified email addresses. A forum admin even told members to use disposable ones.
81% used Gmail anyway. Most of those burner addresses appear nowhere else. The remaining ~5,800 showed up in infostealer malware logs.

Full analysis of the BreachForums network and user data, including top ASNs, VPN usage and blocklist recommendations, are all in our latest blog post.
okta.com/blog/threat-intelli…

A browser extension promised security. In reality, it was a Trojan horse for your crypto.
We tracked the extension, mapped the infrastructure and pulled the plug.
Full breakdown of the takedown: bit.ly/40E9i9N

Watch @Okta’s exclusive interview with @HHieupc, a cybercrime investigator who explains the Vietnamese cybercrime-as-a-service ecosystem and how much of it operates in the open. Read our full research here: bit.ly/4r6NgHn
Fake accounts fuel global fraud. Our latest research uncovers a sprawling cybercrime-as-a-service ecosystem in Vietnam that sells fake and hacked accounts on a massive scale.
Read our full research and raise your identity security posture: bit.ly/4b7Shtp

University students using "tutors" are being extorted for thousands, but the risk is bigger: When students turn over login credentials, malicious actors can pivot to sensitive university systems and perpetrate fraud. okta.com/blog/threat-intelli…

Your star hire might be a DPRK agent. 🇰🇵 @Okta reveals how state actors use stolen LinkedIn IDs, AI-generated faces, and forged git commits to bypass HR. Verify identities before they're on your payroll! #opentowork bit.ly/4quh8go

ALT AI-generated image of a post from a North Korean state actor
Google disrupted IPIDEA, a major residential proxy network. Our data confirms a sharp drop in their active IPs following the action. 📉
Protect your Okta org today: block IPIDEA and residential proxies with dynamic network zones bit.ly/3OiZVJz

Our promise to you: serving up the bad packets. That's why we wrote about how to use threat intel right in @Auth0 Actions. bit.ly/494lt4M
Revamped site, new IoCs. In addition to bad ASNs, we've got disposable email domains beloved by threat actors inside 👉 bit.ly/4b4GUUE
