





Really honored to be part of BlueHat Asia. Met so many brilliant researchers and cool people here. Huge thanks to MSRC for the invitation and for organizing such an amazing event. Had a great time!🙌


Sometimes the most interesting vulnerabilities are not caused by a single bug, but by assumptions that quietly break over time.
At BlueHat Asia, Microsoft MVRs Zhu Qing and b2ahex (@b2ahex) shared their research into the Windows DirectX kernel, uncovering dozens of vulnerabilities spanning local privilege escalation, guest-to-host attack paths in Hyper-V, information disclosure, and denial-of-service scenarios. Their work resulted in 32 reported vulnerabilities and 26 confirmed CVEs at the time of submission.
From user-mode interactions with dxgkrnl to host-side processing in GPU-PV environments, the researchers demonstrated how subtle violations of security assumptions can create powerful exploitation opportunities.
Beyond the vulnerability findings themselves, the talk offered a practical framework for security research: trace every path from attacker-controlled input to the final privileged action, and verify that security guarantees still hold at each step. It was a compelling look at how deep technical analysis can uncover entire classes of vulnerabilities across complex systems.


b2ahex retweeted

We're excited to announce our next BlueHat Asia speakers: b2ahex (@b2ahex), Senior Security Researcher, four-time MSRC Most Valuable Researcher (MVR), and Pwnie Award winner; and Zhu Qing, CTO of Snowrock, Senior Security Engineer, MVR, and top MSRC Windows Bounty recipient.
In their talk, "Broken Contracts in the DirectX Kernel: Local Elevation of Privilege and Hyper-V Guest-to-Host Remote Code Execution," b2ahex and Zhu Qing present a systematic study of object lifetime bugs in the Windows DirectX kernel, a component that today spans the boundaries between user mode, kernel mode, graphics drivers, and virtualized environments.
During their research, the pair uncovered recurring vulnerability patterns involving handle resurrection, object type confusion, object lifetime management failures, and guest-controlled handles crossing trust boundaries. These issues affected both traditional Windows graphics paths and Hyper-V GPU paravirtualization scenarios, demonstrating how security flaws in graphics subsystems can evolve into virtualization isolation risks.
Their work led to the reporting of 32 vulnerabilities in Dxgkrnl components, spanning Windows Hyper-V remote code execution, elevation of privilege, kernel information disclosure, and denial of service vulnerabilities. At the time of submission, 26 of these reports had been confirmed and assigned CVEs.
Through real-world case studies, the session examines both local privilege escalation and Hyper-V guest-to-host vulnerabilities, explores the root causes behind these bug classes, and discusses practical approaches for strengthening object lifetime management, handle validation, locking mechanisms, and virtualization boundary protections. This is a rare opportunity to hear directly from researchers who have spent years uncovering some of the most impactful vulnerability classes within the Windows graphics stack.

AI is getting really useful for vuln research. With some manual guidance, I used GPT-5.4 to find some Windows kernel bugs, and the points in the image still feel obvious.
Even so, its already a fun and powerful tool in the workflow. Curious how other researchers are using it😃

b2ahex retweeted
Congratulations to all the researchers recognized in this quarter’s MSRC 2025 Q3 Security Researcher Leaderboard! Thanks to all the researchers who partnered with us for your hard work and continued dedication to securing our customers.
Learn more in our blog post: msft.it/6016sfncp
We also want to recognize the top 10 researchers in the leaderboard:
🥇Brad Schlintz (@nmdhkr)
🥈 Yuval Avrahami
🥉 b2ahex
4. Jianyang song
5. Felix B.
6. Haifei Li @HaifeiLi
6. tuandv of Viettel Cyber Security
8. P1hcn
9. 0x140ce @0x140ce
10. Matthew Jensen

ALT Q3 leaderboard


Won the @PwnieAwards for Best Desktop Bug and was nominated for Best RCE Bug. Congratulations to all the winners and nominees! 🫣☺️

Thanks so much for another excellent year of Pwns! If you missed the show check out the winners here:
docs.google.com/document/d/1…

#5 😸

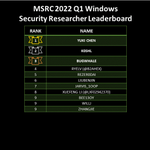
Congratulations to all the researchers recognized in this quarter’s MSRC 2022 Q4 Security Researcher Leaderboard!
For more information, check out our blog post: msrc-blog.microsoft.com/2023…
#cybersecurity #securityresearch #msrc

b2ahex retweeted

Here is my writeup for 2 Windows kernel bugs I reported to MSRC. Both are race conditions that cause Use-After-Free. As there is very few windows kernel writeups I share my research methodology and more. Hope it helps other researchers. Share it😀
dannyodler.hashnode.dev/raci…
b2ahex retweeted
Check out the scrolling MVR list that played at the MSRC Black Hat party! @guhe120 @pnig0s @callum_infosec @wtm_offensi @MDeilamyM @edwardzpeng @bee13oy @SinSinology @Hperalta89 @b2ahex @kasifdekel @jq0904 @Creastery @M3ikShizuka @ronenshh @Yanir_ @hillstone_lab @D1iv3 @DrAzureAD
Congratulations to our MSRC 2022 Most Valuable Researchers! Thank you to all the researchers who have helped secure our customers. Check out our blog for the full list: msrc-blog.microsoft.com/2022… #cybersecurity #securityresearch

b2ahex retweeted

I make a BSOD of Win10 with CVE-2022-30151, which was discovered by @b2ahex and patched last week. This vulnerability is a race condition bug, which results in Double-Free. I share my scenario slide to trigger this vulnerability and a crash screenshot. Thx.


CVE-2022-24542, although there is only one cve number, it contains more than 10 different privilege escalation vulnerabilities that I submitted last December, and they have basically existed in the system for 20-30 years.
#CVE_2022_24542

