






Pian retweeted

No gatekeep.
- Website yang gue pake buat dapet gaji standard US tapi bisa kerja remote dari Jogja: hiring.cafe
- Website buat cari klien AI video dari US/Europe: contra.com
- Website buat jari project clipping/UGC (dapet duit dari impression post di Sosmed): contentrewards.com
Fokus cari kerja/project di 3 website ini dapet IDR 40juta/bulan sangat sangat realistis


Pian retweeted

Andrej Karpathy spent 8 years at OpenAI and Tesla
Last week he compressed everything he knows into one free 2-hour lecture
Prompts → Agents → Harness → Graphs → Loops
People spend $15k on bootcamps that teach less than this
You probably don't have 2 hours right now
Don't let it vanish from your feed
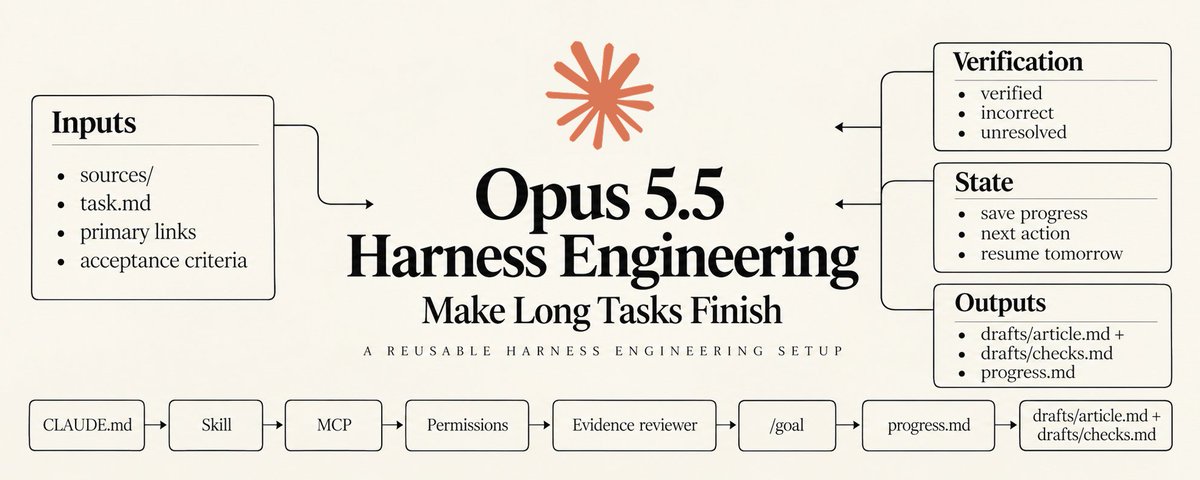
Watch it, then read the full Opus 5.5 harness engineering guide below

Pian retweeted

web favorit cari kerja WFH gaji tinggi:
• upword. com (dibayar jam)
• fiver. com (jutaan per project)
• sribu. com (per project)
• projects. co. id (per project)
• freelancer. com (per project)
• total. com (per jam)
• guru. com (perjam)
• 99designs. com (per project)


Pian retweeted
tier list personal AI agent (versi pribadi)
S+ hermes
fully customizable, bisa dipake buat apa aja
S grok bot
paling enak dipake sehari-hari, gampang dipake, cepet, satset, connect X langsung
A muse, gemini spark, poke
- muse: gampang dipake, beberapa temen juga nyaranin
- gemini spark: udah include di google ai pro, nyambung ke gmail, calendar sama docs
- poke: tinggal chat kayak ngetik ke temen
B dots, duet, openclaw, instinct
- dots: subsnya mahal
- duet: masih baru, waitlist US doang, usage ngikut limit claude jadi kureng
- openclaw: gratis dan open source, tapi harus setup sendiri
- instinct: gratis, tapi jarang ada yang beneran pake
C cue (manus)
who use this lmao
ini penilaian pribadi ya, kalian pake yang mana?

Pian retweeted

TV Android lo berat & penuh bloatware? Bisa bikin ringan & bersih tanpa root, cuma butuh laptop + AI.
Pastikan TV sama laptop satu WiFi.
Buka Setelan → Sistem → Tentang, ketuk Build Number 7x sampe Opsi Developer muncul. Aktifin USB Debugging & Wireless Debugging.


Pian retweeted

Buat yang tanya tutor
1. pastikan tv nya andro google, belum coba yg lain, kalau mau kirim aja kesini nanti kita coba wkw.
2. konek ke wifi yg sama dengan tv, atau usb kabel
3. siapin ai yg mau dipakai, bebas. saya sih pakai claude, kalau mau free bisa pakai Opencode (pilih deepseek atau GLM)
4. di tv andro, ke settings -> cari nomer build -> klik ok di remote 7x untuk buka pandora box , developer mode.
5. ke developer menu, aktifkan USB debugging, wireless debuggin kalau ada.
kalau ga ada wireless debug dia tetap bisa via wifi, in someway si claude bisa konekin itu asal bisa cast via browser
6. buka ai tools nya itu, minta lakukan scan dulu untuk deteksi smart tv. setelah terdeteksi dia akan install adb.
7. minta ai tools untuk lakukan debloat, dan minta beberapa apps kesukaan kalian jangan dihapus. misal netflix, siaran tv langsung dkk
enjoy


Pian retweeted

Saya bikin video soal motion graphics yang bisa kalian bikin di @claudeai .
Coba juga fitur skill, instruksi yang disimpan. Kita simpan jadi satu style, lewat fitur skill. Nanti kalau mau bikin lagi tinggal panggil e.g: /video-explainer
Simak dan bookmark ya video ini:
Pian retweeted

kalo perusahaan lu kecil, Cloudflare nembokin infrastruktur lu secara gratis.
kalo perusahaan lu udh skala enterprise, harganya sangat2 worth it utk tembok perlindungan sekelas Cloudflare.
saya cinta Cloudflare, saya siap locked in sama Cloudflare ❤️

Cloudflare has deployed default web application firewall (WAF) protections for newly disclosed PHP vulnerabilities before public disclosure. The rules use request and response signals to stop exploit attempts and prevent exposed data from reaching attackers. cfl.re/488w8dc

Pian retweeted

PLEASE.
Siapapun kalian yang sudah pakai coding agent jadi bagian tak terpisahkan dair kehidupan, pakai lah ini.
SEKALI AJA di app apapun yg kalian buat. Daripada menyesal di masa depan.
github.com/cloudflare/securi…

Pian retweeted

Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.

Pian retweeted

URGENT. Klo web kamu pakai PHP, segera update hari ini.
Ini zero-day. Cara nyerangnya bocor duluan sebelum patch keluar. NSA sampai bilang, klo belum bisa update, matiin sistemnya sekarang.
69% website di dunia jalan pakai PHP. Web pemerintah, bank, kampus, toko online, web kantor kamu.
Ini kenapa?
- Ada 2 bug kritis di PHP, skornya 9.2 dari 10
- Detailnya udah bocor ke publik
- Attacker tinggal cari web yg blm update
Penyebabnya apa?
- Attacker cukup kirim 1 form atau upload file yg udah diakalin
- PHP salah ngurus memory pas request itu diproses
- Dari situ attacker bisa jalanin perintah apa aja di server kamu
- Ga perlu login, ga perlu password
Risiko klo ga update?
- Attacker masuk dan pegang server kamu
- Akses langsung ke file dan database
- Data user, password, data transaksi dicuri
- Web dirusak, ditanam backdoor, dijadiin lapak judol
Siapa aja yg kena?
- Semua PHP di bawah 8.5.12, 8.4.27, 8.3.36, 8.2.35
- PHP 8.1 ke bawah ga dapat patch sama sekali
Apa yg harus dilakukan sekarang?
- Update PHP di server hari ini, update WordPress aja ga cukup
- Belum bisa update? Matiin dulu sistemnya sampai aman
- Cek versi pakai php -v atau di panel hosting
- Pakai shared hosting? Tagih hosting kamu hari ini juga
- Masih PHP 8.1 ke bawah? Upgrade sekarang
Jangan tunggu besok. Jangan anggap remeh zero-day.

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Pian retweeted

やばすぎるね。穴塞ぐ方法は公開されてないけど、穴の入り方は公開されてしまっている。

PHP Remote Code Execution (CVE-2026-109618 & CVE-2026-109619)
Information about two new remote code execution (RCE) vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS v3.1 10 / 10), has leaked ahead of their coordinated disclosure, and security firm Watchtowr Labs confirmed that the flaws are real. Both vulnerabilities are due to be disclosed on Thursday, October 22, alongside patches. Until those advisories land, no fix is available, which leaves the flaws as zero-days in PHP installations everywhere.There is currently a scheduled release of an advisement and possible patch on Wednesday, October 21 2026 at 14:00 UTC.
Below is a video of a researcher, maybe the original researcher, showcasing the exploits.
#CTI #BlueTeam #ThreatIntel #CVE-2026-109618 #CVE-2026-109619
Pian retweeted
Kalau kamu buka halaman dv-g3b-emudhra.we-have-a-pro… dan tidak muncul error seperti ini (ERR_CERT_REVOKED) maka browser kamu perlu segera di-update.


private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
emudhra.we-have-a-problem.co…
