

Python || AgenticAI 🛠️ || Sharing Content 📝 || Techy from Hyderabad 🚀 || DM ✉️ for Collab https://xitter.cf/t.co/sk8GgQoJwm
Joined August 2025
- Tweets6.5K
- Following722
- Followers5.4K
- Likes9.8K




Pinned Tweet
A few weeks ago, I started turning the Kubernetes commands I use every day into something I could actually keep as a reference.
Days of writing.
Reviewing commands.
Creating diagrams.
Simplifying explanations.
Going through every page again and again.
It finally became a 20-page Kubernetes Handbook. ☸️
I decided to give it away for free to DevOps & Kubernetes learners.
Less Googling. More practicing. 🚀
📘 Free download: asynctrix.gumroad.com/l/olpg…

Distributed Systems Fundamentals 👇

Distributed Systems Fundamentals, Part 1/3.
A service is only as reliable as its ability to handle failures in the services it depends on.
In this series, we'll explore practical distributed systems concepts that every backend engineer should understand, starting with timeouts, retries, exponential backoff, and jitter.
A few rules to remember:
• Always set timeouts for network calls.
• Use exponential backoff to avoid retrying too aggressively.
• Add jitter to prevent retry storms.
• Retry only when it makes sense, and make operations idempotent.
Because in distributed systems, failures are inevitable. The goal is to stop one failure from taking down everything else.

AsyncTrix retweeted

Hiring Post 📫

Hiring - Junior Python Developers
1. Must have 1 year experience shipping with Python
2. Ai Native; uses agents for shipping
3. Shipped features end to end; (we've asked for a loom video demo for this)
Details and application link:
jobs.clanx.ai/o/junior-backe…
Happy Job Hunting :)

AsyncTrix retweeted
31. Why Does VPC Peering Get Difficult at Scale? 👀
Connecting 2 VPCs is simple:
VPC A ↔ VPC B
That's VPC Peering.
But what happens when you have 50 VPCs?
You end up managing many point-to-point connections and routes.
That's where Transit Gateway helps.
VPC Peering
→ Simple point-to-point connectivity
Transit Gateway
→ Centralized hub for many VPCs
Start simple.
Scale smart. 🚀


30. Why Use VPC Endpoints? 👀
Your private EC2 needs to access AWS services.
Do you really need to send that traffic through a NAT Gateway?
VPC Endpoints let you access supported AWS services privately.
Gateway Endpoint
→ S3 & DynamoDB
→ Route table based
→ No NAT Gateway required
Interface Endpoint
→ AWS PrivateLink
→ Private IPs / ENIs
→ Many AWS services
Simple understanding:
Gateway → S3 / DynamoDB
Interface → Many other AWS services
Less NAT dependency.
Private connectivity.
Better network design. 🚀

VPC Peering Simplified 👇
31. Why Does VPC Peering Get Difficult at Scale? 👀
Connecting 2 VPCs is simple:
VPC A ↔ VPC B
That's VPC Peering.
But what happens when you have 50 VPCs?
You end up managing many point-to-point connections and routes.
That's where Transit Gateway helps.
VPC Peering
→ Simple point-to-point connectivity
Transit Gateway
→ Centralized hub for many VPCs
Start simple.
Scale smart. 🚀
30. Why Use VPC Endpoints? 👀
Your private EC2 needs to access AWS services.
Do you really need to send that traffic through a NAT Gateway?
VPC Endpoints let you access supported AWS services privately.
Gateway Endpoint
→ S3 & DynamoDB
→ Route table based
→ No NAT Gateway required
Interface Endpoint
→ AWS PrivateLink
→ Private IPs / ENIs
→ Many AWS services
Simple understanding:
Gateway → S3 / DynamoDB
Interface → Many other AWS services
Less NAT dependency.
Private connectivity.
Better network design. 🚀
AsyncTrix retweeted
🚨 Your docker pull can be a security problem.
Docker Engine 29.9.1 just shipped with an updated containerd 2.4.2.
The update fixes multiple vulnerabilities where a malicious or untrusted registry could potentially crash containerd during image pulls.
One issue involves a malformed digest.
Another involves a crafted "Content-Length" response during parallel layer downloads.
And another could allow unbounded layer data to consume the host's disk before size validation.
This is why container security isn't only about what's running inside the container.
Even the image pulling process itself is part of your attack surface.
If you're running Docker Engine, check your nodes and upgrade to 29.9.1.
Especially if those nodes pull images from registries you don't fully control.
AsyncTrix retweeted
30. Why Use VPC Endpoints? 👀
Your private EC2 needs to access AWS services.
Do you really need to send that traffic through a NAT Gateway?
VPC Endpoints let you access supported AWS services privately.
Gateway Endpoint
→ S3 & DynamoDB
→ Route table based
→ No NAT Gateway required
Interface Endpoint
→ AWS PrivateLink
→ Private IPs / ENIs
→ Many AWS services
Simple understanding:
Gateway → S3 / DynamoDB
Interface → Many other AWS services
Less NAT dependency.
Private connectivity.
Better network design. 🚀
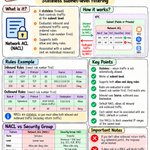
29. Security Group vs NACL ⚔️
Same VPC. Different jobs.
Security Group
→ Resource level
→ Stateful
→ Allow only
NACL
→ Subnet level
→ Stateless
→ Allow + Deny
→ Rules evaluated in order
Easy mental model:
🔐 Security Group → Protect the resource
🚧 NACL → Filter the subnet
Use both for defense in depth.

Understand VPC Endpoints 👇
30. Why Use VPC Endpoints? 👀
Your private EC2 needs to access AWS services.
Do you really need to send that traffic through a NAT Gateway?
VPC Endpoints let you access supported AWS services privately.
Gateway Endpoint
→ S3 & DynamoDB
→ Route table based
→ No NAT Gateway required
Interface Endpoint
→ AWS PrivateLink
→ Private IPs / ENIs
→ Many AWS services
Simple understanding:
Gateway → S3 / DynamoDB
Interface → Many other AWS services
Less NAT dependency.
Private connectivity.
Better network design. 🚀
29. Security Group vs NACL ⚔️
Same VPC. Different jobs.
Security Group
→ Resource level
→ Stateful
→ Allow only
NACL
→ Subnet level
→ Stateless
→ Allow + Deny
→ Rules evaluated in order
Easy mental model:
🔐 Security Group → Protect the resource
🚧 NACL → Filter the subnet
Use both for defense in depth.
AsyncTrix retweeted
Lambda is starting to look less like just functions
AWS just introduced Lambda Web Functions🔥
The interesting part?
You can run a normal HTTP application on Lambda without rewriting it into a Lambda handler.
Your app listens on a port.
Lambda takes care of the infrastructure and scaling.
It can also handle multiple requests concurrently in the same execution environment.
This feels like AWS is bringing the simplicity of deploying a web service to the serverless model.
Lambda is getting closer to running apps, not just functions.
share.google/Zp3np7uvHSdOlZe…
7/8 The interesting part is that these aren't four separate agents or products.
They work together around the same agent.
LangGraph provides the runtime.
Deep Agents provides the harness that helps the agent manage longer, more complex work.