

An Internet Intelligence Company with hyperspecialization in Subdomain and Exploit Intelligence.
India
Joined November 2023
- Tweets1.6K
- Following337
- Followers573
- Likes2.1K





Pinned Tweet
In 2020 we open-sourced Kenzer, a recon and scanning framework for bug bounty hunting: github.com/ARPSyndicate/kenz…
Today it's reborn as a full security platform.
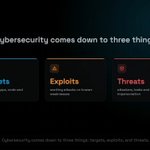
Cybersecurity comes down to targets, exploits and threats. Most teams cover them with separate tools that all score them differently, so nobody can answer the one question that matters: how exposed are we?
Kenzer brings it into one place, with one security grade. It covers SCA, SAST and DAST, Fourth-party risk and Dark web monitoring. Every finding is ranked by real exploitability using VEDAS, our exploit intelligence covering nearly 5 million vulnerabilities.
Built by ARPSyndicate. Watch the 4-minute tour below.
kenzer.arpsyndicate.io
#cybersecurity #bugbounty #vulnerabilitymanagement #appsec
ARPSyndicate - Cyber & Open Source Intelligence retweeted

We launched OSS Scanner, which gives critical open source projects free, periodic vulnerability scans from our strongest models.
Each finding includes a proof-of-concept, and a patch where possible.
red.anthropic.com/oss-scanne…

ARPSyndicate - Cyber & Open Source Intelligence retweeted

Bro reverse-engineered Satoshi’s original 2009 bitcoin.exe using Opus 5.5 rebuilt byte for byte. 😭
Produce identical executable .exe matches the same historical SHA256 as the one released 17 years ago.
- Debug build with max optimization only on the mining hash,


i rebuilt satoshi's 2009 bitcoin.exe byte for byte!
afaik nobody has been able to perfectly recreate the executable published in 2009 from source, because we didn't know the exact build environment that was used.
using opus 5.5, i reverse-engineered satoshi's build machine from the binary.
it now outputs an exe with the exact same sha256 as the 2009 release!
ARPSyndicate - Cyber & Open Source Intelligence retweeted

We have released a free open source tool 'Zero Breach' - that can identify whether a recent Israeli spyware campaign left traces on your PC - the one Citizen Lab exposed, where Israeli ad-tech was used to infect journalists through 'no-click' ordinary ads.
It needs Python installed (python.org — tick "Add python.exe to PATH" during setup). Then open PowerShell in the folder where you saved it and run:
python -X utf8 zero-breach.py
It takes about 15 minutes. It only reads - it changes nothing, needs no admin, and never connects to the internet. It checks for 338 indicators and tells you if one of your browsers interacted with one of the infected ads in the past. (It also checks for Candiru infection)
Download it here: github.com/interplains/zero-…
You can also check whether your browser or device already blocks these kinds of ads, without downloading anything, here:
archivegenocide.com/scan/
You are looking for a green result ✅ - if not, fix your browser settings, install an ad blocker / DNS resolver.
For phones: Tens of thousands of apps show these ads, so we suggest you set up a DNS resolver (NextDNS, AdGuard, or a router/Pi-hole blocklist) so your phone blocks all of them automatically.
We also publish ready-made blocklists you can subscribe to as well. Use them.
Pease report any issues in our telegram linked in bio
God bless.

ARPSyndicate - Cyber & Open Source Intelligence retweeted

‼️ China proposes banning exports of AI used for cybersecurity.
It wants to ban exports of:
- AI that writes malware beating a mainstream antivirus 85%+ of the time
- AI malware that escapes sandboxes or rewrites 50%+ of its own code per run
- AI agents built for defence or critical infrastructure
- AI models trained on China's "core data"
A licence would be needed for:
- AI that finds 5+ unknown high-severity flaws in a major OS on its own
- AI that builds working exploit chains for major operating systems or browsers
- Weights of models with 2T+ parameters or a global top-10 ranking
- AI chip and memory chip designs


ARPSyndicate - Cyber & Open Source Intelligence retweeted

🚨 Rapid Response: CVE-2026-110447 (CVSS 9.2), a critical flaw in the Collabora Online Built-in CODE Server for Nextcloud, has reportedly been exploited in the wild.
Censys detects 19,454 hosts and 103,350 web properties with the app installed, not all confirmed vulnerable. bit.ly/4BbTBrm

ALT Censys world map highlighting countries by host count from Censys. Notable figures include Germany with 6,965 hosts, France with 1,819, the United States with 1,607, and Russia with 1,382. A list on the side outlines the total hosts for other countries.
ARPSyndicate - Cyber & Open Source Intelligence retweeted
🚨 BREAKING: A Broadcom Wi-Fi bug lets anyone in range run code on routers without the password.
Quentin Kaiser showed it on Proximus, Orange Belgium and VOO routers and estimates ~1.5M in Belgium are exposed, none patched.
The bug dates to 2010. Broadcom won't assign a CVE.


ARPSyndicate - Cyber & Open Source Intelligence retweeted

Unauthenticated RCE chain in Plex:
$500 bounty
Writeup: zmain.info/blog/plex2shell
PoC: github.com/code-zm/plex2shel…
Patch your servers!
ARPSyndicate - Cyber & Open Source Intelligence retweeted

I feel bad man 😭 Apologies to the thousands of VPS and compute engineers worldwide spending their weekend emergency patching and rebooting hypervisors because of CVE-2026-99999. Security bugs really do love getting disclosed right before the weekend.


ARPSyndicate - Cyber & Open Source Intelligence retweeted

Exploiting a 16 zero bytes write at a partially controlled offset in Linux kernel (CVE-2026-72018)
xbow.com/blog/no-time-to-pwn…
Credits Baul Lee
#infosec


@citizenlab: citizenlab.ca/research/how-d…
@ConfiantIntel: blog.confiant.com/p/adint-we…
On-device mobile defence: encryptlayer.net
Open intel feed: github.com/ARPSyndicate/encr…

ARPSyndicate - Cyber & Open Source Intelligence retweeted

For the second time in Google Chrome’s history, Google awarded a $250,000 bounty for a full-chain exploit… to @XBOW. Here’s the full story:
At an all-hands at the start of 2026 in Malta, I set the team a crazy challenge. A full-chain exploit of Chrome by the annual Black Hat cybersecurity conference in August.
I believed there were few better tests of whether @XBOW could move beyond web applications to desktop software, servers and devices.
Chrome is one of the most hardened pieces of software on the planet, used by more than half the world’s population.
A full-chain exploit lets an attacker take total control of a machine, where they can read every email, password and bank login the user types. You don’t need to download anything or click a phishing link. Visiting the wrong site is enough.
So @moyix, Andres Luksenberg, Baul Lee, and Willem Pinckaers took on the challenge along with a fifth teammate: OpenAI's GPT-5.6 Sol.
They built a chain they thought would win, but Google told us they already knew one of the bugs.
We were already in Las Vegas for Black Hat and DEF CON, and the team didn’t want to go home without the win.
So Brendan and the agents built a new exploit in just 6 days.
We submitted it to Google and waited.
The news came through that we'd done what should’ve been impossible. A full-chain bounty of $250,000, the first awarded under Google’s 2026 rules.
It took just 6 days and $40,000 of compute to construct an exploit that affects a billion users of Chrome on Windows. An intelligence-agency veteran told me his team used to spend 6 months on this kind of vulnerability.
My takeaway: the cost of finding truly critical vulnerabilities is collapsing, for attackers and defenders alike. Restricting powerful models is not the answer; GPT-5.6 Sol is already public.
But defenders have one advantage attackers never will: they can test their own code first.
Assume your software is exploitable. Whoever is hunting your bugs has the same building blocks we did.
This is cause for urgency but not panic.
XBOW is now developing an autonomous product for testing compiled software (desktop applications, servers, embedded devices), and partnering with the world’s top organizations to design that product.
If you’d like to be one of them, get in touch.
P.S. Restart Chrome whenever the Update button appears!


ARPSyndicate - Cyber & Open Source Intelligence retweeted

Rarely I post bug bounty tips anymore but this small gem is unknown to most ;)

Your new Android phone could be hacked before you even switch it on.
@Bitdefender found malware baked into cheap phones at the factory — hiding as a fake "System" app you can't remove, running ad fraud and turning your phone into a botnet.
150+ countries. Breakdown below.
Bitdefender report: bitdefender.com/en-us/blog/l…
On-device Android firewall: encryptlayer.net
Open intel feed: github.com/ARPSyndicate/encr…

ARPSyndicate - Cyber & Open Source Intelligence retweeted

UPDATE: I can confirm that the Ledger supply chain is compromised in Europe as well. @Ledger should initiate an immediate product recall to protect users.
I just purchased a second device from a different Mediamarkt location today, recorded the unboxing process, and discovered spyware once again (video linked in the second tweet).
The device was compromised in the exact same manner, featuring identical modifications (such as additional cables and an LTE module). This indicates its a widespread issue rather than an isolated incident, potentially affecting Ledger inventory across MediaMarkt and Saturn stores throughout Europe (comprising over 1,000 stores across 11 countries).
My initial hypothesis was that these devices were returns that looked unopened to the employees and were just sold again as new however, a MediaMarkt employee confirmed that the device I purchased was not a return, and that returned Ledgers are sent directly back to the manufacturer rather than resold.
Store records show the inventory originated from Aqipa GmbH. While Ledger's CTO was unsure if Aqipa serves as the direct distributor between Ledger and MediaMarkt, it appears to be the case. Given that Aqipa distributes across Europe, any physical retail store receiving stock through them may be at risk.
I sent the first ledger to mark and the second one is going to ledger now, so that they can analyse it.
If you purchased a ledger from anyone other than the official ledger store, make sure to check your device!!


ARPSyndicate - Cyber & Open Source Intelligence retweeted
Regarding the Danfoss refrigeration systems hacked in France:
The username is `admin`, and the password automatically changes every day to... the current date.
Yes, today's date.
The French supermarkets affected in today's attacks had exposed all its refrigeration controllers directly to the internet.
Every single device reportedly used the same password: today's date...
There's also a documented authentication bypass: sending a POST request to /xml.cgi can bypass the login entirely.
Via: GossiTheDog


ARPSyndicate - Cyber & Open Source Intelligence retweeted
❗️ Mossad emailed vx-underground offering 47 of Netanyahu's toenail clippings for 8,000 shekels.
He says the mossad.gov[.]il sender is not spoofed, but it was from a compromised Israeli government domain.
We checked: the domain has no SPF or DMARC record. 💀

