

🛡️ digital security guy
Madrid / Sanabria
Joined February 2009
- Tweets6.2K
- Following1.2K
- Followers11.5K
- Likes1.5K





AstroScan is now public 🛰️ Checks selected high-impact Astro framework vulns the right way: a version match is only an upgrade candidate, and every positive needs discriminating evidence. One Python file, no deps.
github.com/aramosf/astroscan

The bright side of the pwnagepocalypse? Critical RCEs are so massive and automated now that the industry finally stopped wasting time giving them catchy brand names, intro music, and dedicated landing pages with custom logos. #vibepwn
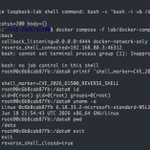
I'm still burning tokens, now the PoC of CVE-2026-61500: Rejetto HFS session forgery to RCE github.com/aramosf/CVE-2026-…
(Vulnerability discovery Zach Hanley @hacks_zach)

I love it when I come across things like that in the console (in spanish: CONFIRMED IN CODE - HIGH/CRITICAL 0-day candidate)
... And five minutes later it says:
-Oh no, it was a false positive.

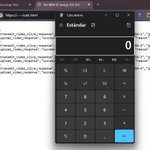
💣 RCE in Synology Image Assistant for Windows any website can abuse the official Chrome extension and desktop client to execute commands as the signed-in user. PoC launches calc.exe. Reported to @Synology but not relevant to them. I will soon disclose many other critical vulnerabilities.

Why are my agents so lazy?
-I'll compile the dossier with its own ID tomorrow and prepare an advisory and email for you, if that's okay. It's late and this has already been captured.
✻ Waiting for 1 background agent to finish
❯ Tomorrow is today, get it ready, I'll send it

🐧 New: LPE PoC + x86_64 LPE for CVE-2026-64468 — a use-after-free in Linux Binder's binder_free_transaction().
Full credit to Alice Ryhl (Google) for finding & reporting it, and Carlos Llamas for the fix. 🙏
Repo → github.com/aramosf/CVE-2026-…


Today we are possessed by two forces, and we are using both with equal energy. One is more useful offensively, the other more useful defensively. The distribution of power is still being drawn, but any space one company doesn't want to occupy will be occupied by another.
At least in cybersecurity.
(We'll talk about the European space issue another day.)
🤖 Made with AI

This is my third Proof of Concept (PoC) for privilege escalation in Linux. In this case, it comes from a commit that fixes the problem (still waiting for a CVE...). Linux AF_PACKET hard_header_len race: local root exploit (03390aa): github.com/aramosf/03390aa-p…. The two previous ones were: CVE-2026-68138 github.com/aramosf/CVE-2026-… and CVE-2026-68398 github.com/aramosf/CVE-2026-…. I keep wondering if I'm able to weaponize this with my limited knowledge, what other organizations are doing. We shouldn't be talking about embargoes; we should be talking about how to change processes that have remained unchanged for 20 years and are saturated and broken.
We keep burning tokens. This repository contains a build-specific local privilege-escalation exploit for Linux, CVE-2026-68398, a use-after-free race between PPPoL2TP: github.com/aramosf/CVE-2026-…
(I have another one ready, but there's no CVE yet? I don't understand it, really... but I'll keep it a little longer)
Stay tuned!
Vuln discovery and fix are credited to Norbert Szetei
I have published a Proof of Concept for the security note CVE-2026-24031: Dovecot SQL authentication bypass (authentication + user enumeration) at: github.com/aramosf/CVE-2026-… discovered by whisperer@yeswehack

I’ve published a proof of concept for CVE-2026-68138, race condition in the Linux kernel’s traffic-control subsystem (net/sched). including the code required to reproduce and validate the vulnerability.
PoC and technical details:
github.com/aramosf/CVE-2026-…


Incluso a los de seguridad nos tienen que concienciar para prepararnos e ir ajustando los algoritmos de cifrado. Por que en casa de herrero… criptografía débil. La imagen es haciendo ... linkedin.com/posts/aramosf_i…
