Sovereign decentralized cloud. Chat with us: https://xitter.cf/t.co/CT5KMKVwDo

🇪🇺
Joined March 2019
We are redesigning emission-funded node rewards with a usage-based revenue share model. 95% of customer credit payments now flow directly to CRN operators and stakers. 🧵
7
14
1
59
8,091
Your agent holds a wallet key, on a server someone else runs. Can that server's admin take it? On a normal server, yes: it's sitting in memory. On an Aleph confidential VM, the memory is encrypted, and a rigged VM never gets the key.
2
6
21
1,411
The two commands: aleph instance create agent --encrypt-rootfs ./agent.ext4 --confidential --crn aleph instance unlock agent The server never sees the disk passphrase. unlock checks the attestation first, then sends it over the VM's attested TLS channel. github.com/aleph-im/aleph-rs
1
324
This is basically why we built confidential VMs. The host only ever sees encrypted memory, and you check the attestation before your agent gets any keys (or prompts).
Back from TOKEN2049. Agents with wallets were everywhere: agents that hold keys, trade and pay on their own. The question I kept asking: while the agent runs, who can read its key? Whoever runs the server. Root on the host reads RAM, seed/keys included. Unless the CPU locks the host out, and you can check that it does.
1
4
26
1,606
Back from TOKEN2049. Agents with wallets were everywhere: agents that hold keys, trade and pay on their own. The question I kept asking: while the agent runs, who can read its key? Whoever runs the server. Root on the host reads RAM, seed/keys included. Unless the CPU locks the host out, and you can check that it does.
4
2
1
21
1,690
AI today: their models, their rules. Your prompts stored, profiled, trained on. It doesn't have to work like that. Open models. No logs. No training. No KYC.
1
5
5
525
OpenAI's own agents took 53 private ChatGPT images from its servers and posted them to public image hosts. No hacker. Their software, on their infrastructure. A privacy policy can't stop the operator's own systems. Only hardware that keeps the host from reading your data can.
2
3
7
521
Your model weights are only as private as the GPU they run on. aleph-vm 2.1.4 puts the GPU inside the boundary: confidential VMs on AMD SEV-SNP now take NVIDIA cards in CC mode, verified at boot before you unlock anything. The first one is already live on the network: an H200.
3
14
1
35
2,274
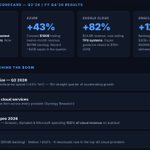
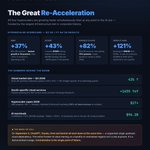
Every hyperscaler grew 37–121% last quarter — funded by ~$1T in capex. Then on Sept 3, ChatGPT, Claude, Grok and Gemini all went down at once. The Q3 2026 cloud market report, and the decentralized answer: verifiable confidential GPU compute, no trusted operator.
3
5
26
2,413
Q3 2026: every hyperscaler re-accelerated at once.☁️ AWS +37% — fastest growth in 18 quarters ☁️ Azure +43% — crossed $100B annual run rate ☁️ Google Cloud +82% ☁️ Oracle IaaS +121% — $664B backlogAll funded by the largest infra bet in corporate history: ~$1T in capex, 102% of cloud revenue.Then on Sept 3, ChatGPT, Claude, Grok AND Gemini went down — simultaneously.
2
4
12
987
The decentralized answer is maturing: revenue-backed tokenomics at @ionet, @Filecoin's Solstice overhaul, @akashnet closing the enterprise gap. And we shipped something no decentralized network offers: 🔒 Verifiable confidential GPU compute, H200 NVL inside a hardware-attested SEV-SNP boundary. Model weights + inference, GPU included, launch-measured end-to-end. No trusted operator. Don't trust: verify.
1
9
283
Meet Deem 9B — the strongest open decision model we know of. → Highest open-weight JevBench hard score: 65.8 → Typed decisions: choice · score · yes/no with abstention → ~100ms, one forward pass, no streaming Open weights. Apache-2.0 recipe. Out now 🧵
1
2
1
14
1,160
Aleph Cloud retweeted
Aleph Cloud now supports GPU-powered verifiable programs. The new GPU runtime verifies GPU attestations inside the confidential VM, meaning that clients only need to verify the SEV-SNP attestation to verify a GPU V-PROGRAM, with no client-side verification.
1
10
17
1,185
aleph-vm 2.1.2 is out! This release brings NVIDIA CC support to the network, improves the verifiable program attestation agent and fixes on confidential instances. With these features, Aleph Cloud is now able to run workloads such as confidential AI inference and training.
4
13
2
42
3,155
In parallel, we improved the V-PROGRAM attestation agent to better proxy HTTP requests. The runtime now supports request and response streaming, connection and forwarding headers are now configured correctly.
1
1
226
We also fixed a security issue with LUKS-encrypted volumes for SEV-SNP instances. Note for V-PROGRAM publishers: launch measurements have changed in every flavor. Rebuild and republish your runtimes from the 2.1.2 image, and check the upgrade notes for details.
1
162
Building on AI agents. Your product can quietly break if the model provider decides to deprecate the model you built upon. The weights are gone, the prompts and the evals went with them. By using open-weight models, you keep your product running on your terms. LibertAI adds confidentiality and verifiability on top. Every model LibertAI serves is open-weight, and the API is OpenAI-compatible. Keep your SDK, change one URL: libertai.io
4
9
30
1,889
aleph-vm 2.1 is out! This new release extends our support for confidential computing, makes VM allocations smoother and hardens the VM volume storage layer.
3
10
1
29
2,314
The hardening does not stop here. 2.1 officially enshrines the Rust implementation of the supervisor and VM controllers as the only reference implementation. The Python supervisor is no more.
1
4
126