




vient retweeted

Yandex School of Information Security is back: academy.yandex.ru/schools/sh…
Wrote a small Hex-Rays plugin to support x86 MOVBE instruction (fused MOV+BSWAP): github.com/vient/ida_movbe_l…
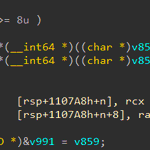
Even with MicroAVX sources on hand it still took like 8 hours to just insert intrinsic calls in Hex-Rays, official docs are very good 🤥

ALT Before, MOVBE inserted as inline assembly, Hex-Rays loses data flow

ALT After, with intrinsics inserted everything is smooth
It's pretty easy to write processor extensions for IDA (see github.com/0xAlexei/WindowsD…), on 0CTF it occured to me that they can be used to "patch" the binary to ease reverse. Example: you want to replace short JMP (2 bytes) at address X with long one (5 bytes) - you have a problem.
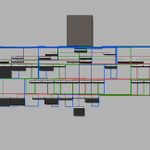
Of course it only patches instructions in IDA, but if you only need static, that's enough. For example, CFG from code1_.bin before (flattened) and after loading the extension:


vient retweeted

Seems like I have finally started a blog!
Hunting for bugs in VirtualBox (First Take)
blog.paulch.ru/2020-07-26-hu…
Made a context menu launcher for IDA which automatically chooses 32 or 64-bit version based on `file` output run in WSL: gist.github.com/vient/db5af9…
Usage: right click on file, Open with IDA. Set your IDA_DIR env or change it in ida_launcher.bat

There are 2 problems:
* There is blinking windows (cmd?) on launch. I tried "start /B ..." in context command, did not help.
* IDA is started as "least priority" window, so you need to Shift+Alt+Tab to it.
Does anybody know how to fix any of them?


vient retweeted

Memory corruption vulnerabilities in VNC protocol implementations, research by @__paulch: ics-cert.kaspersky.com/repor…
xitter.cf/__paulch/status/119460…

Today at @ZeroNights I presented research about memory corruption vulnerabilities in VNC. Full report in English will be available at ics-cert.kaspersky.com on the 22-th of November.
vient retweeted
Hey, I made a gallery of the things I've made while breaking Firefox's rendering code! Check it out! gankra.github.io/glitch/

vient retweeted

Kaspersky ICS CERT invites you to join the IoT Vulnerability Research and Exploitation Training at Security Analyst Summit 2020, April 6-9, Barcelona, Spain.
Book your early-bird ticket now: thesascon.com/training or just ping me in DM!
vient retweeted

Just published my writeup for CPU Adventure at DSCTF, wherein me, @zwad3, @thebluepichu and @jay_f0xtr0t reverse engineered a program written for a completely unknown, custom CPU with no access to the CPU, emulator or any documentation: robertxiao.ca/hacking/dsctf-…
