

offensive security researcher | top 3 @glider_xyz leaderboard 🥉 | ctf player for @infobahn_ctf
Atlantis
Joined August 2022
- Tweets1K
- Following1.7K
- Followers634
- Likes9.8K




Pinned Tweet
Finished joint third 🥉 overall on the glider contest !
Special thanks to @_mr_thank_you_ and the glider team for organizing this amazing contest .congratulations to @ChaseTheLight99 for first place and to everyone who participated

Glider Contest final leaderboard.
🥇 @ChaseTheLight99
🥈 @0xodus
🥉 @0xK42
Congrats, and thanks to everyone who submitted queries.
I am grateful for everyone who sent me messages of support or paid me a visit in this confusing time. Words will fail me time and time again but he will always be in my heart forever.
1
5
183
vi retweeted

my experiences so far with bug hunting on immunefi:
1. waiting for a $100 refund for 5 months now (Contest submission fee, but couldn't submit report)
2. a report closed as oos -> pay $250 mediation after seeing public fix -> changed to duplicate of valid report (no refund)
3. find multiple complex critical chain -> closed as duplicate of valid report because root cause already reported (low 😭)
4. 5x $100 submission for valid duplicate (no public known issue). -> no refund.
5. Staff named mike on discord working non stop and very responsive 🫡. Really appreciate it.


A small win for @iitz_ctfguy and myself. Another confirmed medium in the bag, this time on immunefi. more to come
I just found a confirmed bug on @immunefi #immunefitribe immunefi.com/s/ss/?severity=…

vi retweeted

Our AI found a bug that let anyone mint infinite XRP, with $94B at risk. It had been hiding in one of the most audited codebases in crypto for nearly a decade, and earned us the maximum $250K bounty.
Here's how it went unnoticed, and how we found it.
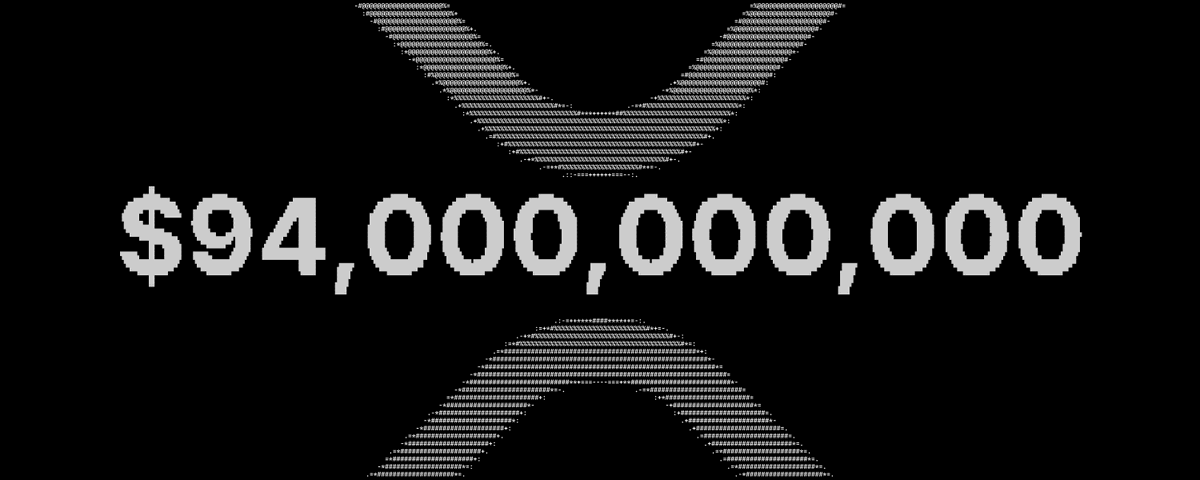
vi retweeted

We audited parts of @0xMiden's zkVM, written in a custom assembly language called MASM. MASM originally had no developer tooling, so we used Claude and Codex to build a decompiler and static-analysis engine. It flagged a signature-forgery bug that could've cost millions. blog.trailofbits.com/2026/09… @fegge


Another top protocol secured. The vulnerability would have led to loss of over 500k in user funds. The protocol team were swift to respond and deploy the fix. I worked alongside @iitz_ctfguy on this one

vi retweeted

We won RITSEC CTF 2026 as GPT 5.5 Internal Testing
and L3akCTF 2026 as gpt 6.7 internal testing 🔥
Jokes aside, it was actually refreshing to play with humans instead of AI agents for once. Huge thanks to @ritsecclub and @l3akctf for organizing such fun events!


vi retweeted

It's been a year since Plume made the boldest(and wisest) security move a protocol can make:
They handed their entire codebase to hundreds of hackers and said: break it.
$200,000 on the table.
5,708 lines of Solidity.
Four weeks of open season.
The result?
952 submissions.
365 valid vulnerabilities found, reported, and fixed.
Every single one caught by a whitehat instead of exploited by an attacker.
365 real bugs surfaced in one scope.
That is what happens when you stop hoping your code is clean and start stress-testing it at scale.
A 2–5 person private audit cannot match this.


Hello @InverseFinance, I’m reaching out after multiple unsuccessful attempts to contact your team regarding a security vulnerability I discovered in one of your smart contracts. Kindly check your DMs or provide a secure communication channel to discuss this.


