






I asked Opus 5.5 to create a short film on this
xitter.cf/_jiga/status/210617532…

So this is the part I did not expect.
Anthropic called Swami Sarvapriyananda, a Vedanta monk and flew him to the San Francisco head-office.
> Closed door meeting with NDA signed.
> theologians and mental health people in the same sitting, all of it aimed at training Claude.
> and one of the founders stayed in the room the whole time.
----
From 'Ramakrishna Vedanta Society of North Texas" YT channel (full video link in comment)


🤖 Made with AI

We Must Pace the Frontier: I’ve written a new essay on why the AI industry should slow down, with a three-part plan for doing so.
Anthropic is unilaterally committing to the first of these steps. We’ll provide third-party evaluators with permanent, employee-level access to our systems, so that they can verify adherence to our safety measures, report on incidents, and assess models’ alignment during training.
You can read the full post here: darioamodei.com/post/we-must…


What got shipped:
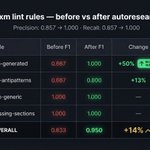
- too_generic_threshold: 100 → 60 chars
- llm_phrase_threshold: 2 → 3 matches
- antipattern_min_strength: 1 → 2 matches
Committed and pushed while I was in morning standup.
Overall F1: 0.8333 → 0.9500. Precision and recall both 1.0.
ctxm is open source: github.com/jiga/ctxm
Autoresearch harness included. Swap in your eval.
30 experiments. $0.15. 12 min.
What system are you pointing this at?

ctxm is open source: github.com/jiga/ctxm
Auto research harness included. Swap in your eval.
30 experiments. $0.15. 12 min.
What system are you pointing this at?
j2p2 🟧 retweeted

Some independent app builders in the Stacks ecosystem were recently targeted via Github in an effort to insert malicious code in their app repositories. We have found no evidence of an attack or compromise of the sBTC or Stacks Core repositories, but because some of these open-source devs also contributed separately to other ecosystem projects (including sBTC), we are taking the opportunity to review security practices around sBTC and Stacks Core and provide more guidance to contributors about their personal and company setups.
Core development (including sBTC) already has extensive security practices in place including least-privilege permissions, branch protections, multi-man rules, MFA, code audits, and more. But as the Stacks ecosystem and sBTC usage grows, attempts on our software development process will become more common. We’re prepared for this increased scrutiny on our Github repositories and continue to strengthen our security practices.
Stacks core devs are working with internal and external security experts to further tighten our software development process. We’ll publish a more detailed analysis of the attempted attack and security measures that helped catch it, along with information on upgraded security processes to help prevent future attacks.
There are no user-facing changes at this time and no steps that users need to take - sBTC and the Stacks network continue to function as normal. Please note that as part of the sBTC development plan, it has filled its 3,000 BTC cap, and withdrawals are not enabled, so it is not currently possible to peg in or peg out of sBTC.
You can always report anything suspicious or find more information on security at stacks.org/security.