




_jamsec retweeted
New Open SSH Vulnerability dlvr.it/T96Gww
_jamsec retweeted

How does a legitimate-looking Google #Chrome update turn into a gateway for #ransomware attacks?
Learn more in our latest post. Research by @_jamsec and @unmaskparasites.
#website-malware #malware #trojans
sucur.it/3Mi5zrI
_jamsec retweeted
🔍 Magecart malware hidden in plain sight?
In our latest post, security analyst @_jamsec reveals how ecommerce malware designed to skim sensitive credit card details from webstores is concealed through pixels and images.
#magecart #malware #magento
sucur.it/3RnRj3Q
_jamsec retweeted
🕵️♂️ What is that, wingdings?!
Attackers are using #unicode and peculiar file extensions to avoid detection in #WordPress backdoors. Research by @_jamsec.
#websitesecurity
sucur.it/3JxxKkT
_jamsec retweeted
🚨 Essential Addons for #Elementor vuln = new #malware taste, classic #Balada flavor. Over 6k detections by SiteCheck already.
Patch ASAP to mitigate risk. Research by @_jamsec & @unmaskparasites.
sucur.it/3IpSieq
_jamsec retweeted

Analysis of the recent massive Balada Injector wave (cdn.scriptsplatform[.]com) that started right after the Essential Addons for Elementor plugin vulnerability disclosure.
blog.sucuri.net/2023/05/vuln…
Had the privilege to contribute to this post with @_jamsec

_jamsec retweeted
🌐 It's raining water company defacements! ⛈️ 💧Our latest blog post explores the strange trend of Belarusian bottled water content appearing on #hacked #websites. Research by @_jamsec.
#defacement #website-security
sucur.it/3pMVeM5
_jamsec retweeted
Double GTM skimmer: urlscan.io/search/#filename%…
GTM-KTGCVGT loads GTM-55SBK75 which loads a skimmer from gojqueryajax[.com/common.css
and previously codesejquery[.com/gtm.js
Related domains urlscan.io/ip/194.4.49.208
jspixjqurey[.com
jspqurey[.com
gojqwejs[.com
Thanks @_jamsec


_jamsec retweeted
The long lasting massive WordPress infection campaign finally gets a name. Meet the Balada Injector and its 9 major approaches to compromising WordPress sites. blog.sucuri.net/2023/04/bala…
Re: xitter.cf/unmaskparasites/status…

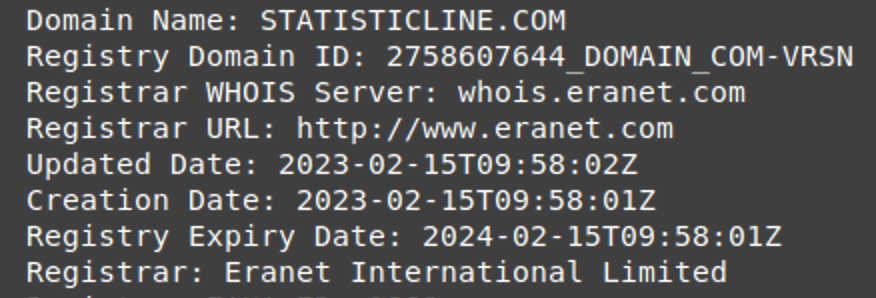
A new wave is coming! countstatisticsbook check.statisticline[.]com/scripts/tap.js
The domain is created on Feb 15 2023
The same IP urlscan.io/ip/194.135.30.210
Re: xitter.cf/unmaskparasites/status…


_jamsec retweeted
🚨 Our 2022 Website Threat Research Report is here! 🚨
Key findings:
- 50.58% of CMS applications outdated at point of infection
- 69.63% of compromised sites had at least 1 backdoor
- 46.76% of all infected sites had SEO spam
sucur.it/3zxX4lq
#WebsiteSecurity #Malware
_jamsec retweeted
Server-side part of the Kritec skimmers found by @_jamsec in vendor/magento/framework/View/Page/Config/Renderer.php
shotsmob[.]sbs in this sample
We also find this malware in WordPress database (theme settings)
Re: malwarebytes.com/blog/threat…


_jamsec retweeted
Found small unwanted ads on your #WordPress website? Might want to check for hex2bin or other encoded #malware #injections in your database. Research by @_jamsec
sucur.it/3moPDty
_jamsec retweeted
Malicious cron jobs can be aggressive. If your site keeps getting reinfected, make sure to check your #hosting control panel or use the crontab -l command.
#malware #infosec #websitesecurity
blog.sucuri.net/2023/02/atta…
_jamsec retweeted
Two weeks after "dns.firstblackphase[.com", we have the "get.sortyellowapples[.com" wave.
urlscan.io/search/#%22sortye…
Infected: index.php, .js files + backdoors
Thanks @_jamsec for spotting it!
Re: xitter.cf/unmaskparasites/status…


When the "violetlovelines[.com" infection count has exceeded 6,000 publicwww.com/websites/%22vi… here comes the "dns.firstblackphase[.com" wave publicwww.com/websites/%22fi… It started after Jan 25, 2023 urlscan.io/search/#%22firstb…
Re: xitter.cf/unmaskparasites/status…


_jamsec retweeted
75+ new #domains pretending to be #URL shorteners are being used to redirect thousands of #hacked sites to fake #crypto Q&A sites and boost #AdSense revenues. By @_jamsec and @unmaskparasites.
#websitesecurity #infosec
sucur.it/3HQ2YC1
_jamsec retweeted
Found the core-stab or task-controller #plugin installed on your #WordPress #website? These are most likely #backdoors that you'll want to remove ASAP.
#websitesecurity #malware
sucur.it/3jvHuCA
_jamsec retweeted
Shady #browser #extensions, stealers downloads from #Discord, unwanted #redirects — thousands of hacked #WordPress sites with track.violetlovelines[.com injection work as a platform for a black hat ad network. Research by @unmaskparasites and @_jamsec.
sucur.it/3wpOJP8
_jamsec retweeted
This new #SocGholish variant loads #malware from a zipped template and encoded #WordPress database record. Research by @_jamsec and @unmaskparasites.
#infosec #websitesecurity
sucur.it/3UV03O5
_jamsec retweeted
@publicww results show nearly 15,000 #websites have been affected by this #Malware. Research by @_jamsec and @unmaskparasites.
#infosec #websitesecurity
sucur.it/3tcTw4L
_jamsec retweeted
When #hackers are able to compromise an environment, they can tamper with important #security controls to evade detection and execute #malicious behavior. Research by @_jamsec
#infosec #NCSAM2022 #websitesecurity #SEO
sucur.it/3SiCIDJ