
Security Researcher
Beijing
Joined December 2015
- Tweets158
- Following75
- Followers1.6K
- Likes2
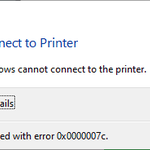



Can't believe that Microsoft not fix Win 10 network printer issue but break Win 11 too. So, is that actually a feature not a bug?

Just found that not publish slides of conference for years, so upload recent ones: github.com/f0rgetting/Presen…
And I will talk at #POC2021 next week, would you join the talk? ^_^

It seems that session pool is removed in WIP. @aionescu @tiraniddo did you have any idea why?
Did you realize that all #printnightmare fix are try to restrict to administrators? It essentially allow UAC bypass. Of course UAC is not a security boundary, so this is not a security issue.
OK, @gentilkiwi found the 3rd one. I have no doubt that he will find the remains soon, just hope that won't be too soon.

But my favorite (for now) #printnightmare dirty trick is: *as a standard user* the way to *force* all other users/admins of workstation/server to install printers😂
rundll32 printui,PrintUIEntry /ga /n"\\print.lab.local\Kiwi Legit Printer"
Rpc(Asyn)cAddPerMachineConnection
Now we got CVE-2021-36958, is it for the not fixed one? or just another one again?

Initial patch analysis show that CVE-2021-34481 only fix @Junior_Baines 's driver install issue, which is not necessary to copy file. Now, 2 of them is public, one is fixed, one not.
Glad to be nominated for @PwnieAwards ^_^

Unfortunately, there is a separate nomination for PrinterNightmare. Perhaps I won't win my pwnie, thanks to @msftsecresponse
Seems that @gentilkiwi found one of them ^_^ xitter.cf/gentilkiwi/status/1415…
@msftsecresponse publish CVE-2021-34481, is that the same as @gentilkiwi 's finding or the second one? 🤔
However, they just pay $5k for #printernightmare , actually it is $0 if I not tweet the demo video. OK, they do not recognize that CVE-2021-1675 is PrinterNightmare, maybe that is why. Well Done! Guess who will report Next Printer Nightmare?

Microsoft Bug Bounty Programs awarded $13.6M to 341 security researchers in the last 12 months. Thank you to everyone for your continued work to help secure millions of customers. msrc-blog.microsoft.com/2021…
@msftsecresponse said that CVE-2021-1675 is just LPE, so maybe this 100% stable RCE as SYSTEM on Domain Controller is another one? 🤔
(7/n) And for now, just set one reg value (NoWarningNoElevationOnInstall) can make it vulnerable again. So, do check if you have this value set.
(8/n) If you like the vulnerability, would you nominate it for a @PwnieAwards ? ^_^ @HaifeiLi @aionescu @tiraniddo @gentilkiwi @mkolsek @wdormann @jonasLyk
My case of #PrintNightmare is closed. And I can't login to MSRC portal because there is no Microsoft account option which I used. Then, how can I report that you not fix CVE-2021-1675 properly (another call is kept vulnerable)? That is your cooperation? @msftsecresponse
Some Clarification: The case closing email is rely to a previous email, not my last report. And there is no response to my last report, so maybe it is lost. This do happen in the past. Unfortunately, I can't login into MSRC portal at the same time. So I can't report it in time.