
Berlin, Deutschland
Joined May 2018
- Tweets31
- Following256
- Followers219
- Likes31
Christian Werling retweeted

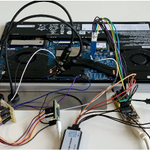
The researchers also say they were able to prove the existence of the "Elon mode" (non restricted, fully self driving) and they were able to turn the mode on. All by a voltage glitch attack on the board with cheap equipment #37c3
Full story in German :spiegel.de/netzwelt/gadgets/…

Christian Werling retweeted
Security researchers say they were able to access restricted parts of the autopilot board in Tesla vehicles, access the neural networks and reverse engineer most of the program. Even recover deleted footage from a Tesla vehicle.
Here is what they told me:
spiegel.de/netzwelt/gadgets/…
Christian Werling retweeted
Drei Berliner Sicherheitsforschern haben mir berichtet, dass sie per Voltage-Glitch Teslas Autopilot-Platine gehackt und den gesperrten Elon-Modus eingeschaltet haben.
Heute stellen Sie beim #37c3 ihre Forschung ausführlich vor, hier eine Übersicht spiegel.de/netzwelt/gadgets/…
Christian Werling retweeted

blackhat.com/us-23/briefings… Why testing fault injection attacks on integrated circuits matters?
⚡️🚗🔐 At BlackHat 23, a research team from @TUBerlin: Christian (@_cwerling), Niclas, Hans and Oleg will show voltage glitch attack against AMD Secure Processor (ASP) used in Tesla cars!
Disk encryption is critical in securing your data when you lose your device or an attacker gets physical access. But we found that if you don't use a BitLocker passphrase on an AMD system (before Windows even comes up), your data is not adequately secured: arxiv.org/abs/2304.14717

Find all code and data to mount the attack here: github.com/PSPReverse/ftpm_a…

Christian Werling retweeted

We built a stealth AirTag clone that is not detected by Apple’s tracking protection. It works by only sending one beacon per generated public key.
positive.security/blog/find-…

Christian Werling retweeted
New blog post: Windows 10 RCE via an argument injection in the ms-officecmd URI handler.
While our RCE vector (MS Teams) has been fixed, the argument injection still persists.
positive.security/blog/ms-of…


Here we go again, #PSPTool 2.3 with several bugfixes and minor improvements is now available 🚂 pypi.org/project/psptool/2.3…

Christian Werling retweeted
Unpatched, critical vulnerabilities in the PlingStore app and Pling-based Linux marketplace websites and patched, lower-severity vulnerabilities in KDE Discover and the Gnome Shell Extensions website
positive.security/blog/hacki…

Christian Werling retweeted

Different port, same exploit: Our research found how a patched vulnerability in ZyXEL NAS devices was still exploitable due to incomplete patching
srlabs.de/bites/zyxel-zero-d…
Christian Werling retweeted
Apple AirTags: Arbitrary data can be uploaded from non-internet-connected devices by sending Find My BLE broadcasts to nearby Apple devices: positive.security/blog/send-…

Christian Werling retweeted

After months of hard work, we're releasing #LibAFL
✔️Scales across cores and machines
✔️Windows, Android, no_std, ...
✔ Different Modes like binary-only Frida mode (120k execs/sec on a phone anyone?)
✔ Easy to extend with grammar fuzzing, etc.
✔️Rust ;)

#libafl is now public! github.com/AFLplusplus/LibAF…
We decided to make it public even without so much documentation so people can start hacking on it.
With @domenuk @srubenst1341 @hackerschoice

Christian Werling retweeted
Insecure URI handling leads to 1-click #RCE in many popular desktop applications: #Telegram #Nextcloud #VLC #LibreOffice #OpenOffice #Bitcoin #Dogecoin #Wireshark #Mumble
Check our post for more details: positive.security/blog/url-o…

Christian Werling retweeted

utk-web now allows for marking #PSP blobs. Click a PSP card to select it! Fun trivia: Even entries from the same "directory" are scattered across a #firmware flash image.
Try it out: hostile.education/utk-web/A3…
#UEFI #AMD #reverseengineering

Christian Werling retweeted
So let's add some JSON output support to #PSPTool for further processing. :)
Thanks a ton @_cwerling for the awesome project! \o/
Christian Werling retweeted

📝 New Blog: "FinSpy Filleted 🐟"
🔬🦠 Dives into FinFisher's (commercial) macOS implant FinSpy: patreon.com/posts/42064704
Builds on @amnesty's writeup (amnesty.org/en/latest/resear…), detailing the malware's
🔓other exploits
⚙️ kernel-mode rootkit
...& more!
H/T @botherder 🙏

Christian Werling retweeted
Over one year we collected Android patch data from phone firmwares. Today we published an analysis detailing patch coverage and time-to-patch for the different vendors: srlabs.de/bites/android-patc… (1/3)
The AMD Secure Processor is a CPU in your CPU you do not control.
It’s a Trusted Execution Environment to protect VMs from host access or copyrighted work from distribution.
At #36c3 I will present our PSP hacking and how we regained control over it.
fahrplan.events.ccc.de/congr…
You can now find a recording of our talk here: media.ccc.de/v/36c3-10942-un…
Code: github.com/PSPReverse
Slides: fahrplan.events.ccc.de/congr…
