

Group CISO @ https://xitter.cf/t.co/mlBb0pUKBI | Engineer & Hacker by heart | Entrepreneur | I enjoy building and breaking stuff 🇲🇦/🇦🇪
Dubai, United Arab Emirates
Joined August 2015
- Tweets1.4K
- Following383
- Followers7.7K
- Likes2.3K





Pinned Tweet
I've just published the slides from my Black Hat talk here: bit.ly/pwning-cloud-bhmea23
Thank you to everyone who attended; I hope you enjoyed it!

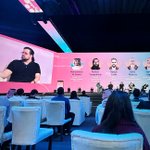
🎥 I had an amazing time on a panel discussion at Black Hat MEA with cybersecurity leaders and CISOs I admire and continue to learn from.
The recording is now available on YouTube, go check it out: youtube.com/watch?v=h1Xpf4VL…
Ayoub FATHI 阿尤布 retweeted

Congratulations on your inclusion in the #ModernCISONetwork Board Book, @_ayoubfathi_! 🎉🎉


Ayoub FATHI 阿尤布 retweeted

📣 May in metal health awareness month and I think it's time for us to talk about it.
Watch: youtu.be/-ljLIf-Pxl0
Donate: supporting.afsp.org/index.cf…

Ayoub FATHI 阿尤布 retweeted

🌟 Brace yourselves for an electrifying revelation from @_ayoubfathi_ , Group Vice President of Information Security, CISO at @noon, as he takes the stage for his closing keynote address! 🚀
You can watch his talk streaming on YouTube.
youtu.be/fjX5u4jxW0E?feature…
#bsidesahmedabad #cloud #ciso #hacking #infosec #security #lateralmovement #bruteforce
When I delivered the closing keynote @bsidesahmedabad, many folks were curious to learn more about lateral movement brute-forcing. So the talk recording is finally live on YouTube, go watch it at the link below.
I had a lot of fun sharing the hacking stories. I hope you enjoy it too!

🌟 Brace yourselves for an electrifying revelation from @_ayoubfathi_ , Group Vice President of Information Security, CISO at @noon, as he takes the stage for his closing keynote address! 🚀
You can watch his talk streaming on YouTube.
youtu.be/fjX5u4jxW0E?feature…
#bsidesahmedabad #cloud #ciso #hacking #infosec #security #lateralmovement #bruteforce
I had a lot of fun listening to @infosec_au story and what I enjoyed the most is that it covers a lot of what bugbounty truly was all about back in the day and that everyone including some of best (eg. shubs) were really trying to be resourceful but also working hard to figure this BB thing out, a must watch!

LEAP has wrapped up!
The buzz and scale were incredible, with over 215,000 attendees! 🎉
But making a ton of new friends and meeting so many incredibly talented people was absolutely my highlight of #Leap24
Thanks to everyone who dropped by our chat, see you next!


1
12
1,880
I'm not sure if that was the reason (but I believe so) — HackerOne has introduced a new CWE type as a result of/right after this was triaged: "Uncontrolled Resource Consumption"
which was used by the program later on.
Reasoning: This doesn't fall under typical DoS attacks, which are usually OOS so they had to introduce a new category to accommodate such valid cases.

python-multipart (which is also used by FastAPI and Starlette in form requests) is vulnerable to ReDos: github.com/Kludex/python-mul…
1. Find requests that use `application/x-www-form-urlencoded` as a Content-type (basically many form requests)
or if you're code reviewing, you may want to look for: ` = Form(`
2. Append to the content type: !=\"\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\ (... lots of backslashes)
3. Report and profit.
Note that you need to take a lot of caution while testing this and ensure you do it in a controlled manner, otherwise, you may slow/take down production applications.

In a week, I'll take the stage at LEAP, this time wearing my CISO/executive hat (yet the hacker/engineer spirit remains strong within me).
I wouldn't have believed it a decade ago if someone said I'd be speaking alongside such a lineup of world-class speakers and over +170,000 attendees.
I'm deeply grateful for the vibrant region/environment we are in, not only a place where one can exercise their technical and entrepreneurial muscles but also make long-lasting connections and meet incredibly talented people. It took a solid decade, but it was worth it.
If you're in Riyadh, let's connect!
Stay tuned! onegiantleap.com/speakers/ay…

Today was another reminder - I have never been more humbled than when I meet a homeless family (parents with kids),
no one should write off that possibility no matter where you are in life, you could be on top of the world but a couple of misfortunes lined up could turn things upside down.
We focus too much on what’s lacking that we forget what we have, we forget that some people don’t even have a roof to cover them or haven’t eaten for days, always be grateful.
watching myself go from
97kg -> 80kg -> 90kg -> 85kg -> ..
I trained, CrossFit, Muay Thai, weightlifting, ..etc.
all in <12 months, then suddenly obsessing over health/sleep/HRV data, biohacking, #blueprint/etc, is something my body still couldn't comprehend for someone who had a sedentary lifestyle at best for most of his life.

5
1,281
~2h, why not 🤷♂️

python-multipart (which is also used by FastAPI and Starlette in form requests) is vulnerable to ReDos: github.com/Kludex/python-mul…
1. Find requests that use `application/x-www-form-urlencoded` as a Content-type (basically many form requests)
or if you're code reviewing, you may want to look for: ` = Form(`
2. Append to the content type: !=\"\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\ (... lots of backslashes)
3. Report and profit.
Note that you need to take a lot of caution while testing this and ensure you do it in a controlled manner, otherwise, you may slow/take down production applications.
python-multipart (which is also used by FastAPI and Starlette in form requests) is vulnerable to ReDos: github.com/Kludex/python-mul…
1. Find requests that use `application/x-www-form-urlencoded` as a Content-type (basically many form requests)
or if you're code reviewing, you may want to look for: ` = Form(`
2. Append to the content type: !=\"\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\\ (... lots of backslashes)
3. Report and profit.
Note that you need to take a lot of caution while testing this and ensure you do it in a controlled manner, otherwise, you may slow/take down production applications.
Ayoub FATHI 阿尤布 retweeted

Oneliner + A collection of special paths linked to major web frameworks and infrastructure projects, known juicy APIs, misconfigurations.. etc.
dirsearch -l 200HTTP --full-url -F -w leaky-paths.txt
- github.com/ayoubfathi/leaky-…
#infosec #cybersec #bugboutnty
What a week it has been at @Blackhatmea in Riyadh!
Delivered a talk (I'll publish the slides shortly!), joined panels, and had dinners with some incredible people & many of the Fortune100 CISOs. We also had a lot of fun touring Riyadh, sharing stories, and having a few laughs.
I can't wait to meet everyone again next year!

