


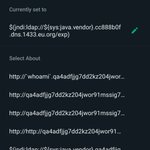
Thousands of Blinkit invoices are getting leaked in public😂, surely it not in @zomato 's hand but ,it can be mitigated if zomato wants to,
On scribd.com search for "ForwardInvoice" you will be greeted with thousands of invoices and it is accepted risk by zomato
1/2

Sam retweeted

I recently developed and posted about a technique called "First sequence sync", expanding @albinowax's single packet attack.
This technique allowed me to send 10,000 requests in 166ms, which breaks the packet size limitation of the single packet attack.
flatt.tech/research/posts/be…

Emails from @immunefi are leet😵💫, the severity just got updated by the program to Critical 😵💫, awesome work tho !
#BugBounty

Hats off to the @immunefi for the best mediation out there ! I really appreciate it !
#BugBounty

Multiple logical errors to parental bypass in Apple music : medium.com/@sam0-0/multiple-…
#bugbounty #apple #infosec #scam #bugbountywriteup

Sam retweeted

I just published 'Hacking Anything LLM via Reversing CVEs (Duplicates)'
basu-banakar.medium.com/hack…
#BugBounty #bugbountytips #bugbountytip #LLMs #reversing


New writeup : BYPASSING PAYMENTS IN APPLE FOR FREE TRAILS FOR LIFETIME medium.com/@sam0-0/bypassing…
#bugbounty #Apple #AppleMusic #infosec #poc
Here's a new write up for testing Hls streams:
medium.com/@sam0-0/hunting-b…
#BugBounty #infosec #bugbountytip

New Bug/Feature (😂) in Twitter, the views counter in every tweet is working suspicious, if you view the same tweet for 100 times you will get 100 views on it, so if you repeat same request then you can get unlimited views on the tweet 😂,
1/2..
#infosec #BugBounty #twitter
4
6
1,059
Now, just make demo account view your tweet, capture traffic and simply repeat the request for 10000's of times to get 10000's of views ok your tweet 😁😂 it's a feature 😂
2/2..
#infosec #BugBounty #twitter
1
2
822
Here's the documentation : help.twitter.com/en/using-tw…
Even if you view your tweet few times it will increase the view count too😂 just start your turbo intruders 😂and enjoy the views 😂
2
696
Sam retweeted
Turning Google smart speakers into wiretaps for $100k downrightnifty.me/blog/2022/…
Sam retweeted

⚡Breaking into iPhone's last Security Barrier
📱Tihmstar @tihmstar presented his work on attacking the iPhone's hardware AES crypto core through an EM-side-channel in order to retrieve the hardware fused GID & UID keys
🍿Enjoy the talk▶️youtu.be/s_cnjOCegs0
#hw_ioNL2022
Sam retweeted

😊🙏🏻 Grateful to hit this Chrome VRP milestone a year earlier than I expected! Hope this is the start of a streak on the @GoogleVRP.

ALT Email from Chrome VRP manager with subject line: "Congratulations, you're a 2022 top Chrome VRP Researcher!" and body: "Hello and Congratulations! If you are receiving this email, you are one of the top Chrome VRP Researchers for 2022."
Sam retweeted
A large part of this is thanks to collabs. Big thank you to @__Sam0_0 who helped discover my most impactful bug of this year. Also thankful to more researchers who are collaborating with me on undisclosed bugs!
xitter.cf/AlesandroOrtizR/status…

This was initially found by @__Sam0_0 using my PoC for CVE-2020-6506. Really appreciate their work here!
Sam retweeted

Very cool series on IoT devices reverse engineering by @apps3c
A lot to learn!
Part 1: buff.ly/3CzUcqF
Part 2: buff.ly/3C7WPyn
Part 3: buff.ly/3M85jKh
#iot #xiot #embedded #Linux #reverseengineering #infotech #cybersecurity #informationsecurity


Sam retweeted

Recently was told that there were some large discrepancies between my Fuzzing101 with LibAFL blog/code and LibAFL's current API. So, I took some time this weekend to update the blogs and the repo to use LibAFL v0.8.1🎉
CC: @aflplusplus
epi052.gitlab.io/notes-to-se…