


Ex Milo retweeted

Not even a SOL maxi can be this retarded and not buy $HYPE on discount
When the CEO of ICE literally said this on the earnings call two days ago:
Ex Milo retweeted

Binance has allocated US$6.34 billion of its own corporate funds to the User Fund. In the current User Fund, BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, and ZEC have all achieved 100% full reserve backing. We will continue to purchase other altcoin assets that are not yet 100% matched through market and over-the-counter (OTC) channels until the replenishment ratio for all tokens reaches 100%.
We completed a new Proof of Reserves snapshot at 08:00 (UTC+8) on October 31, 2026, and have updated it on the Proof of Reserves website. This snapshot presents the latest fully verified asset position and is part of our ongoing commitment to transparency. Because generating zero-knowledge proofs requires substantial computing resources, it is expected to take approximately 40 to 50 hours. If you hold any of the aforementioned ten tokens, you can independently verify, once the complete proof is generated, that your assets are backed by at least 1:1 full reserves. The complete proof is expected to be published on Tuesday, November 3, 2026 (UTC).

Ex Milo retweeted

ICE and Trade[XYZ] plan to bring Hyperliquid-based perps to the U.S.
Subject to regulatory approvals, ICE will operate U.S. regulated versions of Trade[XYZ]’s markets, leveraging their expertise as the leading deployer of real-world-asset perps on Hyperliquid.
The new venue will operate separately to ICE’s institutional futures franchise and offer a trading experience designed for retail participation.
Once live, U.S. traders will be able to trade 24/7 across a range of assets spanning the macro complex including:
*Crypto
*Equities
*Indices
*Commodities
*Forex
Read more: spr.ly/6010BHq9X8
Users will access the platform through U.S.-regulated FCMs performing KYC/AML screening, including ICE's joint venture with OKX.
ICE and Trade[XYZ] will seek approvals to launch a new market built on Hyperliquid to operate KYC-compliant perp markets, including regulatory approvals to support leveraged trading.


Regulators are embracing the technology and calling for a common legal framework to prevent market practices and infrastructure choices from becoming entrenched elsewhere.
Meanwhile, certain market participants seem more interested in protecting the status quo.


Ex Milo retweeted

Payward, the parent company of Kraken, announced its intention to be the first CFTC-regulated deployer on HIP-3* markets. Payward will use Hyperliquid as the infrastructure layer to deploy perpetual futures markets for US clients. Subject to regulatory approval, Bitnomial, Payward’s CFTC-regulated DCM and DCO, would act as the HIP-3* deployer: creating, owning, and administering the markets and clearing and settling the contracts. If approved, NinjaTrader Clearing, Payward’s CFTC-registered FCM, would carry client accounts.
HIP-3 will support optional deployer configuration for permissioned markets in a future network upgrade. This set of additional deployer functionality is collectively called HIP-3*. At its core, HIP-3* activation involves an onchain allowlist managed by the deployer or its sub-deployers. The functionality is strictly additive to HIP-3; its use is optional and up to the deployer. Existing markets remain unchanged. The initial release is available on testnet, where specifications are preliminary and subject to change based on feedback.
Hyperliquid is a neutral infrastructure layer with the goal of supporting large parts of the financial system. HIP-3* gives deployers additional functionality to operate deployments consistent with the requirements applicable to them. As with HIP-3, HIP-3* deployers are independent operators who use Hyperliquid as the onchain infrastructure layer for their own markets, while retaining control and responsibility over their deployment.


Ex Milo retweeted

NEW ODD LOTS:
It’s the podcast debut for Jeff Yan
@tracyalloway and I have an ultra-rare interview with the CEO and co-founder of Hyperliquid Labs about his plan to house the world’s entire financial system
open.spotify.com/episode/5Aq…

Ex Milo retweeted

I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices.
(and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation)
So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.
The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be?
This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-.
For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption.
And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10.
To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety.
And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all.
Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems.
For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size).
Concrete TLDR, my own personal views:
* Hash-based > lattice-based, in those situations where hash-based is possible at all
* For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ...
* For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism.
* If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**.
* For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money"
firefly.social/post/x/210783…

Ex Milo retweeted

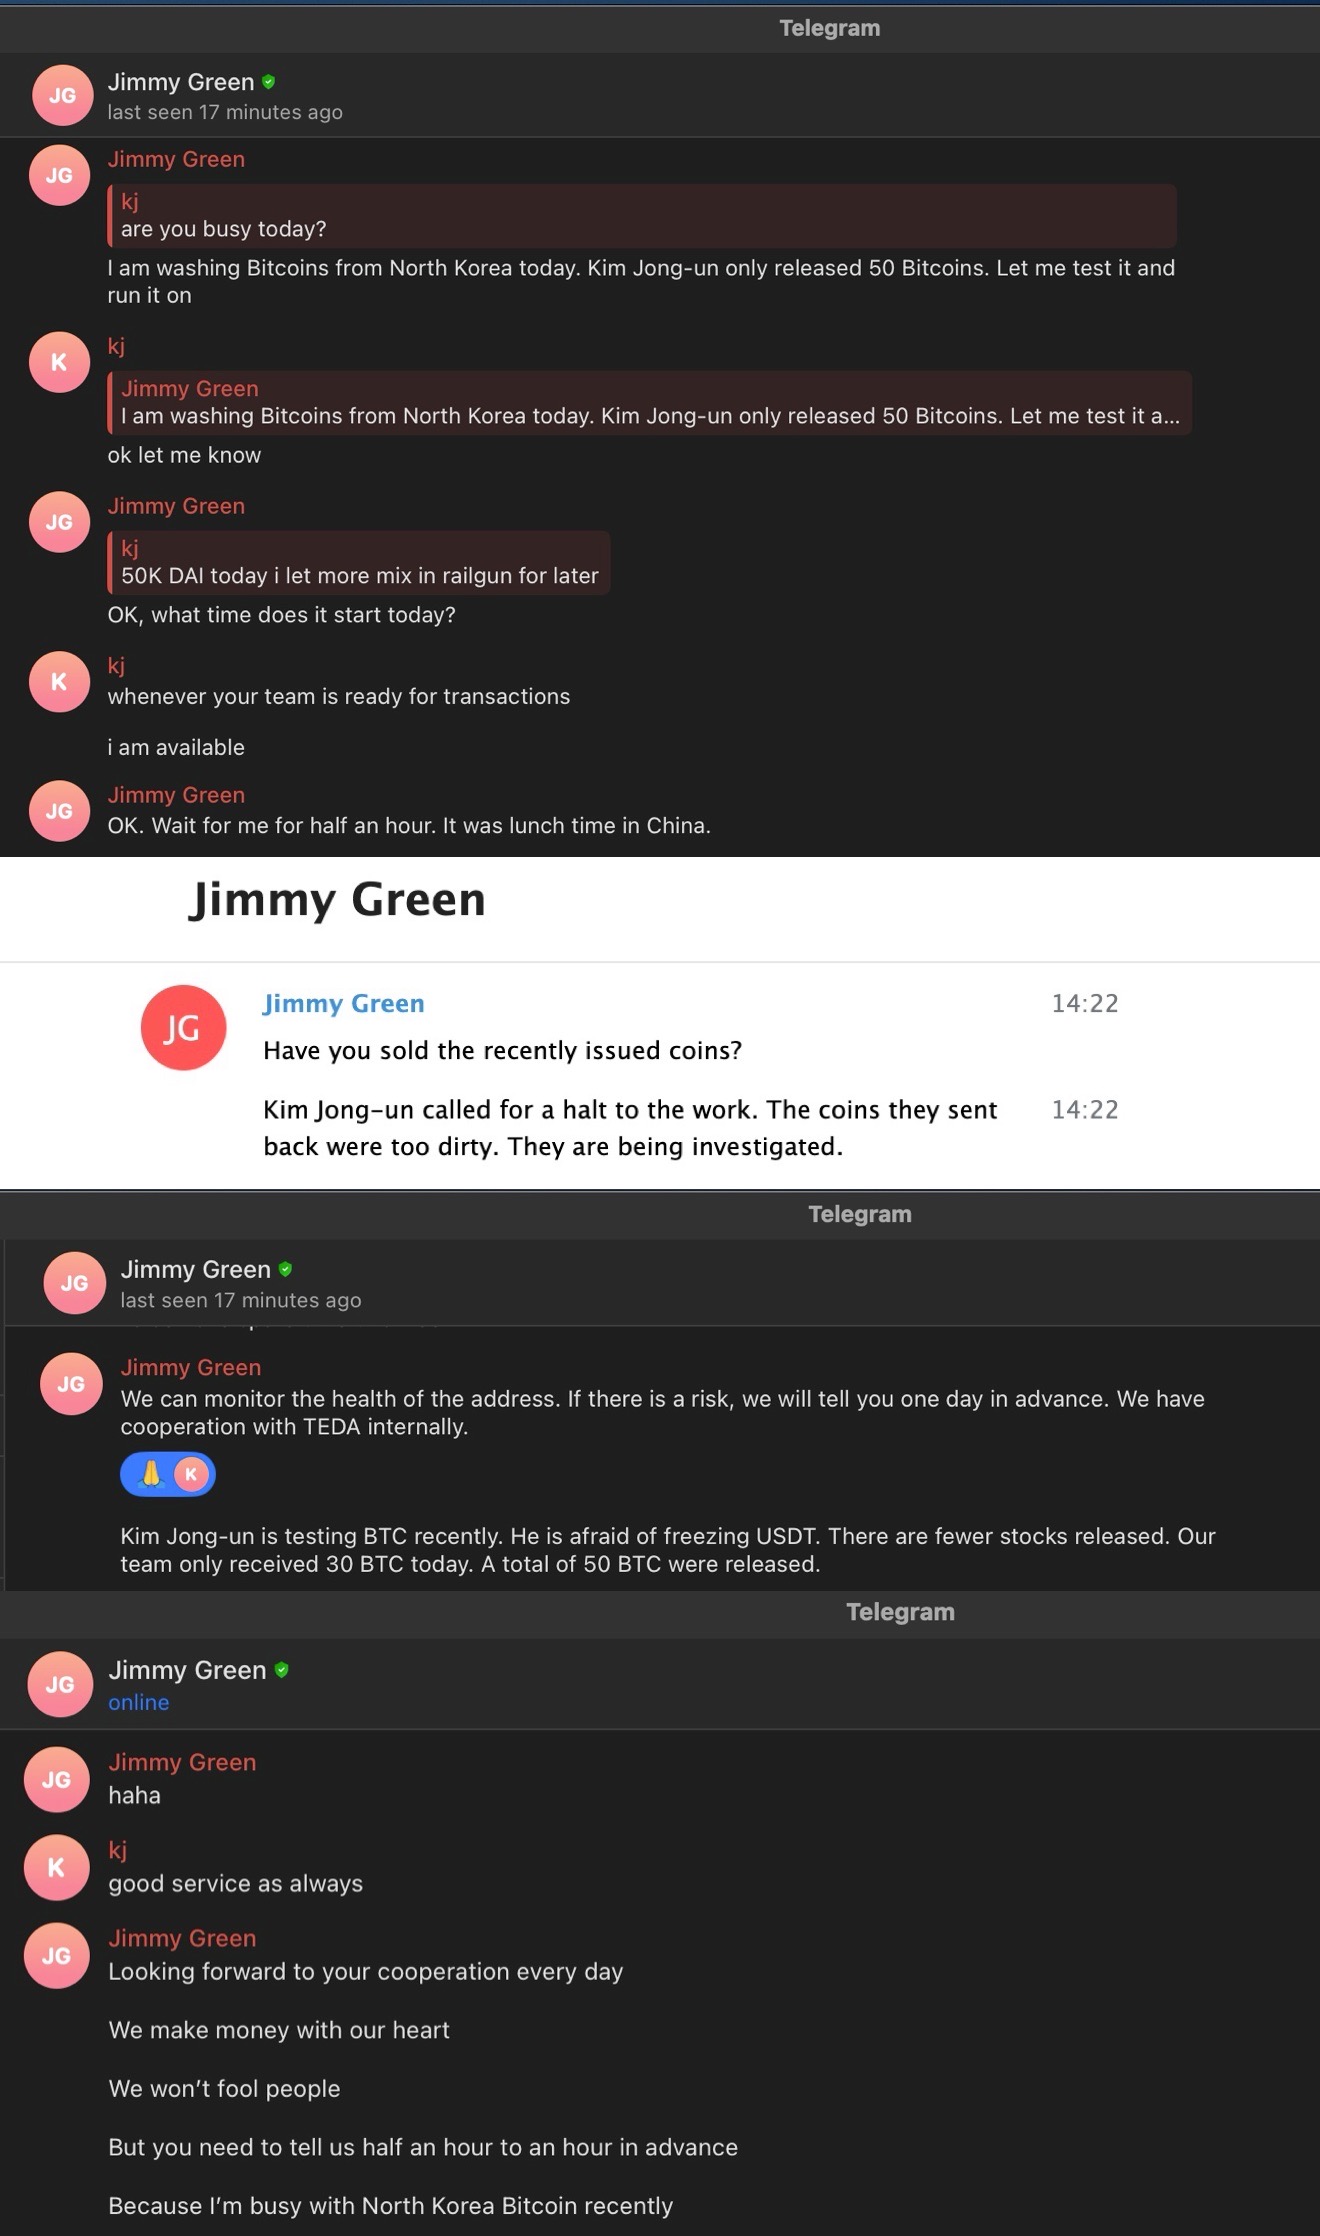
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

Ex Milo retweeted
After months of research, we have published the most comprehensive report on tokenised equities, indexing over 1.5m addresses across five issuers on four chains.
arrakis.finance/tokenized-eq…
In this report, you will learn who is actually buying tokenised equities, how fast this market is growing, what the latest innovations are, and projections for what's ahead in 2027.
Ex Milo retweeted

If I shield ZEC, what can I do with it?
Answer: Hold it or transfer it, right?
To do any DeFi with it, I have to unshield it?
So to swap in/out, I give up privacy first?
I guess I could shield ZEC, transfer to other shielded addresses, then unshield later to store/spend/use it.
But most CEXs only accept unshielded ZEC?
So if I buy ZEC on a CEX, it has to be transparent ZEC and if I withdraw/send that ZEC to a wallet, the CEX has me now linked.
In order to spend ZEC, practically speaking, then I have to unshield it, because very few, if anyone, accepts shielded ZEC?
Ofc, I could pay someone else with a shielded address, if I can track someone down willing to accept shielded ZEC.
All this to say, I can store value indefinitely in shielded ZEC and potentially transfer/pay it to other wallets, but the path post-buying ZEC, and prior to shielding ZEC, is likely doxxed onchain through an exchange relationship.
So I can't buy/acquire ZEC, without exposing myself.
And I can't use ZEC as money, without unshielding it?
But it is money? Superior private money?
Just money I can't use?
Ex Milo retweeted
Yesterday, HPC responded to @EU_Finance’s review of MiCA, our first filing outside the U.S., urging the Commission to build on existing EU rules for onchain markets.
The EU wrote the first rulebook for crypto-asset markets. Its review now asks which rulebook governs perpetual futures, one of the most traded derivative products in the world.
Our position: perpetual futures belong under MiFID II, the EU’s framework for derivatives, regardless of how they are recorded or what asset class they reference. Applying MiFID II with attention to how onchain markets work will give EU investors access to regulated markets that are deeper, continuously margined, and verifiable by anyone.
Read it here:


Ex Milo retweeted
BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379


Ex Milo retweeted

The @bitget exploiter tried to move the stolen funds through @Chainflip.
Chainflip’s response?
“Deposit rejected by the broker.” 👋
No freeze, but no luck either — the funds were refunded. 👍
Nice try. 😶
We’ll continue tracking the movement of the stolen funds.
🔗 scan.chainflip.io/channels/1…


Ex Milo retweeted

tldr - Bitget hackers tried to move >$50M through NEAR Intents and the NEAR Intents team swiftly coordinated to stop $49.83M from being laundered by the hackers.
NEAR Intents is not for unlawful actors. Accelerate.

The $S3 posts are getting so fucking annoying. They either forgot to sign the T&Cs, jeeted their airdrop at $3, or are stuck in the $PURR meme trade.
What have you guys been smoking to think it’s a good idea to dilute $HYPE holders?
Milo big ungry

Everyone that jeeted their $Hype airdrop or forgot to sign the t&c coming up with reasons why Jeff should give them more free money.
Ex Milo retweeted

when thorchain got drained in 2021, the network halted within hours. when thorfi went underwater in jan 2025, nodes voted to freeze withdrawals overnight.
"decentralized and permissionless" seems to apply only when it's other people's money.
a sanctioned state already used you to move over $1b from bybit. at some point regulators won't care what you call yourself.

We are devasted to hear about the recent exploit and can imagine how difficult this must be for everyone involved.
THORChain is decentralized and permissionless like Bitcoin, Ethereum, and BNB Chain.
What responsibility should Bitcoin, Ethereum, and BNB Chain bear when handling known stolen funds?
@star_okx @GracyBitget