

WATCHPUG is a security team that offers in-depth auditing for Solidity smart contracts.
EVM
Joined May 2021
- Tweets53
- Following204
- Followers2.2K
- Likes25
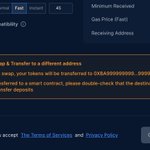


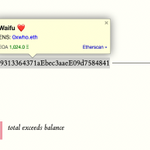




a frontend hijacking attack on Convex
this is exactly why the wallet should display a human-readable ENS name for the smart contract address they are interacting with;
and the reason I added this feature to @TallyCash 3 months ago: github.com/tallycash/extensi…


0xWho is an open-sourced Chrome extension: github.com/jack-the-pug/0xwh…


WATCHPUG retweeted
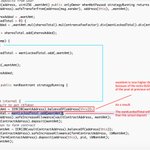
This happened in etherscan.io/tx/0x9582362669…: the problem was them rolling a vulnerable LP token price oracle (sers, we have the correct one also!).
Conclusion: if ever in the future you feel like rolling your price oracle for our pools - ask us to check please


.@InverseFinance now believes the crv3c is worth much more than it's actual value, so the attacker can borrow out 10m DOLA with only $4.7m worth of collateral.
that's ~$5m of bad debt to the protocol.
currently building a chrome ext which will show you a tooltip with a human readable name (from your address book) whenever you select an address.
it supports ENS reverse resolution; tells if it's a contract or EOA, + the ether balance.
this chrome ext is gonna be called: 0xWho?

WATCHPUG retweeted
We are honored to introduce the new ReportingDAO member, .@WatchPug_, a team of web3 security professionals!
In combination with WATHPUG, InsureDAO will be able to elevate security, privacy, and usability even more!!
link.medium.com/VpyPPrsUBnb
#InsureDAO #DeFi


⚠️ Oct 20, 9 AM UTC, an attacker exploited PancakeHunny and stole 2.3M
The root cause: inappropriate usage of a low liquidity pool makes it vulnerable to price manipulation to create artificial profits
Read more: watchpug.medium.com/pancakeh…
WATCHPUG is proud to have received a quarter million ($250K) bug bounty award from @PancakeBunnyFin for a critical bug in the Zap function.
Thank you! @PancakeBunnyFin @immunefi


At 2 AM UTC on Aug 4, @Wault_Finance‘s WUSD on BSC was exploited and drained $800k (370 ETH) out of the WUSD/BUSD LP.
WUSD is a stable coin backed by USDT and WEX.
We believe it's an economic attack rooted in the design of WUSD.
Read our analysis: watchpug.medium.com/wault-wu…

WATCHPUG retweeted

Today, we want to share with you couple repos that will help you master blockchain pentesting and smart contract dev.
github.com/bkrem/awesome-sol… - Contains a huge amount of information, updated regularly
github.com/openblocksec/bloc… - All known blockchain incidents, updated regularly
