

I LOVE CHINA 🇨🇳 #SecurityResearch Blog: https://xitter.cf/t.co/lMvHRGPcLJ
Joined September 2021
- Tweets731
- Following489
- Followers5.9K
- Likes1.3K





严肃玩Tibo


Day 28/ tibo's game has landed
i spent $5.99 on this domain, but i had a blast making it with grok bot and cursor! i hope you enjoy it and find all the easter eggs 🤍
if i did it right you should be able to play it inside of X too
tibo.dog

2
611
key retweeted

I have developed an #IDAPro version of the #CyberChef plugin, #IDAChef—time to explore using it.
github.com/ExpOrx/IDAChef.gi…




key retweeted

Guys, I built a super fast Android decompiler called ASC.
It completely replaced Jadx MCP for me and lets me analyze 10+ APKs in parallel.
And this week my Agent use ASC found 2 RCE in Honor and Xiaomi!
This tool now accepted by BlackHat EU Arsenal
github.com/MG1937
#BHEU

key retweeted

Lody 开源了!
我们通过 @loro_dev 第一天就构建了面向团队的、本地优先的 workspace,coding agent 的控制面是我们的第一步。我们真正要解决的是团队数据 context 的共享,通过 agent 帮助团队和个人真的理解 context。
AI 已经能够帮助我们完成大大小心的任务,沉淀各类文档,但还无法让我们真的理解它做了什么,团队其他人做了什么。只有理解了才有掌控感,这就是 Lody 想去完成的,我们通过本地优先让你掌控了自己的数据,我们进一步希望通过 Lody 让你掌控自己的作品。
我们开源了客户端和 CLI 端,更多的更新和博客会逐步开放!如果你对我们做的事情感兴趣,欢迎 star,保持关注!
github.com/LodyAI/Lody


Lody is a shared workspace for the coding agents your team already uses.
The CLI and local desktop are now open source!
lody.ai/blog/lody-is-now-ope…

AI 自动化渗透平台跑完一轮,最难交代的就是证据。真去旁路挂一套 Burp 抓流量再截图,部署和维护都太重,有人会想干脆拿 HTML 照着 BurpSuite 的样子画一个假的界面,但是这样始终不真实。amber 把流量直接固化成真正的 .burp 项目文件,字节级读写,生成过程不需要 Burp,也不需要 JVM,旁路抓的 pcap 也能一键转成项目。拿到项目文件,用 Burp 打开就能一步步复现请求和响应,方便截图。

让AI搓了一个项目,用于解析BurpSuite项目文件的HTTP History,并且支持创建空的项目文件写入HTTP History信息。
github.com/overspace-labs/am…

让AI搓了一个项目,用于解析BurpSuite项目文件的HTTP History,并且支持创建空的项目文件写入HTTP History信息。
github.com/overspace-labs/am…
HaEFile 1.0.3 版本发布,增加结果导出功能,导出结果为JSON文件(需求建议来自:冰淇霖 & 地图大师)。
github.com/overspace-labs/Ha…


key retweeted

hhh,fastjson终究还是顶不住压力了啊,推出了最最最后一版1.2.84 🤪github.com/alibaba/fastjson/…


是的,我被 @xishan12509850 蒸馏了。他把我平时做事、想问题、给建议的那一套方法,尽量“塞”进 AI 里,做成一个像我的 Skill。蒸馏的重点不是把我写过的文章、做过的项目全扔进去,让 AI 背资料,而是想办法把我平时怎么判断、先看什么、什么值得继续搞、什么情况直接算了,这些更核心的东西提出来。
文章地址:mp.weixin.qq.com/s/wRjq9PfSn…

重要通知:鉴于当前项目结构较为复杂,为提升整体维护效率并便于下游仓库使用,HCM 三个项目已由个人作者仓库 gh0stkey 迁移至开源团队组织仓库 overspace-labs。
HaE项目地址:github.com/overspace-labs/Ha…
- HaENet版本源码(BurpSuite):github.com/overspace-labs/Ha…
- HaEFile版本源码(VSCode):github.com/overspace-labs/Ha…
CaA项目地址:github.com/overspace-labs/Ca…
MaR项目地址:github.com/overspace-labs/Ma…
HaENet在线视频教学:bilibili.com/video/BV1Xy421B…
HaEFile在线视频教学:bilibili.com/video/BV1ttTE6H…
CaA在线视频教学:bilibili.com/video/BV1F8WzeF…
MaR在线视频教学:bilibili.com/video/BV1JyqHBp…

做了一个视频介绍我和 @0chencc 开发的新项目,AI给取的标题名是《开发阶段就发现安全风险:我们做了一个 VS Code 扫描插件》。实际上,也是我想表达的,HaE项目不仅可以为网络安全从业人员服务,也可以为广大的开发这服务!
HaE File使用讲解来了!欢迎大家一键三连!
bilibili.com/video/BV1ttTE6H…

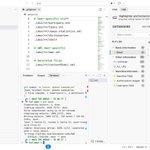
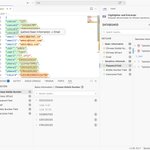
HaE File — A VSCode extension that auto-highlights and extracts sensitive data from local files via regex matching.
Built on ripgrep, it scans files/folders/workspaces at lightning speed, highlights matches in real-time with multi-color coding, and centralizes results in a Databoard panel — making it a must-have for bug bounty hunters, pentesters, and security researchers who sift through logs, configs, and source code.
github.com/gh0stkey/HaE
#bugbounty #infosec #securitytools #vscode #pentesting #recon #HaE

key retweeted
HaE File — A VSCode extension that auto-highlights and extracts sensitive data from local files via regex matching.
Built on ripgrep, it scans files/folders/workspaces at lightning speed, highlights matches in real-time with multi-color coding, and centralizes results in a Databoard panel — making it a must-have for bug bounty hunters, pentesters, and security researchers who sift through logs, configs, and source code.
github.com/gh0stkey/HaE
#bugbounty #infosec #securitytools #vscode #pentesting #recon #HaE
HaE File — A VSCode extension that auto-highlights and extracts sensitive data from local files via regex matching.
Built on ripgrep, it scans files/folders/workspaces at lightning speed, highlights matches in real-time with multi-color coding, and centralizes results in a Databoard panel — making it a must-have for bug bounty hunters, pentesters, and security researchers who sift through logs, configs, and source code.
github.com/gh0stkey/HaE
#bugbounty #infosec #securitytools #vscode #pentesting #recon #HaE