

Doing fun stuff at @reversinglabs now. Reverse Engineer. Former CTO @avtestorg
Germany
Joined April 2009
- Tweets1.3K
- Following955
- Followers739
- Likes6.2K
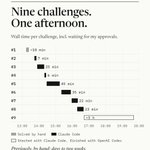




Flare-On used to take me several days. This year it took an afternoon.
Challenge 1 I solved by hand, the other eight with Claude Code running Claude Opus 5.5 and one with ChatGPT Sol 5.6 when Opus was stuck. What I took away:
1. No special harness. A short CLAUDE.md with my preferred tools and how to drive them was enough, with GhidraSQL as the workhorse. The capable model did the rest.
2. The instructions grew with the run. After each challenge, the lessons went back into CLAUDE.md. One example: use the real reverse engineering tools instead of rebuilding them in Python, which the model likes to do. Another: log dead ends too, because those are the expensive part.
3. Refusals happened. On two challenges Opus 5.5 refused to continue. I finished one with Sonnet 5, the other with Opus 5 and then 4.8.
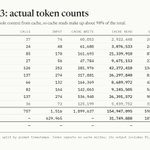
4. So did getting stuck. Twice Opus 5.5 hit a wall. Once a hint from me was enough. The other time I switched to ChatGPT Sol 5.6, which burned a full day's token allowance but solved it. The remaining seven took about 1.5 days' worth of Opus token limits, typically 8–9% of a 5-hour usage window per challenge and around 25% for the hard ones.
5. The expensive mistakes weren't reasoning errors. They came from tool choice and missing folklore. An hour went into a full auto-analysis of a huge binary, and 25 minutes passed before the agent tried a password every CTF player tries first. Experience still mattered, just after the fact, as rules in the instructions.
6. The agent took a convincing decoy at face value. Only submitting the flag exposed it. Without external validation, nobody would have noticed.
7. It fetched its own tools, within bounds. When a format wasn't supported, it proposed a Ghidra plugin and rebuilt it in about five minutes, asking first as instructed. Apart from two cases I explicitly approved, it never ran challenge code on my host: static analysis and emulation only.
8. Days became hours. What used to take me days, sometimes one or two weeks, took 3–4 hours, with very little interaction.
9. My knowledge wasn't really needed. The agents solved the challenges autonomously. I learned little about the underlying reverse engineering this time. What really counted: what to put in the instructions, when to step in, when to switch models.
If you want to learn from an agent's work, make it document its findings and its approach, including the dead ends. Otherwise the knowledge disappears with the context window.
That leaves the big open question: what do we as humans still need to know and take away, and what do we leave entirely to the AI?
#FlareOn #ReverseEngineering #AI #Cybersecurity


Maik Morgenstern retweeted
Shai-Hulud is back. 🪱
A massive software supply chain attack just tore through npm: 2K packages compromised with hundreds of millions of combined downloads.
🚨 Notable victims include flat-cache, file-entry-cache and packages under namespaces [@]workbench-stack and [@]adminide-stack.
Malware records from RL's secure.software:
secure.software/npm/packages…
secure.software/npm/packages…
secure.software/npm/packages…
secure.software/npm/packages…
Full research/analysis to come...
My team published new research. Check it out! – at Hohendodeleben, Deutschland

🚨 NEW from ReversingLabs: Copy, Paste, Compromise: The Tale of ClickFix
Full #ClickFix attack chain research + an open-source #YARA rule validated against 4K+ samples — incl. 123 lures that evaded every #Antivirus engine.
Detect the lure before the user acts: hubs.ly/Q04ps-7p0

Challenge accepted. Challenge completed. 💪 #FlareOn12
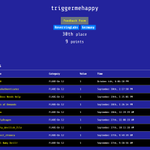
The last one, #9 was brutal, but I made it — 30th out of 2,500+ players! Proud to have represented @ReversingLabs for the first time and placed it high on the scoreboard.
Thanks @Mandiant & @googlecloud for Flare-On 12!

Maik Morgenstern retweeted

#flareon12 is coming in hot and fast this year and will only run for 4 weeks this year instead of the usual 6. Don't miss it! flare-on.com


2 weeks ago I posted the first statistics for #flareon11 Went from 2462 participants who solved Ch1 to 3652 and from 3 finishers to 64!
Challenge 2 is still the first tough test for many, only 43% of Ch1 solvers managed to do it. Followed by 5, 7 and of course the special ch9.

And done, achieved my goal for this year: Top 100!
Lost so much time on 9, I was on the right way, but took a wrong turn and went deep down the rabbit hole.
10 was a nice final challenge! Special mentions for 5 and 7.
Learned a lot and had lots of fun!
#flareon11

OMG, Ch7 was cruel and Ch8 was all new stuff for me, but at least faster to solve ... Seeing the flag was extremely rewarding for both though! Only 2 more to go now #flareon11

The current #flareon11 scoreboard stats while I despair over challenge 7.
2462 people managed to complete the 1st challenge. The 2nd challenge already left 1500 people behind. Ch 5 was the next big test, stopping 400 ppl for now. And now Ch 7 is the next roadblock.

Finished the first 5 challenges of #flareon11 and feeling already tired :D

Excellent summary. I always think back to that SOC manager who I asked what they look for in sandbox reports: "The overall score. We just want to know whether it is malware or not!"
It's the sad truth 😐😐😐

Doing a bit of vulnerability research and found this gem ... that is a good way to protect secrets such as API keys 😀

What a fantastic day! Exciting talks in the morning during our AV-TEST Security Summit and then the most amazing AV-TEST Awards ever. Thank you for making this day a success and for being part of 20 years of AV-TEST!

Congratulations to all winners of this year's @avtestorg Awards and many thanks to all our speakers at the AV-#Security #summit, as well as our guests, partners & friends and the whole AV-TEST team for the great work over the last 20 years! You all made this such a great event!

Maik Morgenstern retweeted

The @avtestorg Security Summit is underway and we are on the lookout for interesting IT security topics!
#cybersecruity #informationsecurity #cybercrime

Opened the @avtestorg Security Summit 2024 earlier today and just finished my talk about YARA. Spoiler: You still need EPP/EDR 😁
#100daysofyara #cybersecurity #endpointprotection – at Altstadt, Magdeburg

Scary stuff. Just checked our database at @avtestorg
for the latest WdBoot.sys drivers we know. Looks like the faulty driver (check the filesize!) was introduced Feb 6th 2024, v4.18.24010.7. Drivers before that look fine.


We collected all publicly reported cyber security incidents in Europa 2023 and put it into a report. Check it out! #threatintel #cybersecurity
Cyber-Incidents in Numbers: Year 2023 » av-test.org/en/news/cyber-in…
Since 2023, our team has dedicatedly collected and analyzed data on cyber incidents across Europe, with a particular focus on Germany.
#cybercrime #cybersecurity #internetsecurity #ransomware

Most comprehensive thread regarding the #lockbit takedown. If you have missed the show, read this thread.

